Third-Party Risk Management Best Practices
Organizations today depend on an extensive ecosystem of vendors, contractors, and service providers to operate effectively, from cloud infrastructure providers and software vendors to staffing ...
Latest stories, in-depth analysis & breaking updates
Organizations today depend on an extensive ecosystem of vendors, contractors, and service providers to operate effectively, from cloud infrastructure providers and software vendors to staffing ...
Modern software is rarely built from scratch. A typical application depends on hundreds of open-source libraries, third-party APIs, and vendor tools, each representing a potential entry point for a...
Supply Chain Attacks: The Hidden Threat Hiding in Your Software and Vendor Relationships Introduction When we think about cybersecurity threats, we typically envision attackers attempting to b...
IBM's X-Force Threat Intelligence Index 2026 has revealed a data point that should fundamentally reshape how organizations think about third-party risk: major supply chain and third-party breac...
Open-Source Authentication Library Backdoor Exposes 400+ SaaS Vendors in Latest Major Supply Chain Compromise A sophisticated supply chain attack discovered this week compromised more than 400 softwa...
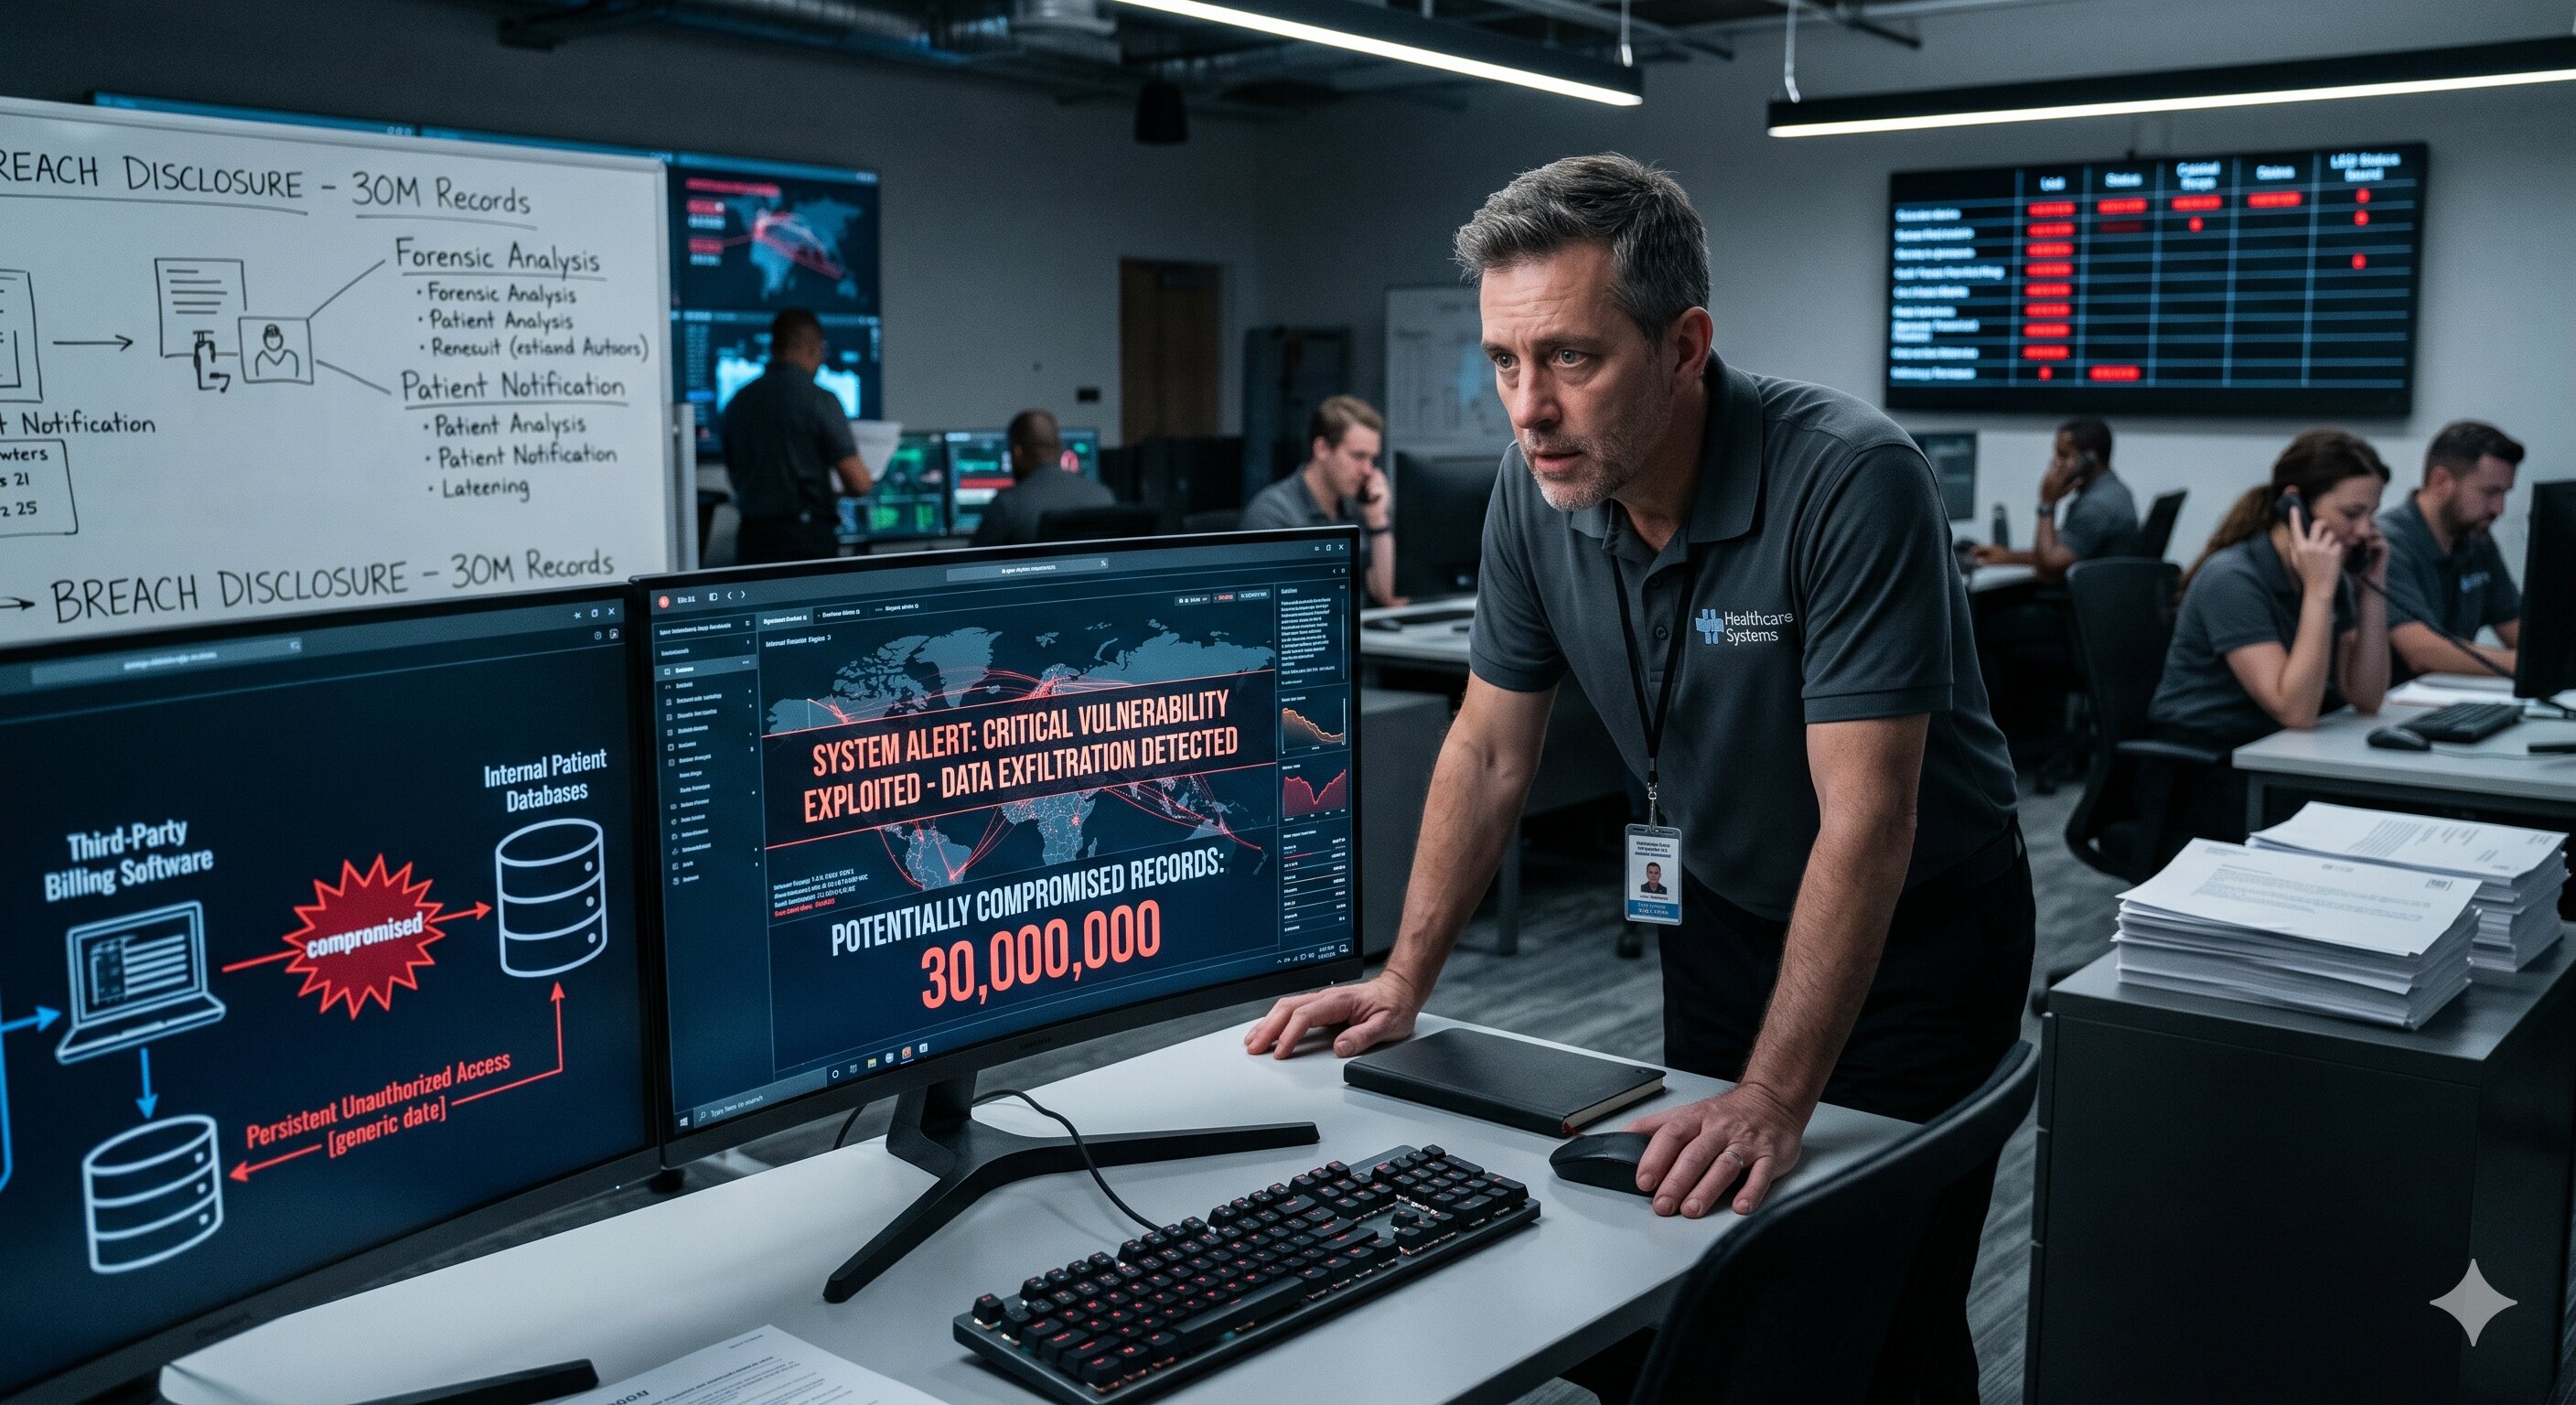
Healthcare Giant Reports Breach Affecting 30 Million Patient Records Category: Data Breaches One of the nation's largest healthcare providers has disclosed a massive data breach that exposed...