Third-Party Risk Management Best Practices
Organizations today depend on an extensive ecosystem of vendors, contractors, and service providers to operate effectively, from cloud infrastructure providers and software vendors to staffing ...
Latest stories, in-depth analysis & breaking updates
Organizations today depend on an extensive ecosystem of vendors, contractors, and service providers to operate effectively, from cloud infrastructure providers and software vendors to staffing ...
The software supply chain crisis has elevated the Software Bill of Materials from an obscure concept in software engineering to a mainstream security and compliance requirement. Government mand...
The regulatory landscape for cybersecurity has never been more complex or more consequential. Governments around the world are responding to the escalating frequency and severity of cyberattack...
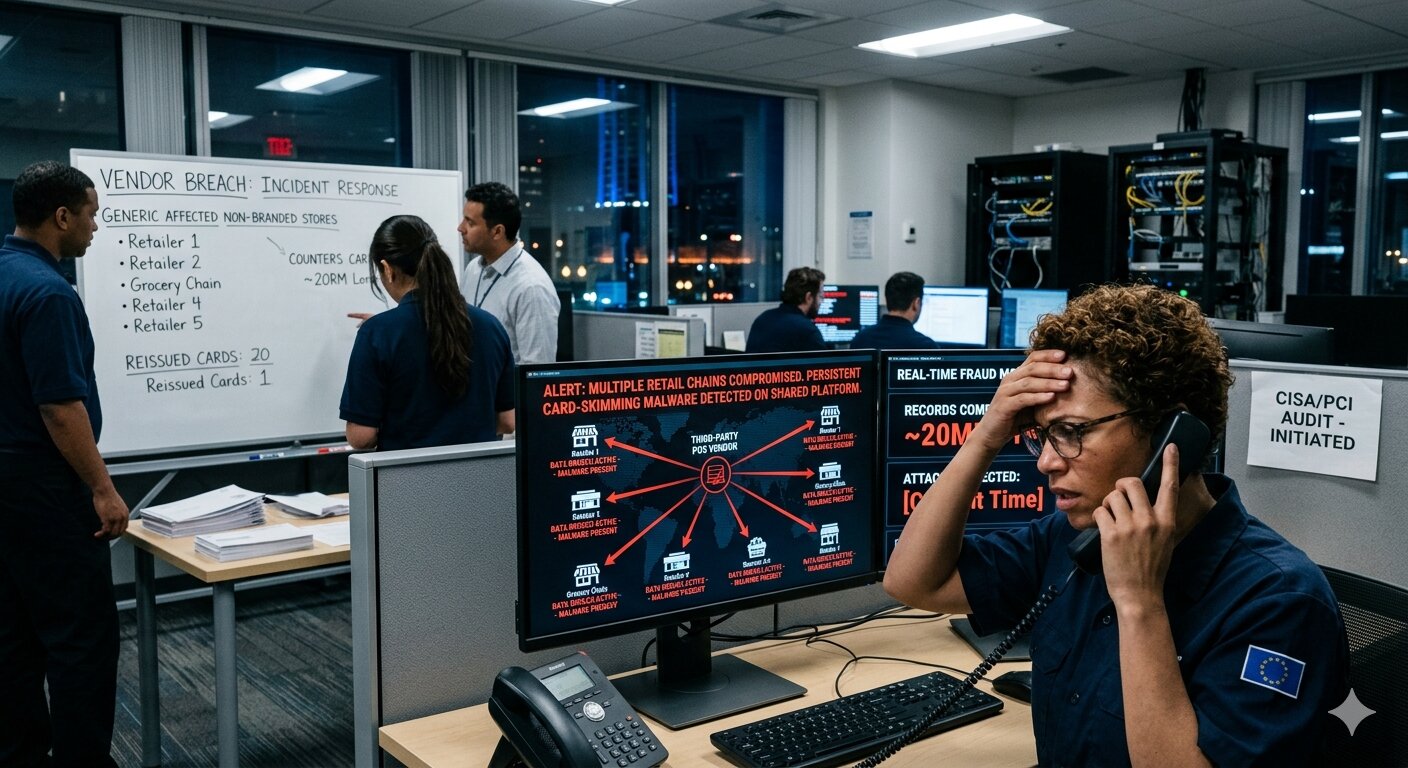
Third-Party Vendor Breach Hits Multiple Retail Chains Simultaneously Category: Data Breaches A data breach at a third-party point-of-sale technology vendor has simultaneously impacted more t...
Data privacy regulation has evolved considerably beyond its origins in giving individuals rights over their personal information, increasingly incorporating specific, detailed security mandates...
Low-code and no-code development platforms have democratized application building, enabling employees outside traditional engineering roles to create functional business applications, automate ...
Modern software applications are rarely built entirely from scratch; instead, they are assembled from a complex web of open-source libraries, third-party frameworks, and reusable components, of...
Supply chain attacks have quietly become one of the most consequential categories of cyber risk facing modern organizations, and the numbers tell a stark story. Incidents involving compromised ...
Cyber insurance has evolved from a niche product to a mainstream risk transfer mechanism, and in 2026 it is a standard component of enterprise risk management programs. The surge in ransomware ...
The software supply chain has become one of the most attractive and devastating attack surfaces in modern cybersecurity. High-profile incidents involving widely-used software components and man...