
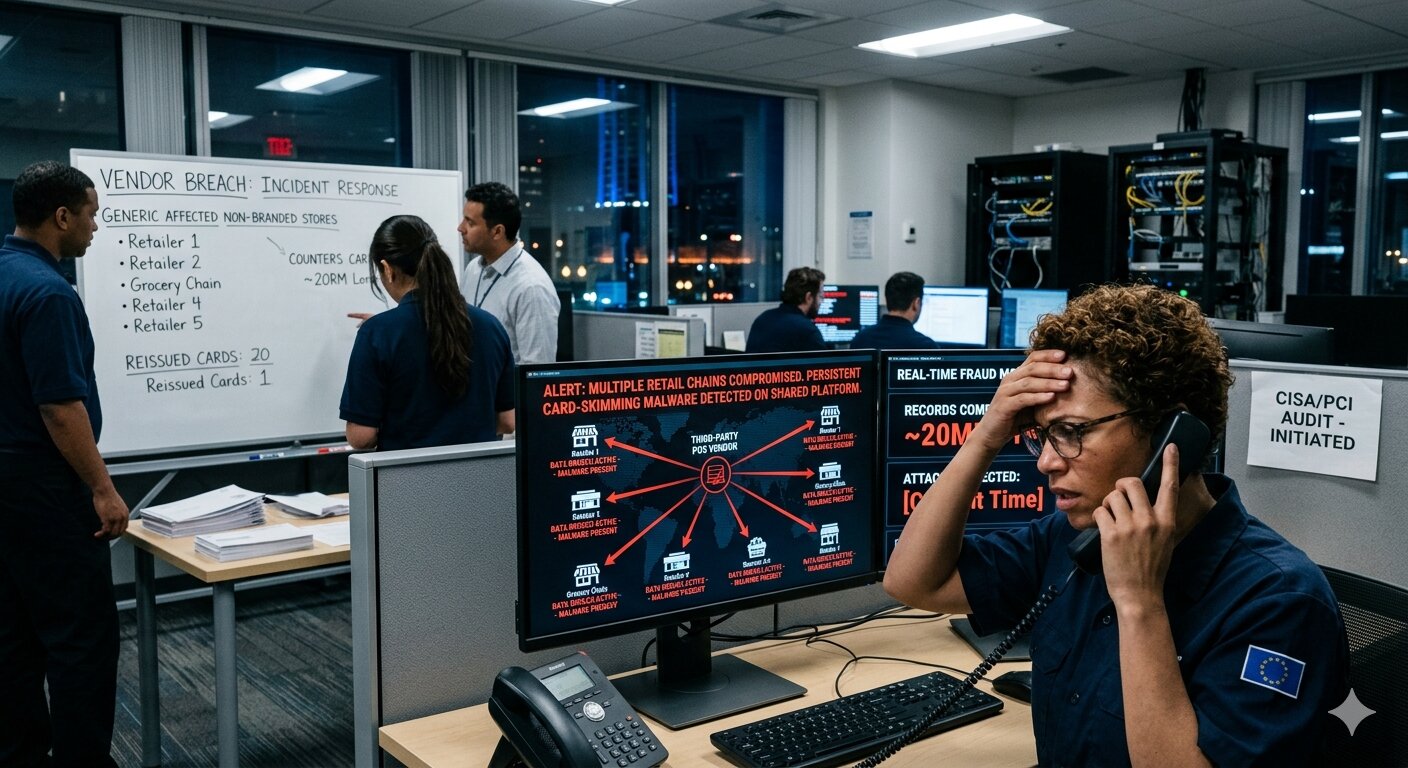
Third-Party Vendor
Breach Hits Multiple Retail Chains Simultaneously
Category:
Data Breaches
A data breach
at a third-party point-of-sale technology vendor has simultaneously impacted
more than a dozen major retail chains, exposing the payment card data of an
estimated 20 million customers. The incident highlights the systemic risk that
third-party vendors pose to large organizations that rely on shared technology
platforms.
The vendor,
which provides payment processing software to retailers across multiple
industries, was compromised through a sophisticated attack that implanted
card-skimming malware on its platform. The malware silently captured credit and
debit card information — including card numbers, expiration dates, and CVV
codes — as transactions were processed in real time.
The breach
was discovered when banks began noticing an unusually high rate of fraudulent
transactions on cards that had a common point of purchase across the affected
retail chains. A forensic investigation traced the fraud back to the shared
vendor platform within days.
"This is
a textbook example of why third-party risk management is so critical,"
said a payment security expert. "When retailers outsource payment
processing, they are effectively trusting the vendor's security posture to
protect their customers."
All affected
retailers have been notified and are working with the vendor to remove the
malware and secure their systems. Card issuers are in the process of reissuing
millions of cards as a precaution. Regulators are also scrutinizing the
vendor's security practices and may impose significant fines for non-compliance
with payment card industry security standards.





Comments