
State-Sponsored
Hackers Breach Defense Contractor's Internal Systems
Category:
Threats & Attacks
A major
defense contractor has confirmed that state-sponsored hackers breached its
internal systems, gaining access to sensitive project files, employee
information, and potentially classified research data. The breach, attributed
with high confidence to a hacking group affiliated with a foreign government,
is being described as one of the most serious espionage incidents targeting the
defense sector in years.
The attackers
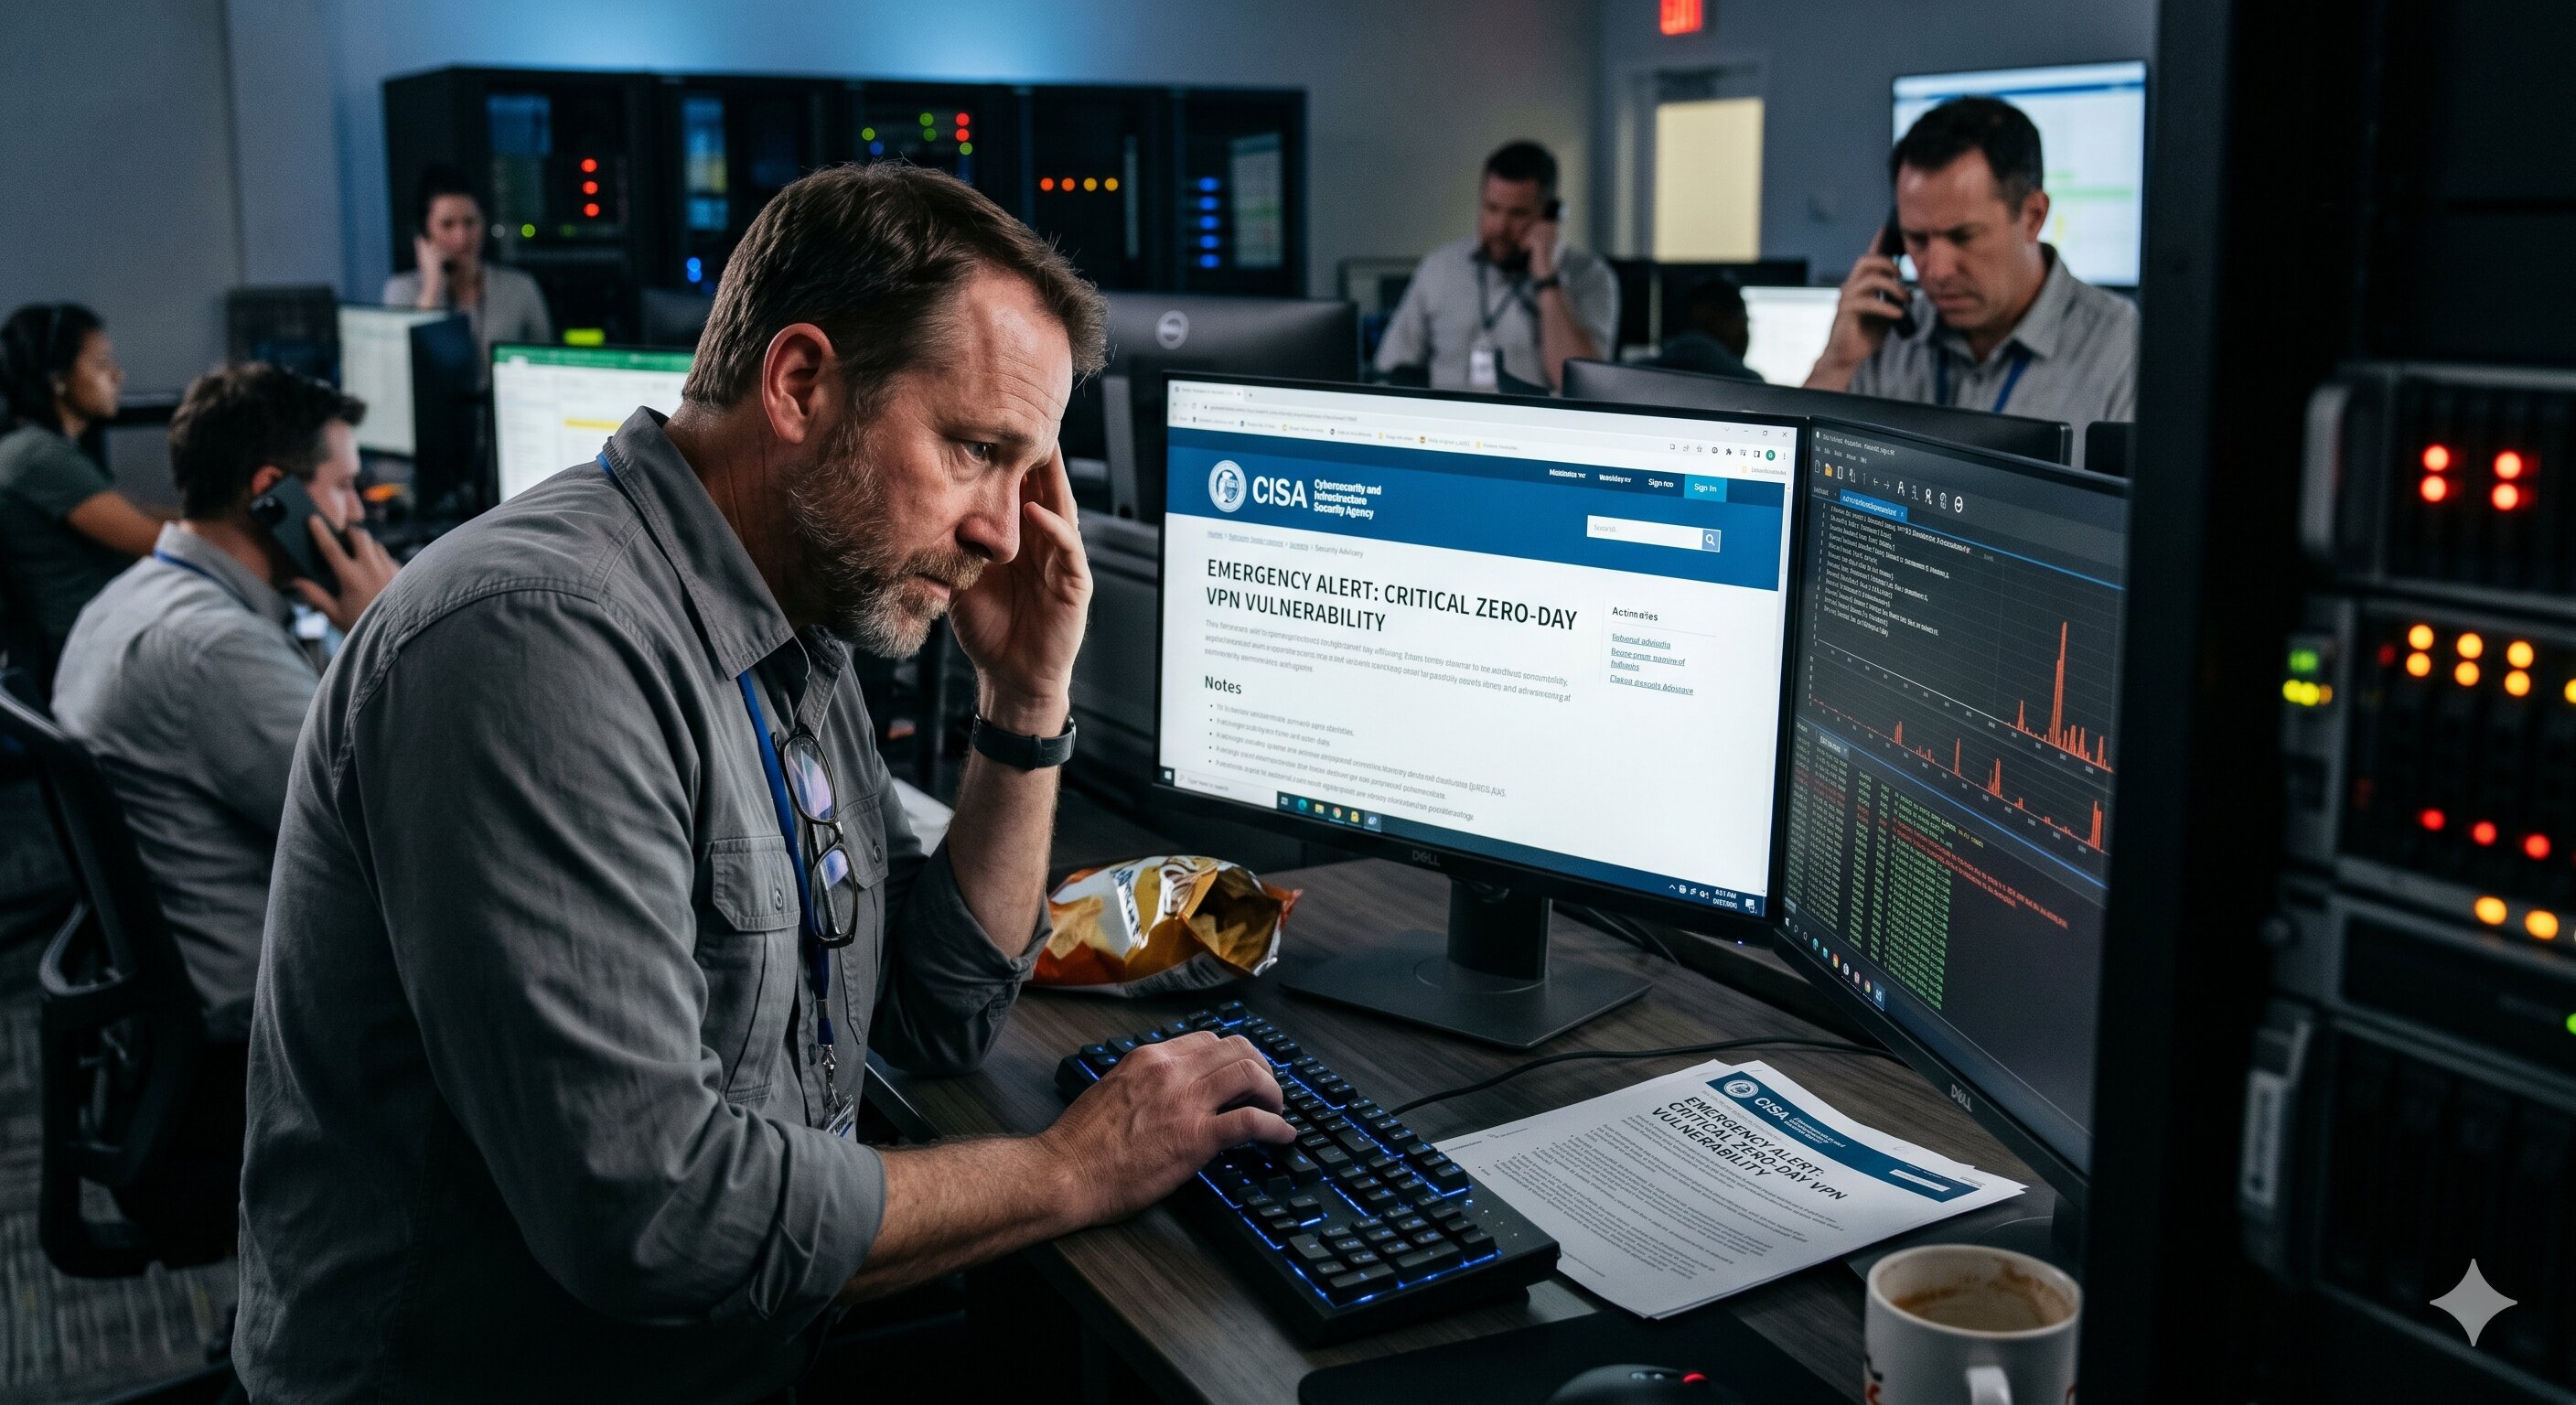
used a combination of spear-phishing emails and a previously unknown exploit in
a widely used remote access tool to infiltrate the company's network. Once
inside, they deployed custom malware designed to evade detection and maintained
persistent access for an estimated four months before being discovered.
"The
level of patience and sophistication shown by this threat actor is
characteristic of nation-state operations," said a senior analyst at a
federal cybersecurity agency. "They weren't just looking for a quick
payday — they were after intellectual property and strategic
intelligence."
The
contractor, which holds contracts with multiple government agencies, has
notified federal authorities and is cooperating fully with ongoing
investigations. The full scope of the data accessed remains under review.
Officials have not ruled out the possibility that classified information was
exfiltrated.
This incident
has reignited calls in Washington for stricter cybersecurity requirements for
all contractors working with the federal government, including mandatory
incident reporting timelines and enhanced network monitoring standards.





Comments