
Major Airline Suffers
Data Breach; Passport Details at Risk
Category:
Data Breaches
A major
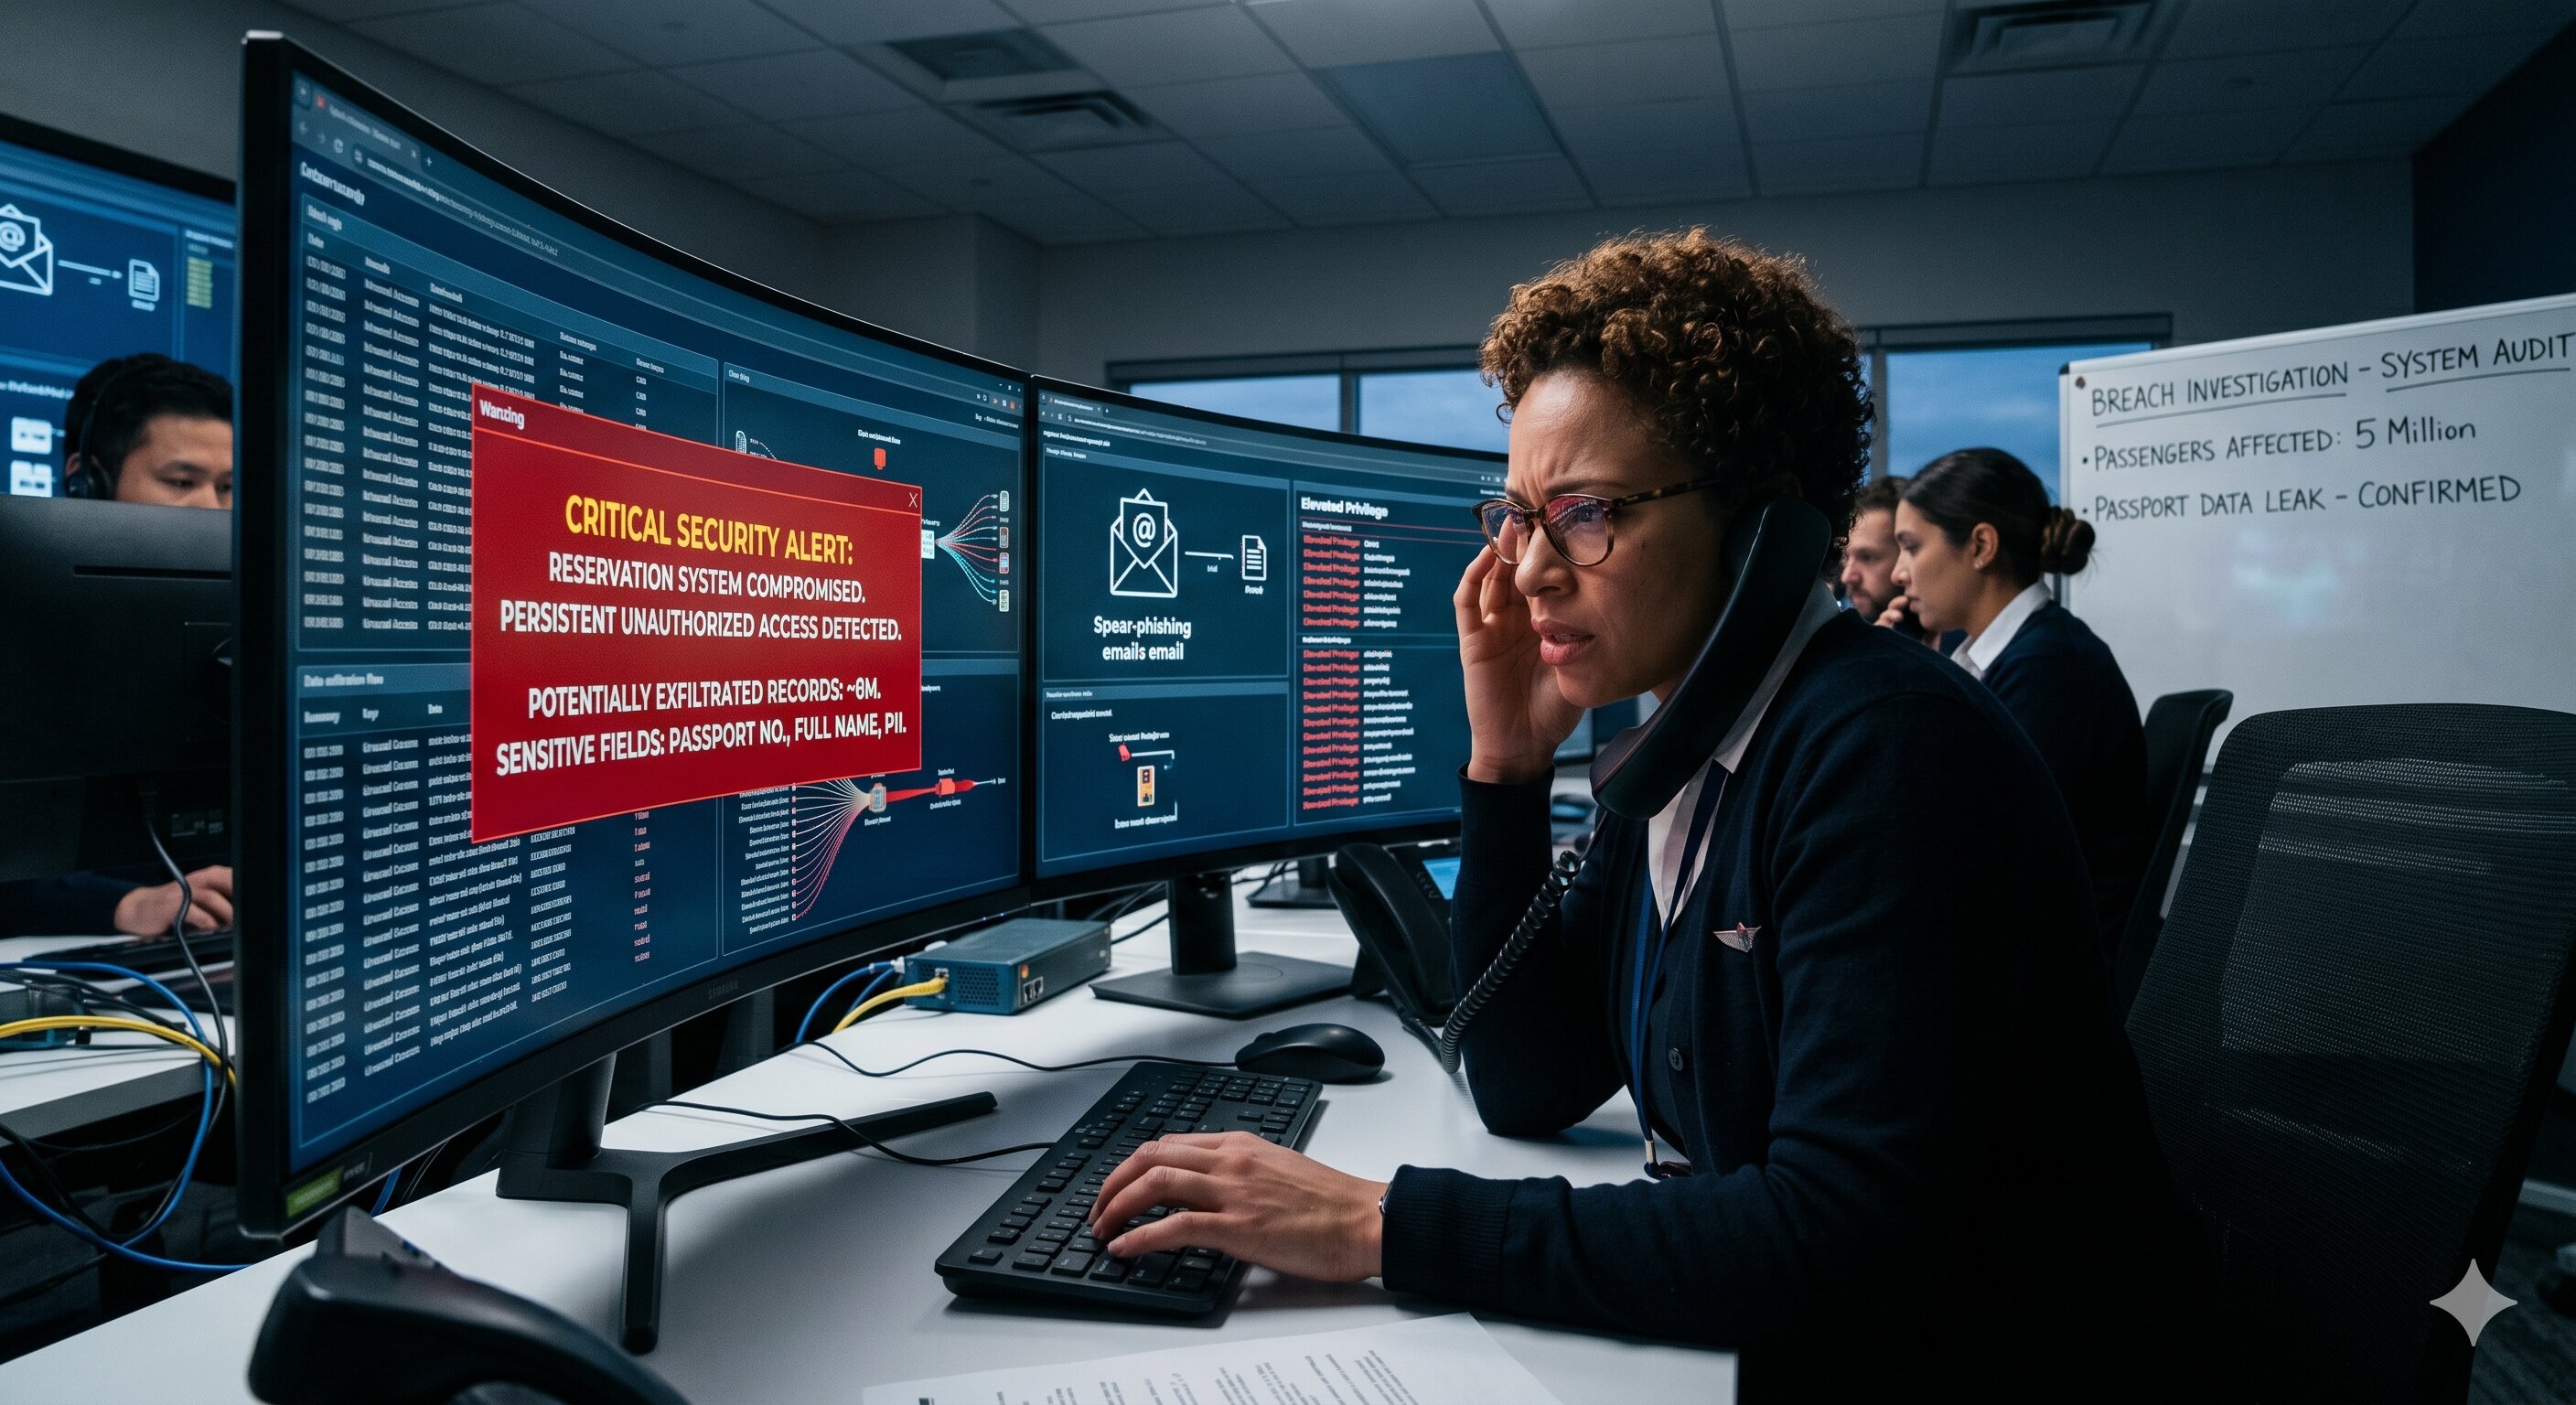
international airline has reported a data breach that may have exposed the
passport details, travel itineraries, frequent flyer account information, and
partial payment data of up to 5 million passengers. The breach was caused by an
intrusion into the airline's reservation system and went undetected for
approximately three weeks.
The airline
discovered the breach when its security operations center detected unusual data
access patterns during a routine audit. By the time the intrusion was
identified, the attackers had already extracted a significant volume of
records. Forensic analysis suggests the breach began with a spear-phishing
email targeting an employee with elevated system privileges.
Passport data
is particularly valuable to cybercriminals and nation-state actors, as it can
be used to create fraudulent identity documents, facilitate human trafficking,
or assist in targeted espionage operations. The airline is working closely with
law enforcement agencies in multiple countries to investigate the incident.
"The
exposure of passport information takes this breach to a different level of
severity," said a cybersecurity expert specializing in identity theft.
"Unlike a compromised credit card, you cannot simply cancel your passport
and get a new number assigned. The consequences can follow victims for
years."
Affected
passengers are being notified and advised to monitor their accounts for
suspicious activity. The airline is also implementing enhanced security
measures across its reservation systems, including multi-factor authentication
and additional encryption for sensitive data fields.





Comments