
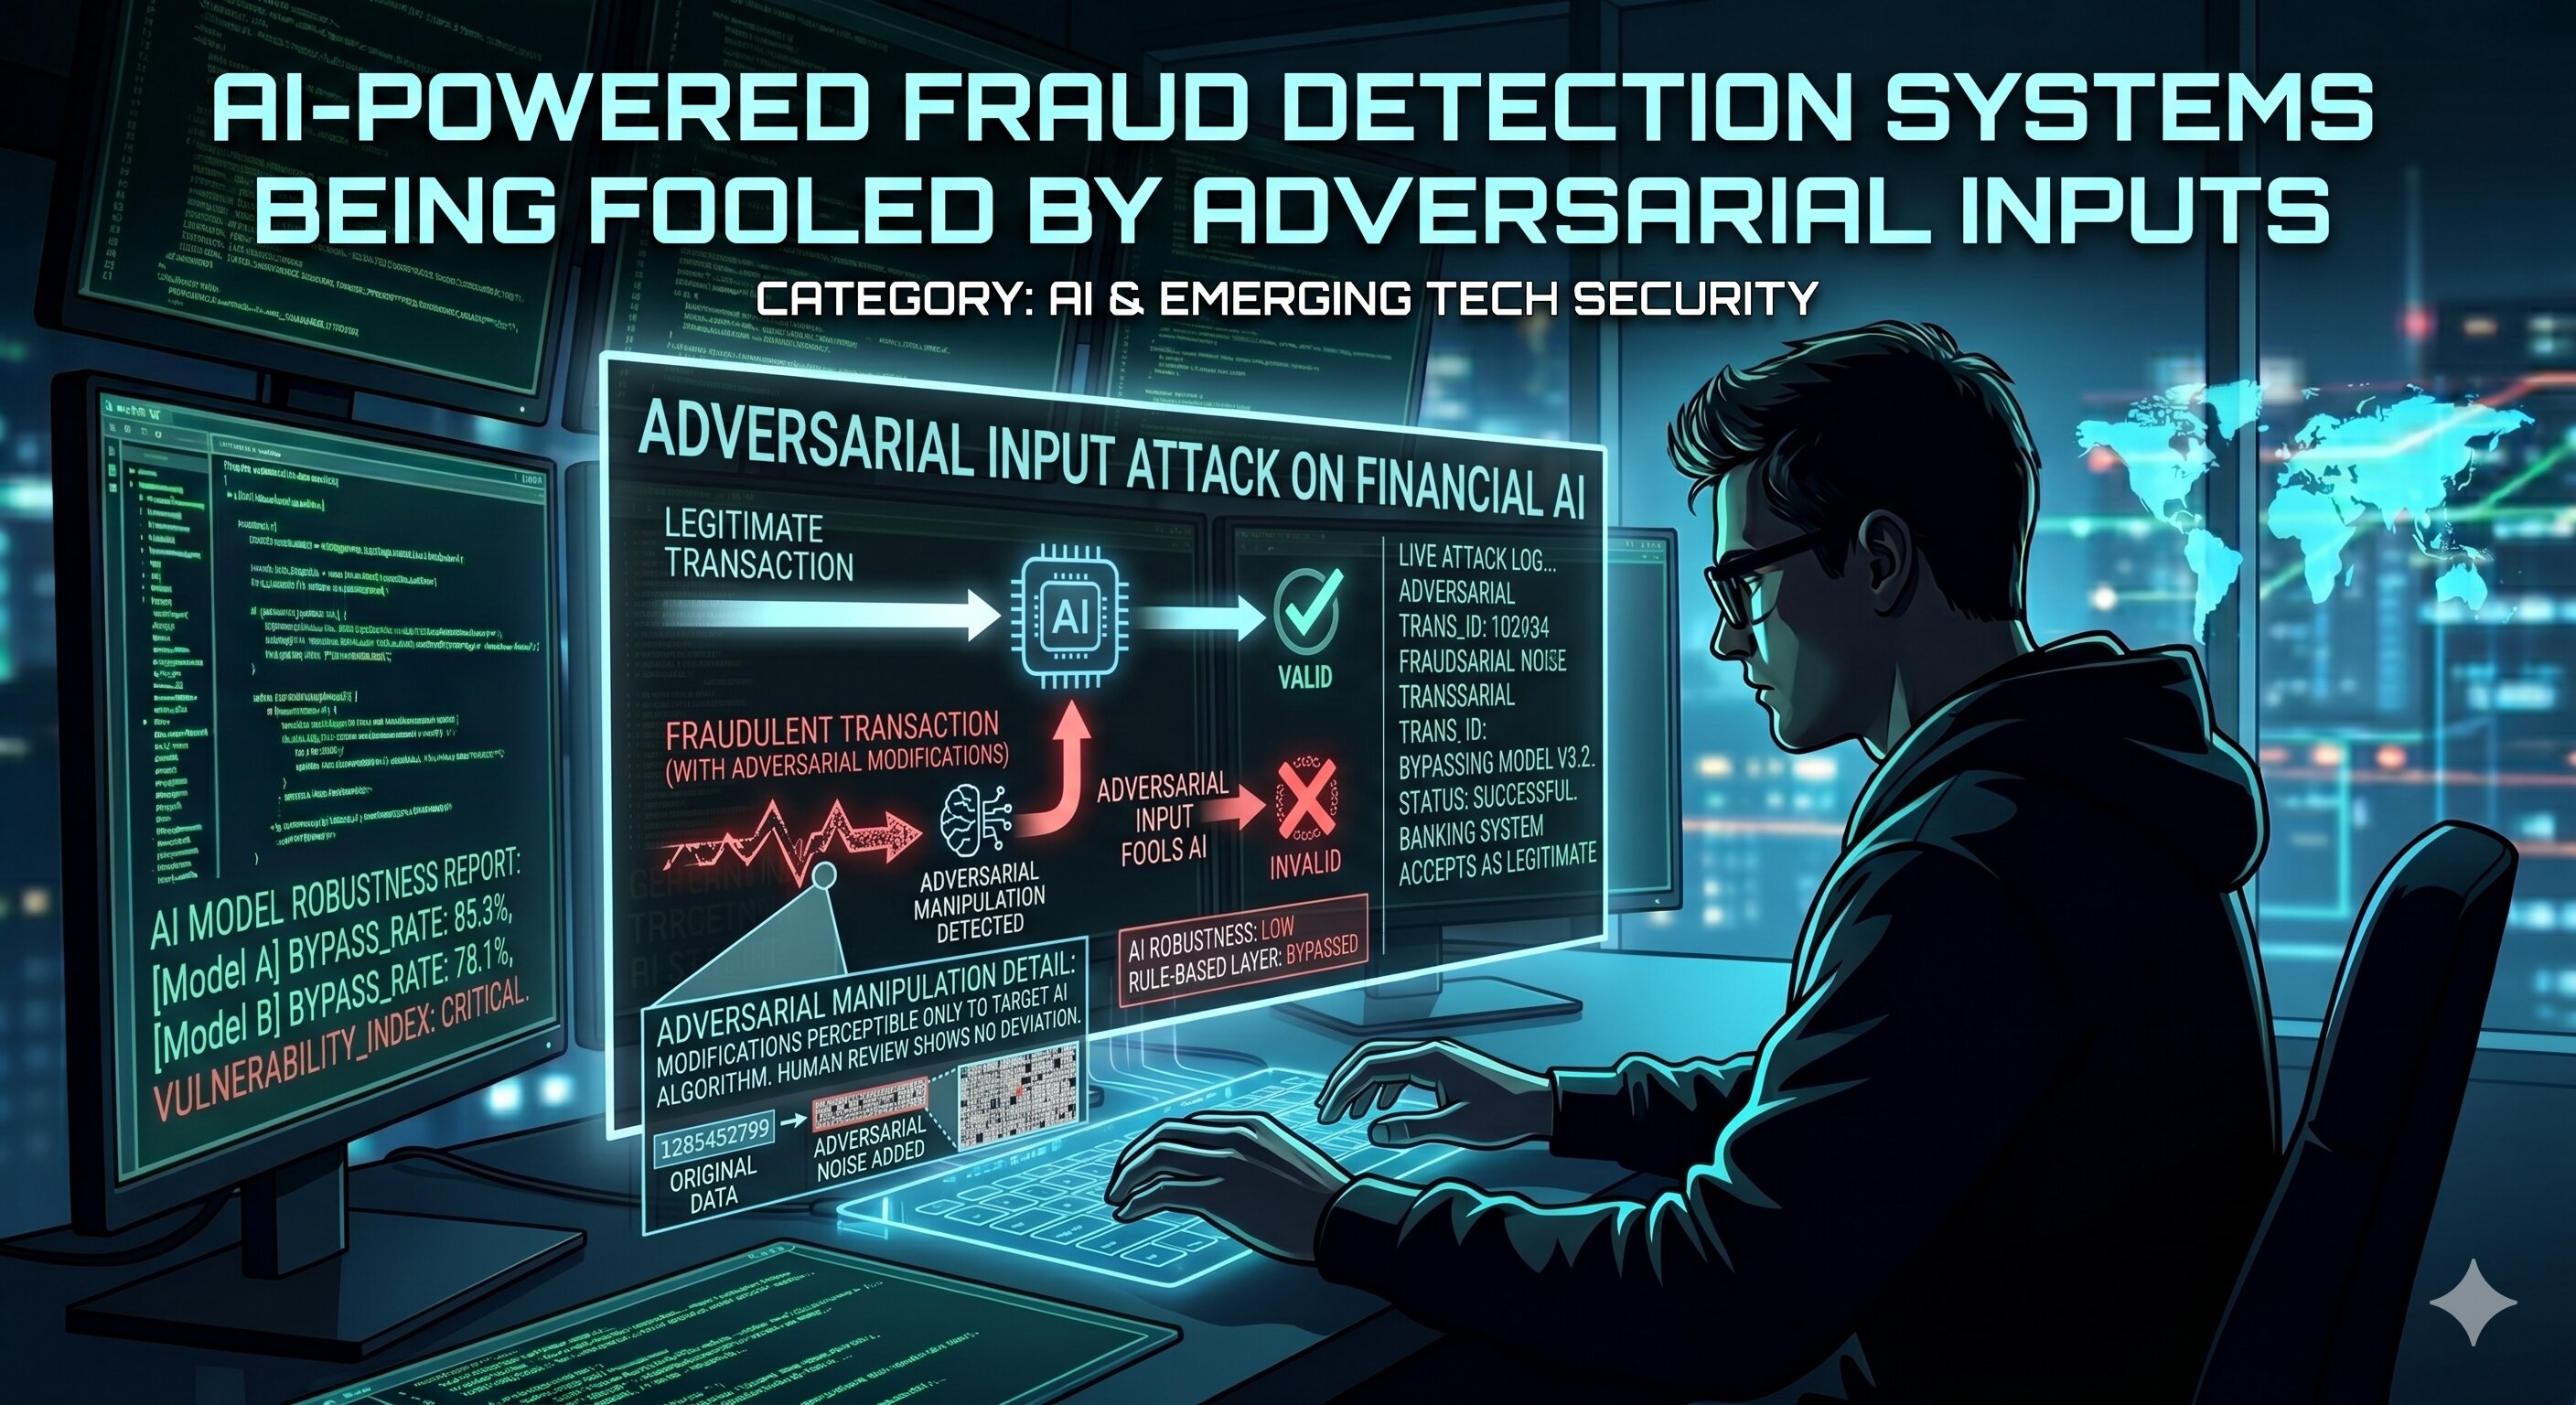
AI-Powered Fraud
Detection Systems Being Fooled by Adversarial Inputs
Category:
AI & Emerging Tech Security
Cybersecurity
researchers have demonstrated that artificial intelligence systems used by
banks and financial institutions to detect fraud can be systematically fooled
through the use of adversarial inputs — carefully crafted data designed to
deceive machine learning models while appearing entirely normal to human
reviewers.
In tests
conducted with the cooperation of several financial institutions, the research
team showed that by making subtle, algorithmically calculated modifications to
fraudulent transactions, they could cause AI fraud detection systems to
classify them as legitimate with a high degree of reliability. The
modifications were imperceptible to human analysts reviewing the same
transactions.
"The
financial sector has invested heavily in AI-powered fraud detection, and these
systems have undoubtedly reduced fraud losses," said Dr. Michael Okafor,
who led the research team. "But adversaries are now learning to attack the
AI itself, not just the transactions it monitors. This is a new frontier in
financial cybercrime."
The findings
are particularly concerning given the growing sophistication of criminal
organizations and their demonstrated ability to rapidly adopt new techniques.
Security researchers believe that adversarial attacks against financial AI
systems may already be occurring in the wild, though they are difficult to
detect by definition.
Financial
institutions are being urged to invest in AI robustness testing, to combine AI
detection with rule-based systems and human review, and to continuously monitor
the performance of their detection models for signs of adversarial
manipulation.




Comments