Securing the Software Supply Chain with SBOMs
Modern software applications are rarely built entirely from scratch; instead, they are assembled from a complex web of open-source libraries, third-party frameworks, and reusable components, of...
Latest stories, in-depth analysis & breaking updates
Modern software applications are rarely built entirely from scratch; instead, they are assembled from a complex web of open-source libraries, third-party frameworks, and reusable components, of...
The software supply chain has become one of the most attractive and devastating attack surfaces in modern cybersecurity. High-profile incidents involving widely-used software components and man...
Supply Chain Attacks: The Hidden Threat Hiding in Your Software and Vendor Relationships Introduction When we think about cybersecurity threats, we typically envision attackers attempting to b...
Supply Chain Attacks Quadruple Over Five Years, IBM X-Force Report Reveals The IBM X-Force Threat Intelligence Index 2026 has revealed a staggering trend: major supply chain and third-party b...
Organizations today depend on an extensive ecosystem of vendors, contractors, and service providers to operate effectively, from cloud infrastructure providers and software vendors to staffing ...
Machine Learning (ML) is becoming an essential component of modern risk management strategies, enabling organizations to identify potential threats, assess vulnerabilities, and make more informed deci...
A landmark study examining the security quality of code generated by leading AI coding assistants has found that approximately 40% of generated code contains security vulnerabilities, with ...
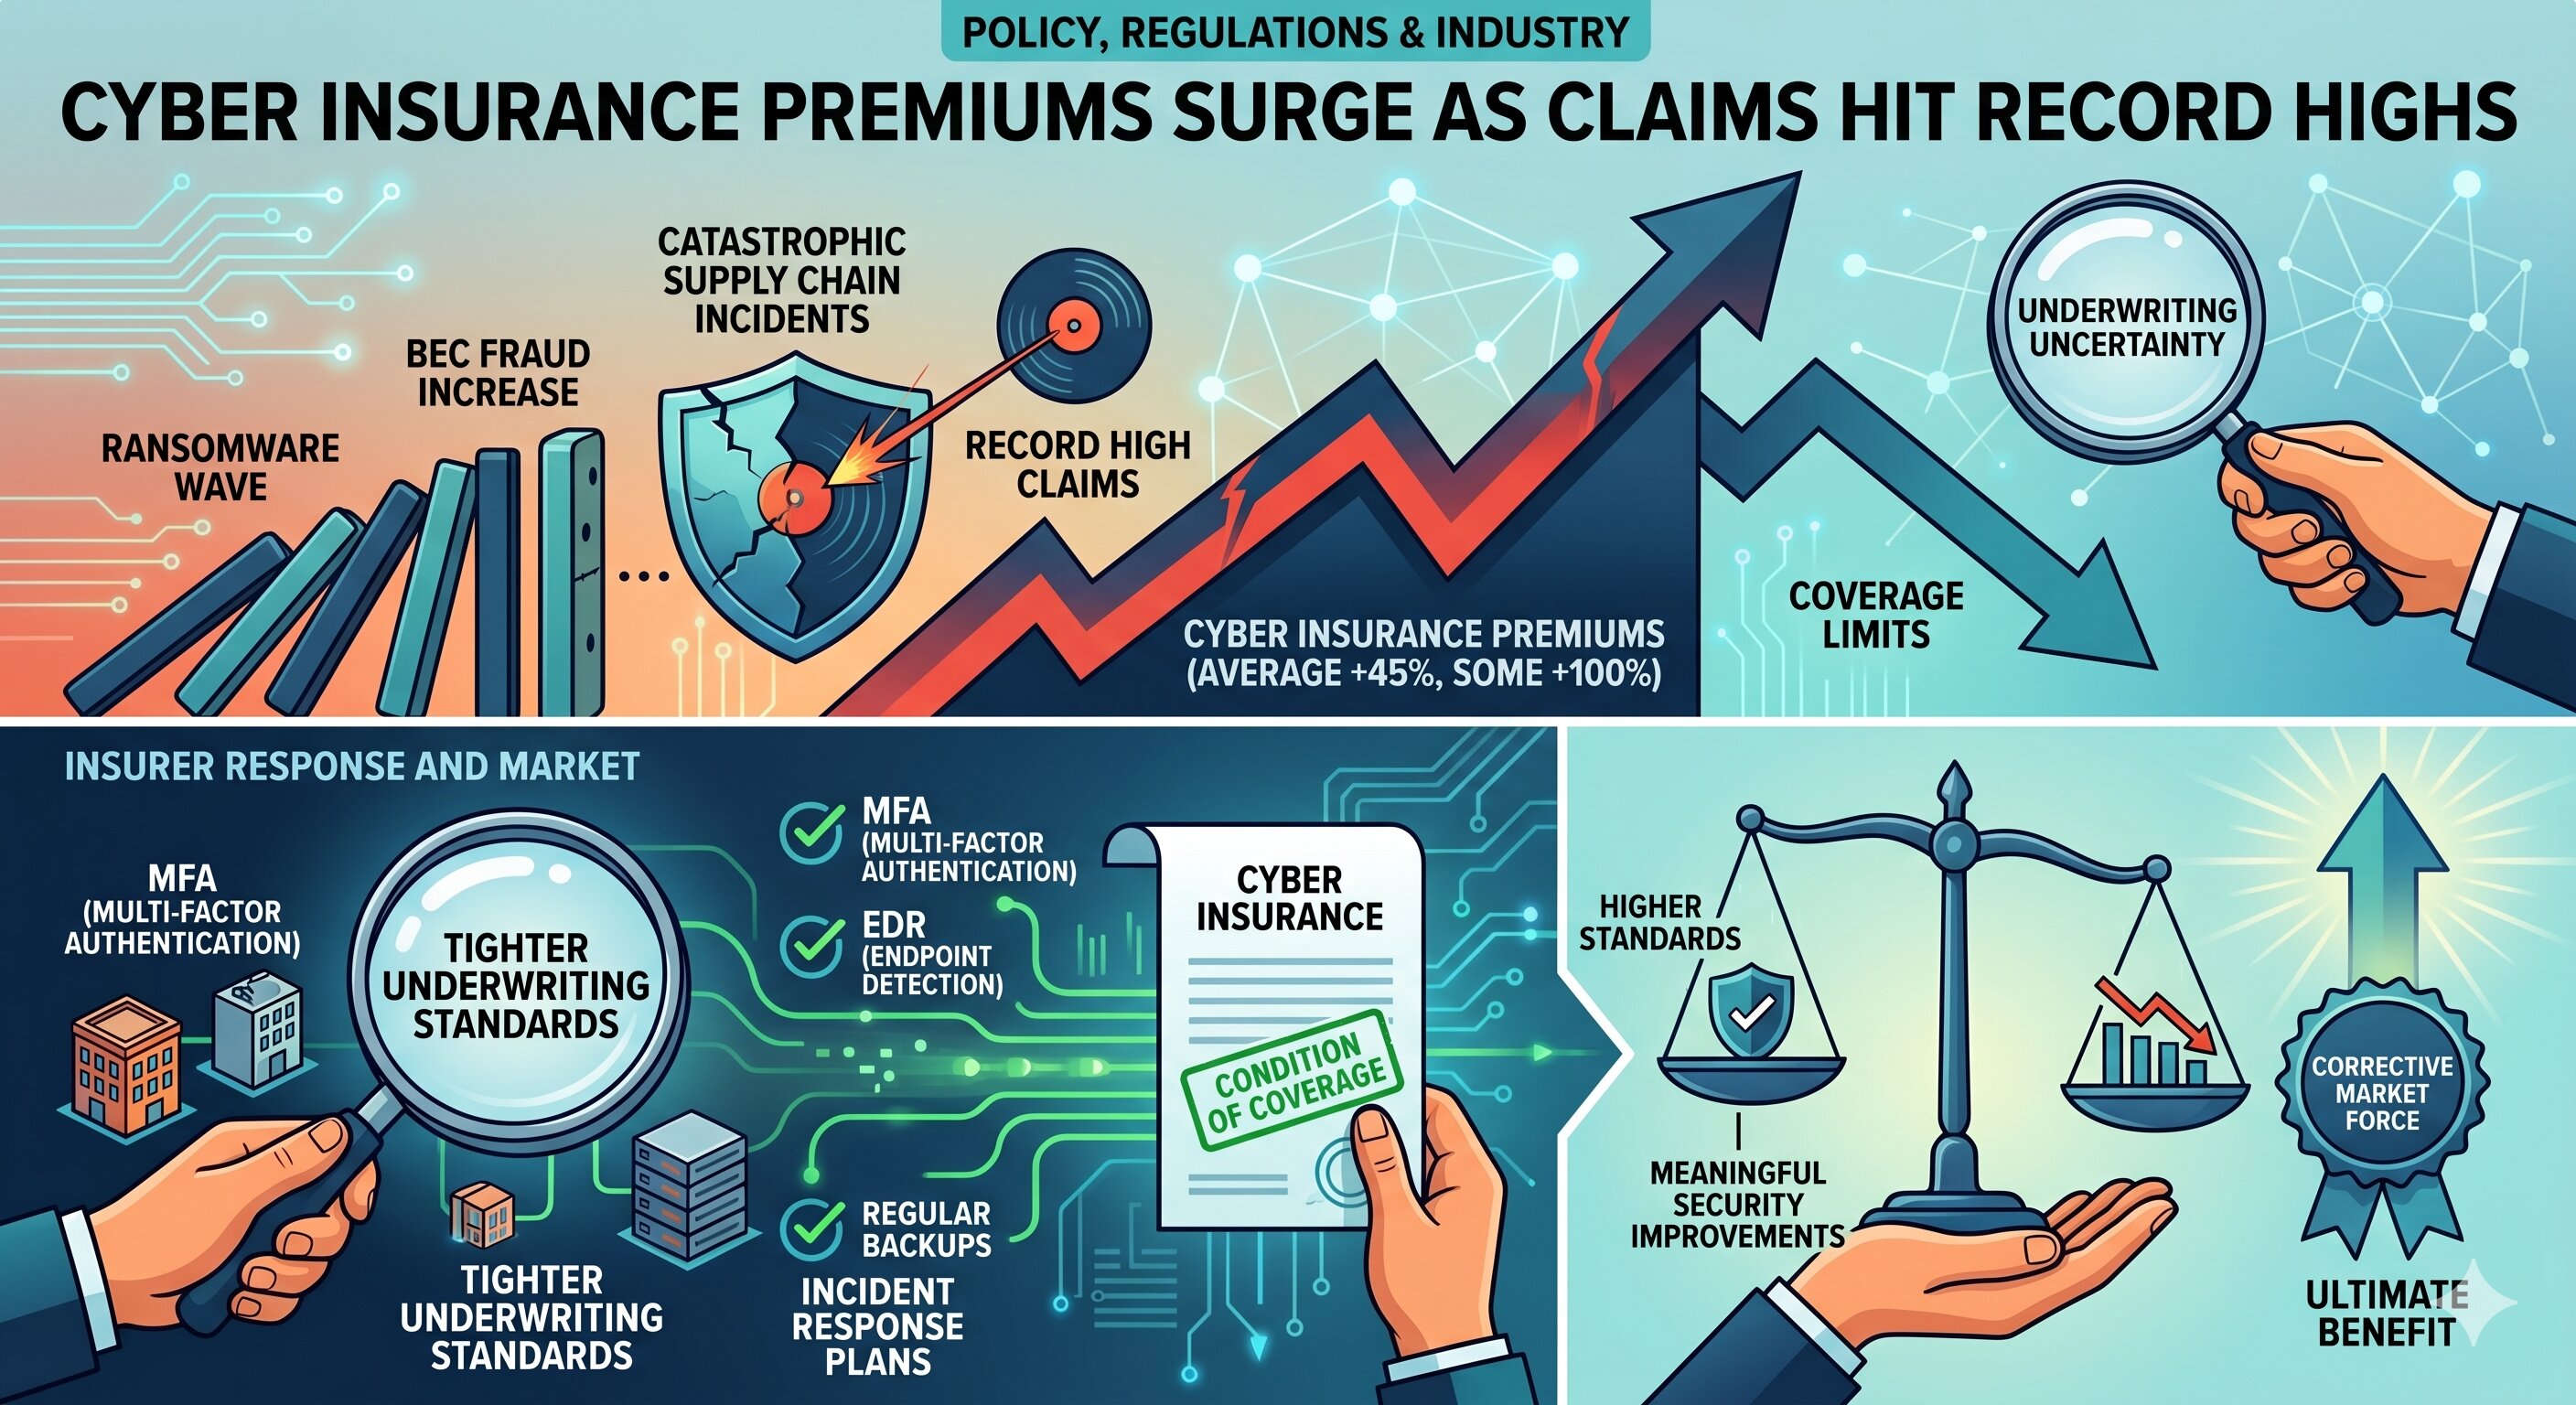
Cyber Insurance Premiums Surge as Claims Hit Record Highs Category: Policy, Regulations & Industry The cyber insurance market is experiencing unprecedented turbulence, with premiums risin...
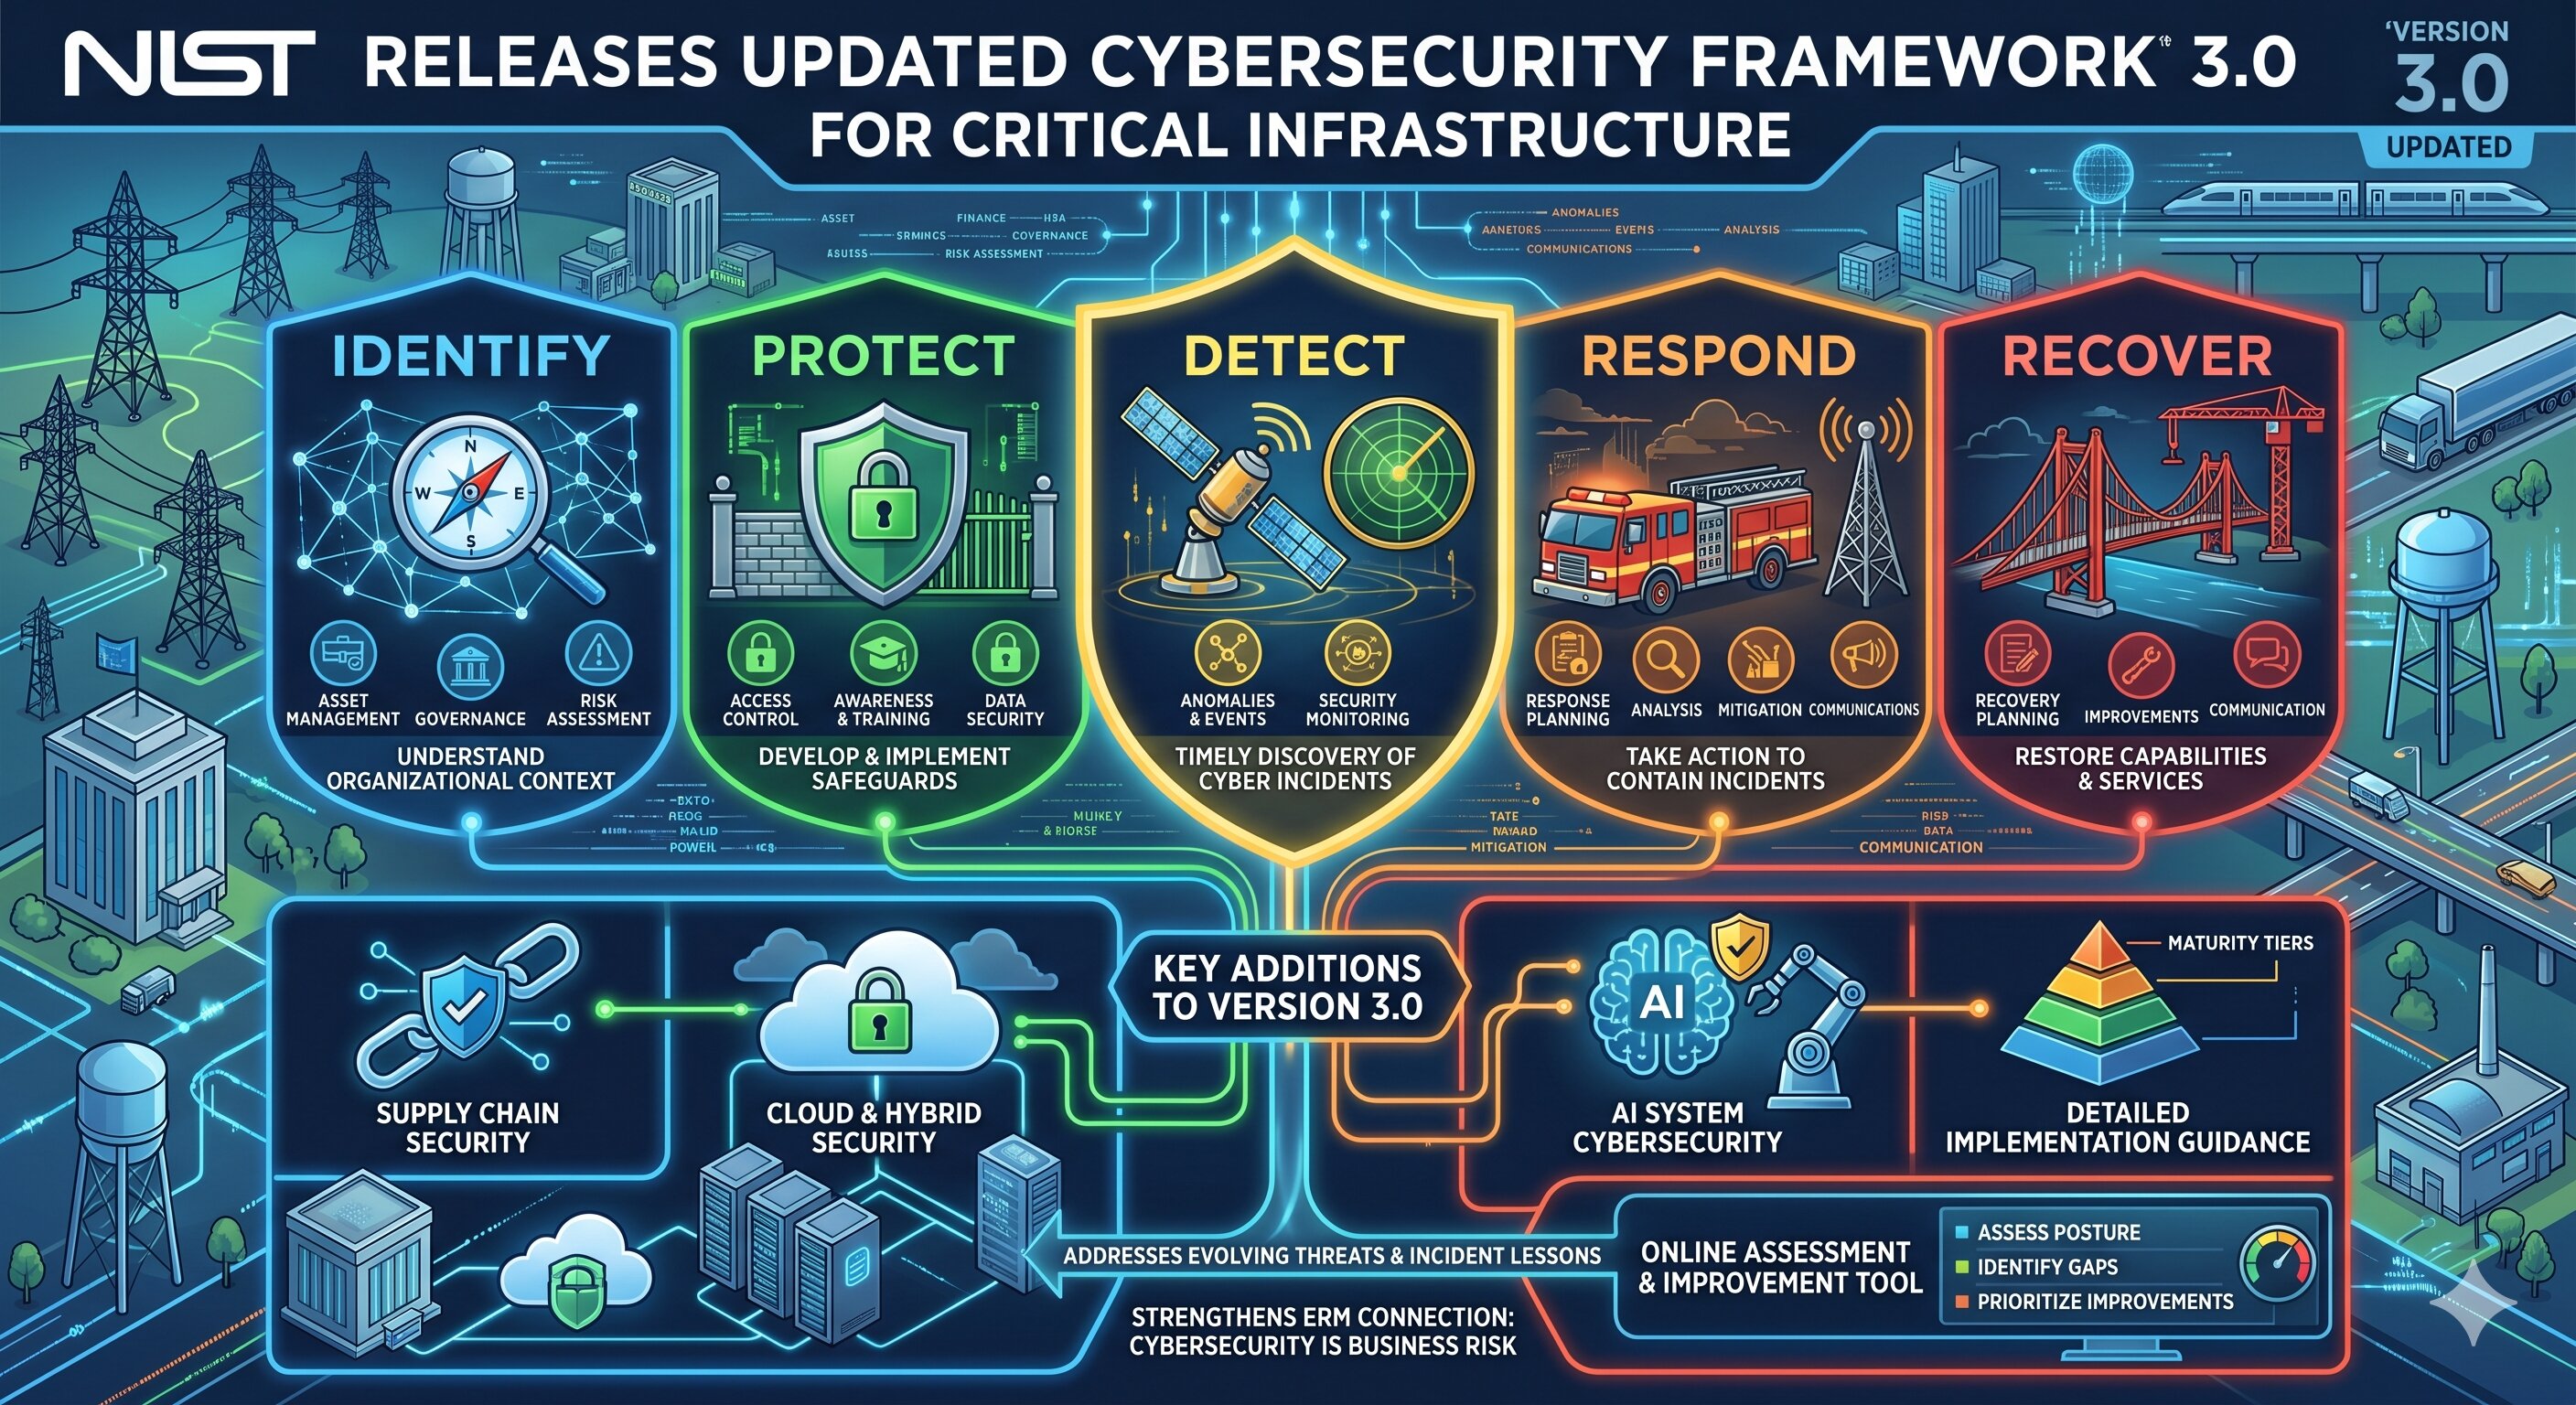
NIST Releases Updated Cybersecurity Framework 3.0 for Critical Infrastructure Category: Policy, Regulations & Industry The National Institute of Standards and Technology has published the...