
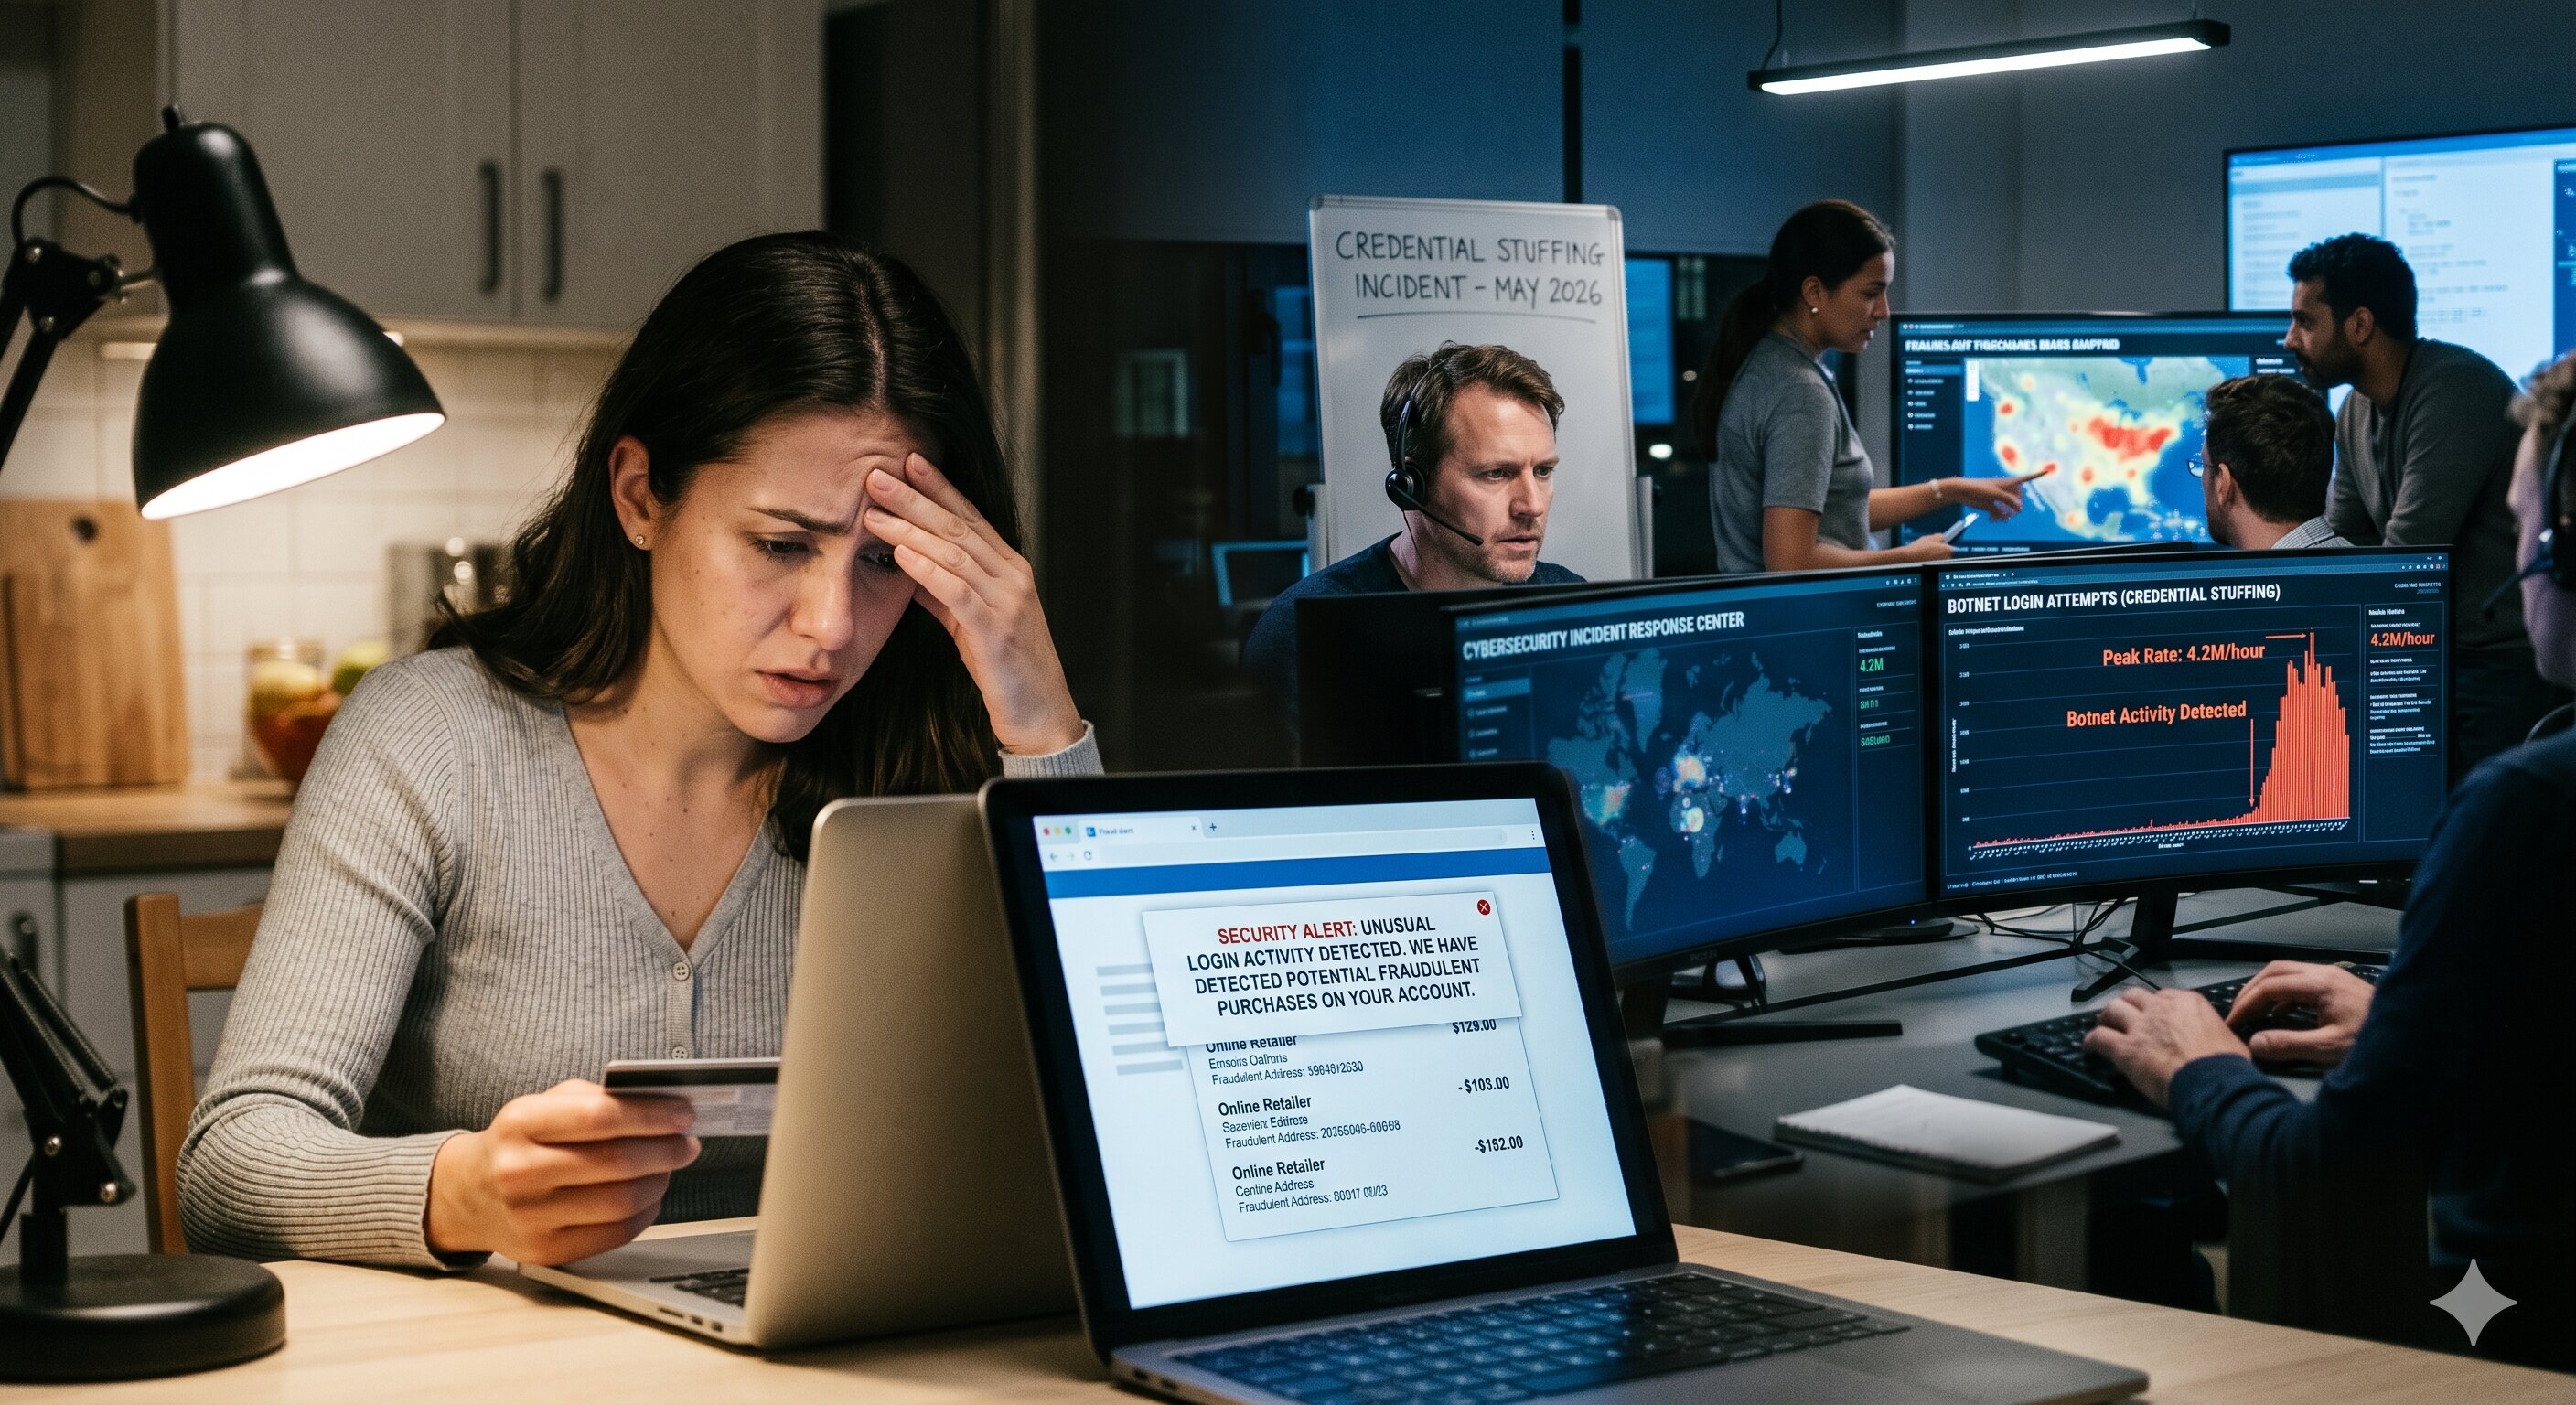
Credential Stuffing
Attack Exposes 10 Million User Accounts
Category:
Threats & Attacks
A large-scale
credential stuffing attack has compromised approximately 10 million user
accounts across a popular online retail platform, according to a security
disclosure released by the company. The attackers used automated tools to test
billions of username and password combinations sourced from previously leaked
databases, successfully gaining access to accounts where users had reused
passwords.
The attack
unfolded over several days, with bots attempting millions of logins per hour.
While the platform's security team detected unusual login activity early in the
campaign, it took additional time to fully block the attack and identify the
scope of accounts affected.
Compromised
accounts were subsequently used to make fraudulent purchases, steal stored
payment information, and access linked loyalty points and gift card balances.
The total financial damage is estimated to be in the millions of dollars.
"Credential
stuffing remains one of the most prevalent and damaging attack techniques
because it exploits a very human habit — reusing passwords," said
cybersecurity analyst James Thornton. "No amount of server-side security
can fully protect accounts if users are using the same password across multiple
sites."
The company
has reset passwords for all affected accounts and is implementing more
aggressive bot detection measures, including CAPTCHA challenges and rate
limiting. All users are being strongly advised to use unique, strong passwords
for every account and to enable two-factor authentication wherever available.





Comments