
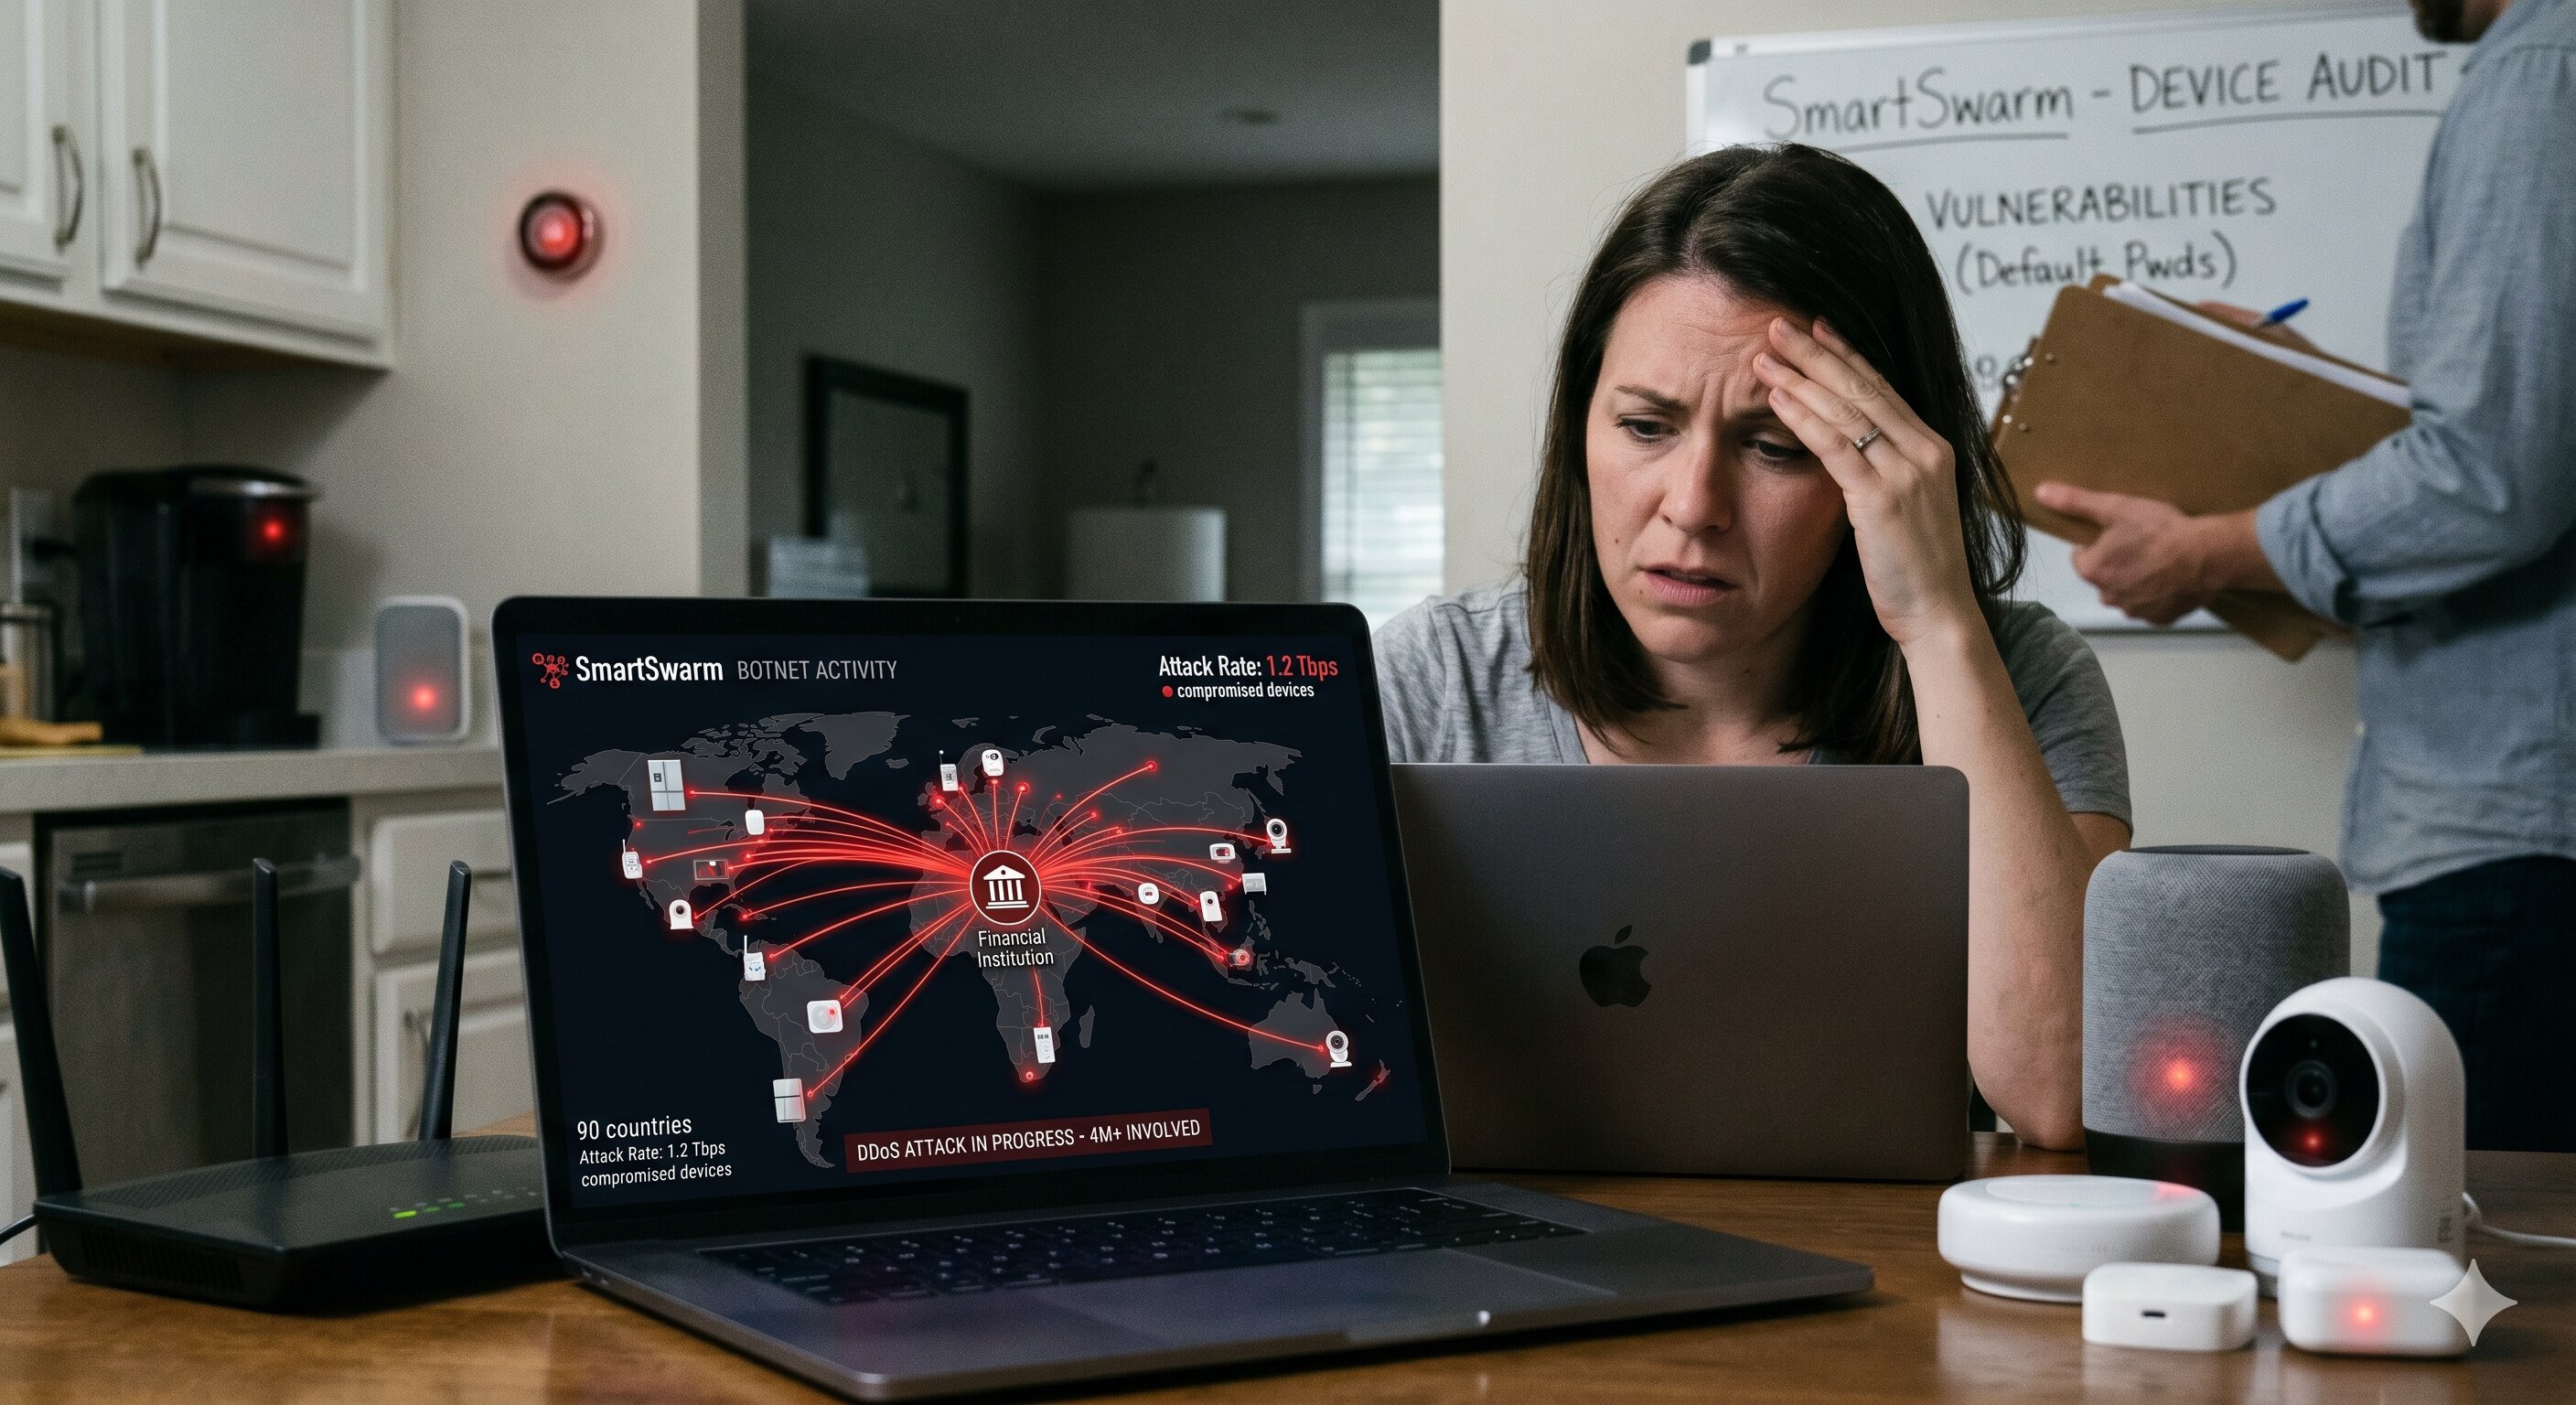
Hackers Exploit Smart
Home Devices to Build Massive Botnet
Category:
Threats & Attacks
A
cybersecurity firm has uncovered a massive botnet built almost entirely from
compromised smart home devices, including internet-connected refrigerators,
baby monitors, smart thermostats, and home security cameras. The botnet, named
"SmartSwarm" by researchers, consists of more than 4 million infected
devices across 90 countries and is being rented to cybercriminals for use in
DDoS attacks and spam campaigns.
The devices
were compromised by exploiting default factory passwords and unpatched firmware
vulnerabilities. Many of the affected devices had never received a security
update since they were manufactured, making them easy targets for automated
scanning tools used by the botnet operators.
"The
Internet of Things has created an enormous attack surface that the security
industry has struggled to keep pace with," said cybersecurity researcher
Nina Larsson. "These devices are often designed with convenience in mind
and security as an afterthought."
The botnet
has been used in at least 40 DDoS attacks against gaming platforms, financial
institutions, and news websites over the past three months. In some cases, the
attacks generated traffic volumes sufficient to take down enterprise-grade
infrastructure.
Security
experts are calling on device manufacturers to implement mandatory security
standards, including unique factory passwords, automatic firmware updates, and
a clearly defined end-of-life support window. In the meantime, consumers are
advised to regularly update their devices, change default passwords, and
consider placing IoT devices on a separate network segment.





Comments