
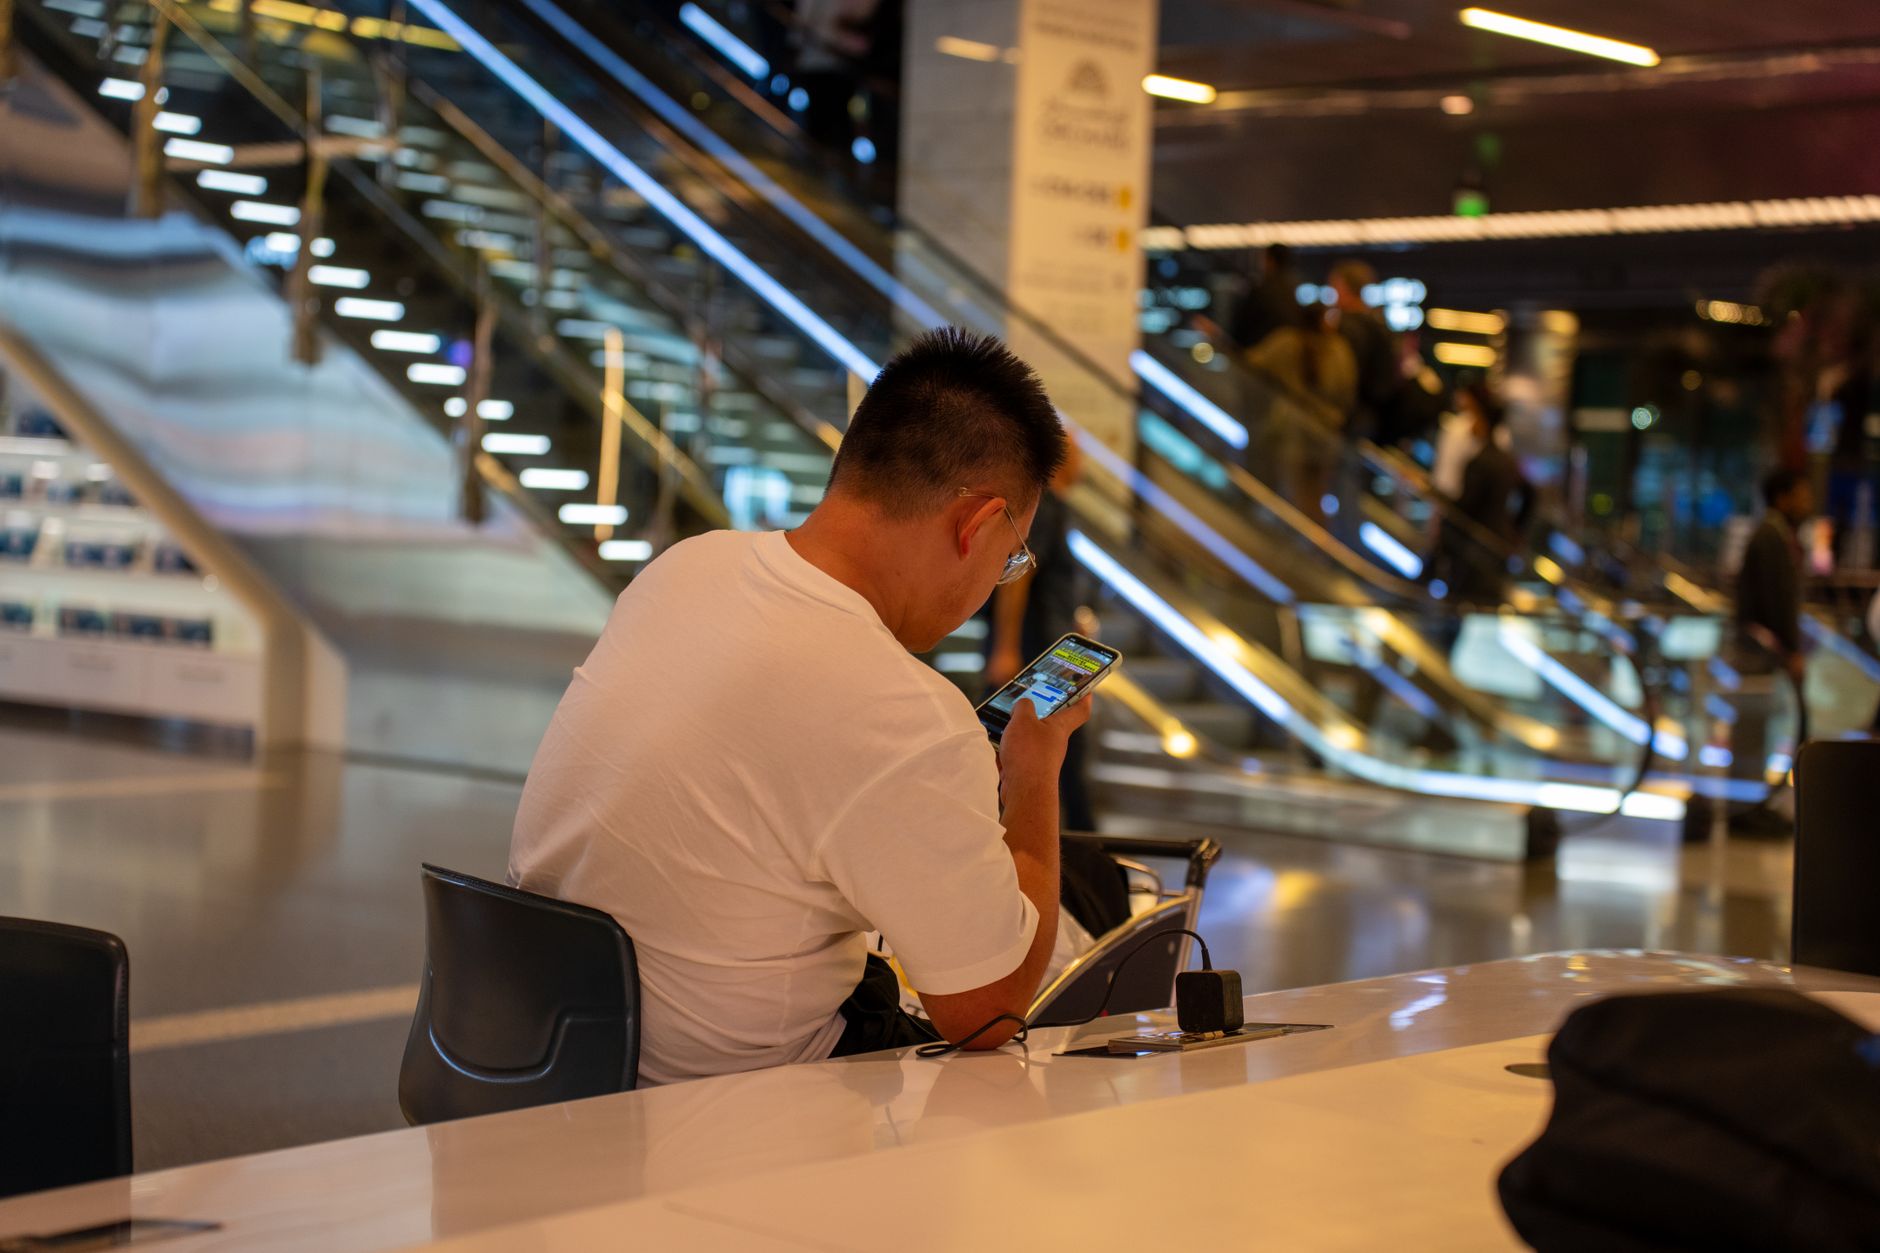
Travelers navigating busy airports often face a dilemma when their smartphone battery dips into the red. Public USB charging ports offer a convenient fix, yet various government agencies have historically urged caution. The Federal Bureau of Investigation, the Transportation Security Administration, and the Federal Communications Commission have all issued warnings over the years regarding so-called juice-jacking. These alerts caution that malicious actors could potentially compromise public charging stations to siphon data or install malware onto connected devices.
Security researchers, however, generally agree that the real-world threat remains heavily overblown. While academic demonstrations have successfully proven the concept, investigators point out a distinct lack of documented, large-scale attacks in the wild. The fundamental vulnerability stems from the architecture of the universal serial bus standard itself, which combines power delivery and data transfer into a single cable. During early proof-of-concept tests, researchers demonstrated how modified hardware could interact with connected devices.
Operating system developers long ago implemented safeguards to counter these vectors. Modern mobile software prompts users to explicitly approve any external data connection before transferring information. Travelers seeking absolute peace of mind can bypass public USB terminals entirely by packing a portable battery pack or plugging a traditional wall adapter directly into an AC outlet. For those who must rely on public kiosks, inexpensive USB data blockers physically disconnect the data pins while allowing electrical current to flow safely, though older adapters may limit charging speeds.



Comments