
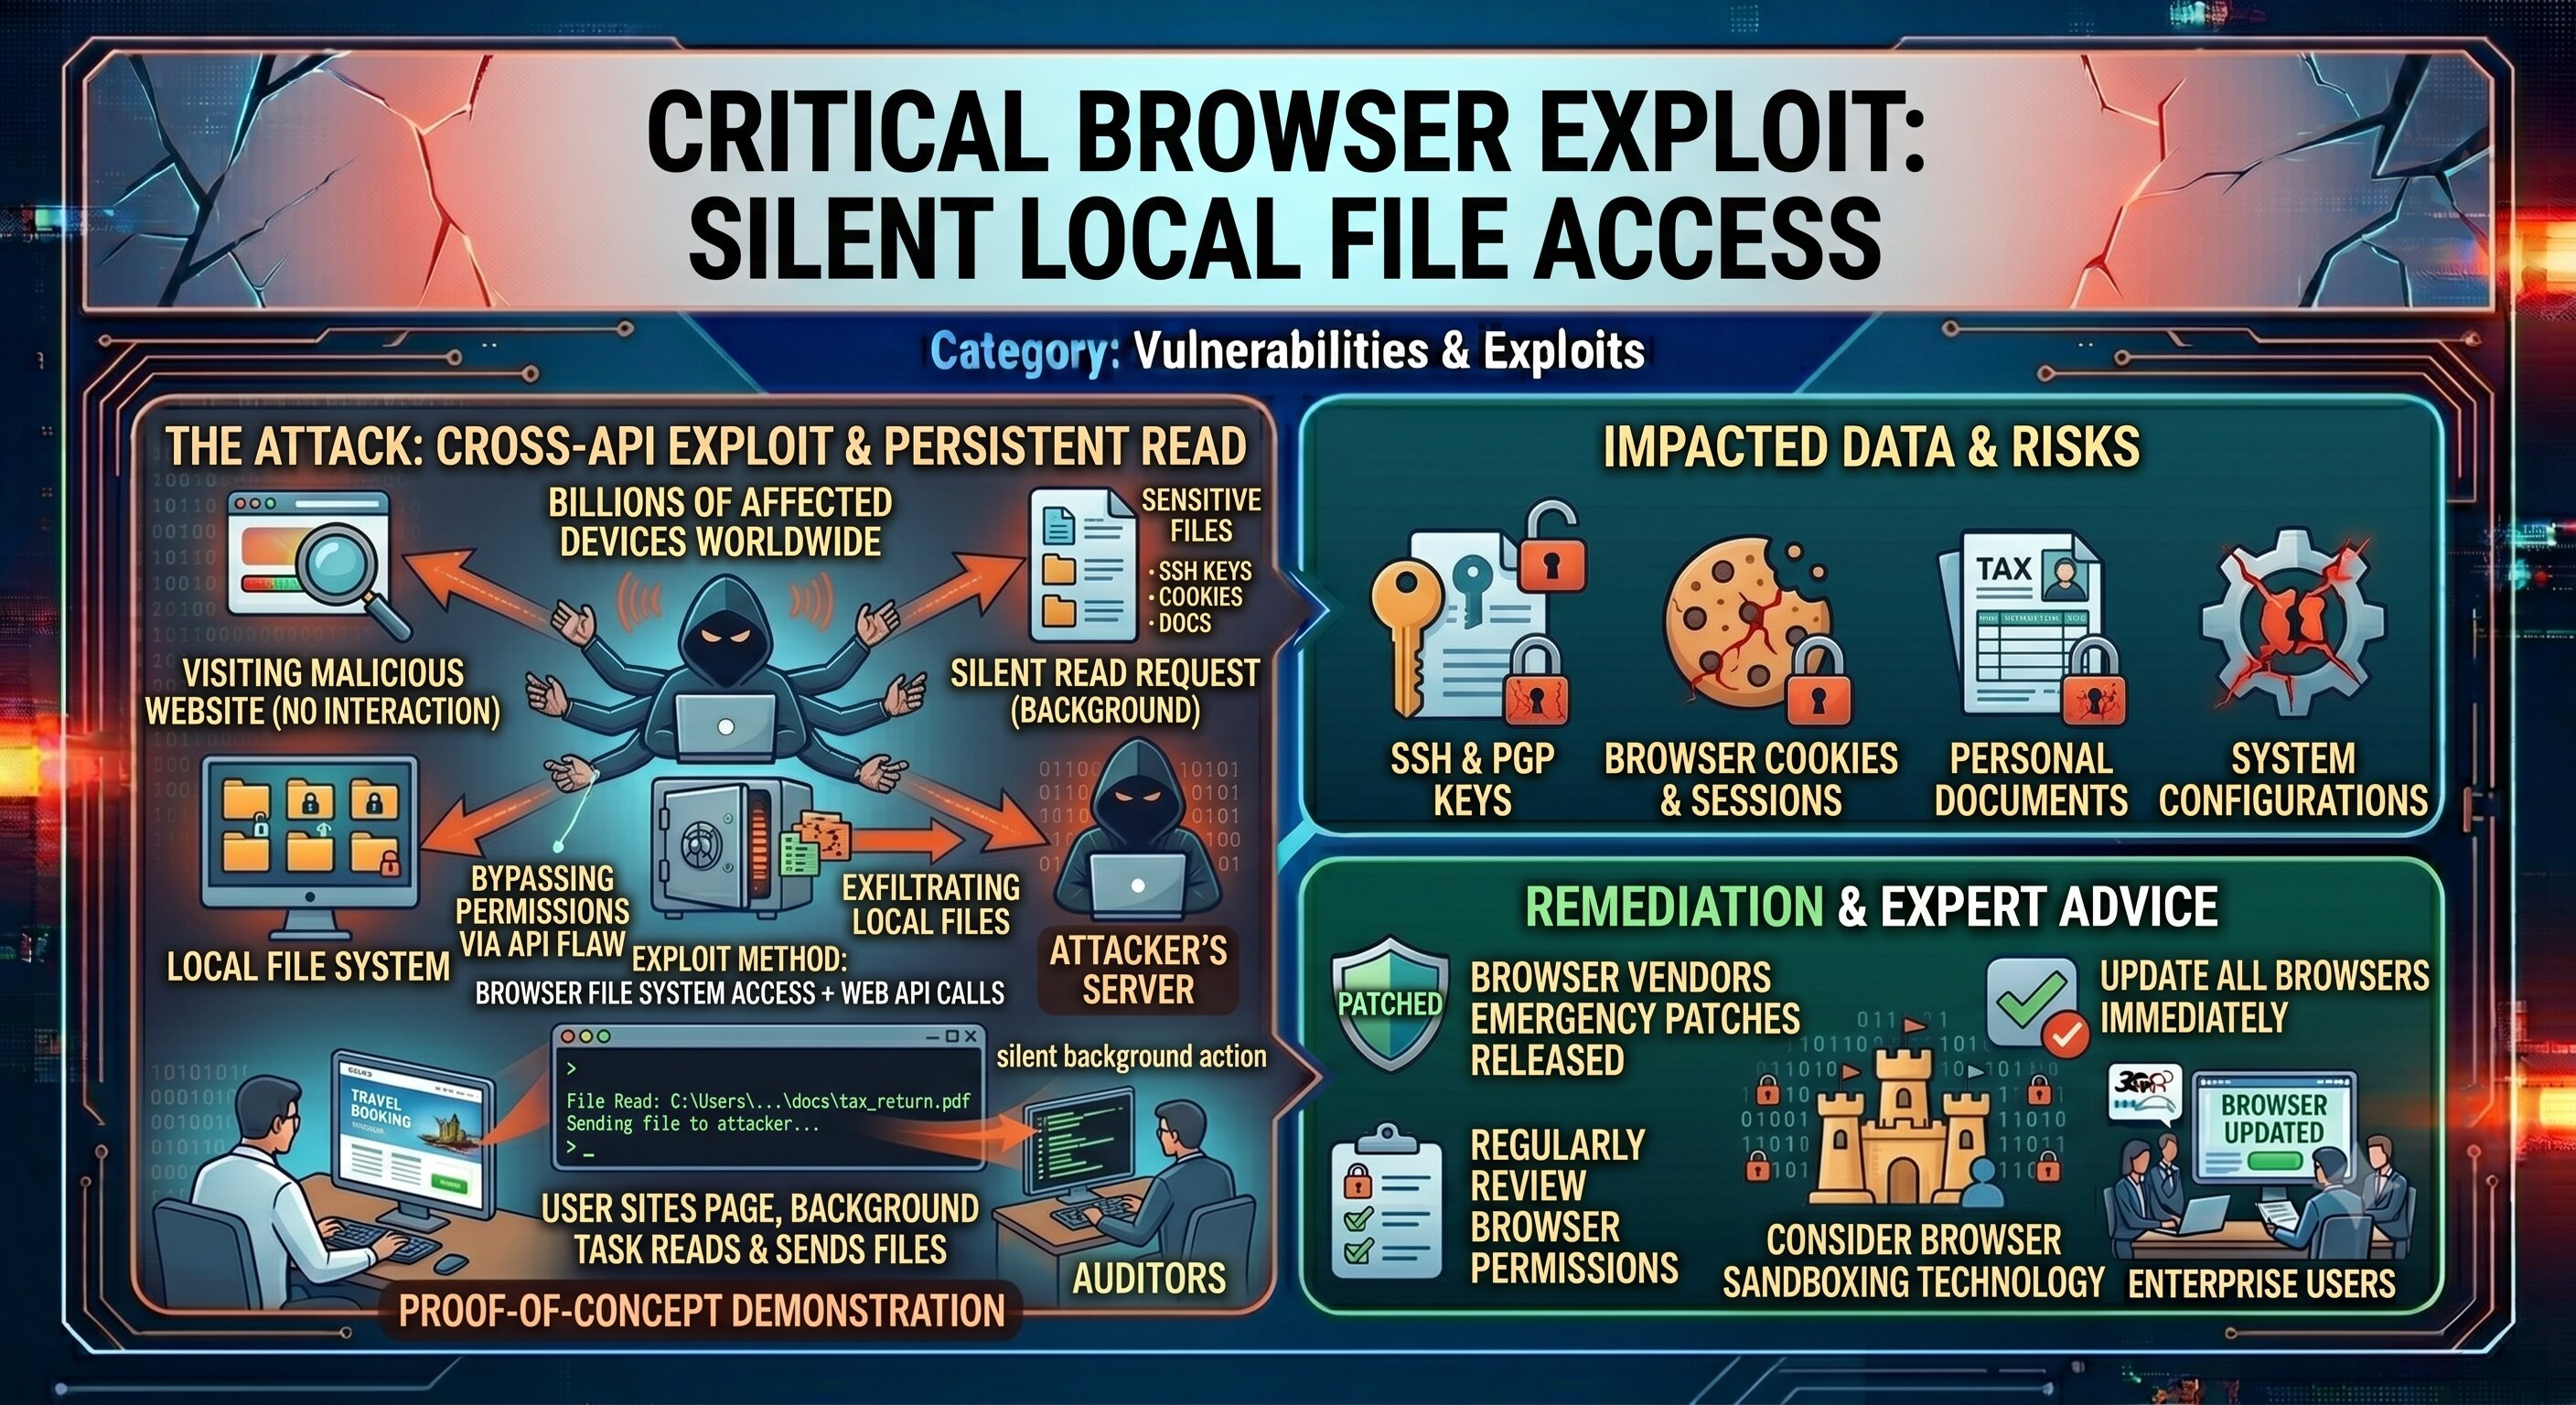
New Browser Exploit
Allows Websites to Access Local Files Silently
Category:
Vulnerabilities & Exploits
Security
researchers have disclosed a new browser exploit that allows malicious websites
to silently access files stored on a visitor's local computer without any user
interaction or warning. The vulnerability, which affects multiple major
browsers, exploits a flaw in the way browsers handle certain file system access
requests in combination with specific web API calls.
In a
proof-of-concept demonstration, the researchers showed that a malicious website
could silently read sensitive files from the victim's computer — including
documents, SSH keys, browser cookies, and configuration files — simply by
having the user visit the page. The entire attack takes place invisibly in the
background without triggering any browser warnings.
"This is
a particularly dangerous class of vulnerability because it requires absolutely
nothing from the victim," said researcher Sofia Martinez. "You visit
a page, and your local files can be read and sent to an attacker's server
without you knowing."
Browser
vendors were notified through responsible disclosure procedures and have worked
quickly to develop and test patches. Emergency updates have been released for
the affected browsers, and users are strongly urged to update immediately.
Security
professionals are also recommending that users regularly review browser
permissions, be cautious about visiting unfamiliar websites, and consider using
browser sandboxing technologies for sensitive activities. This incident
underscores the ongoing challenge of securing the complex and constantly
evolving web browser attack surface.





Comments