
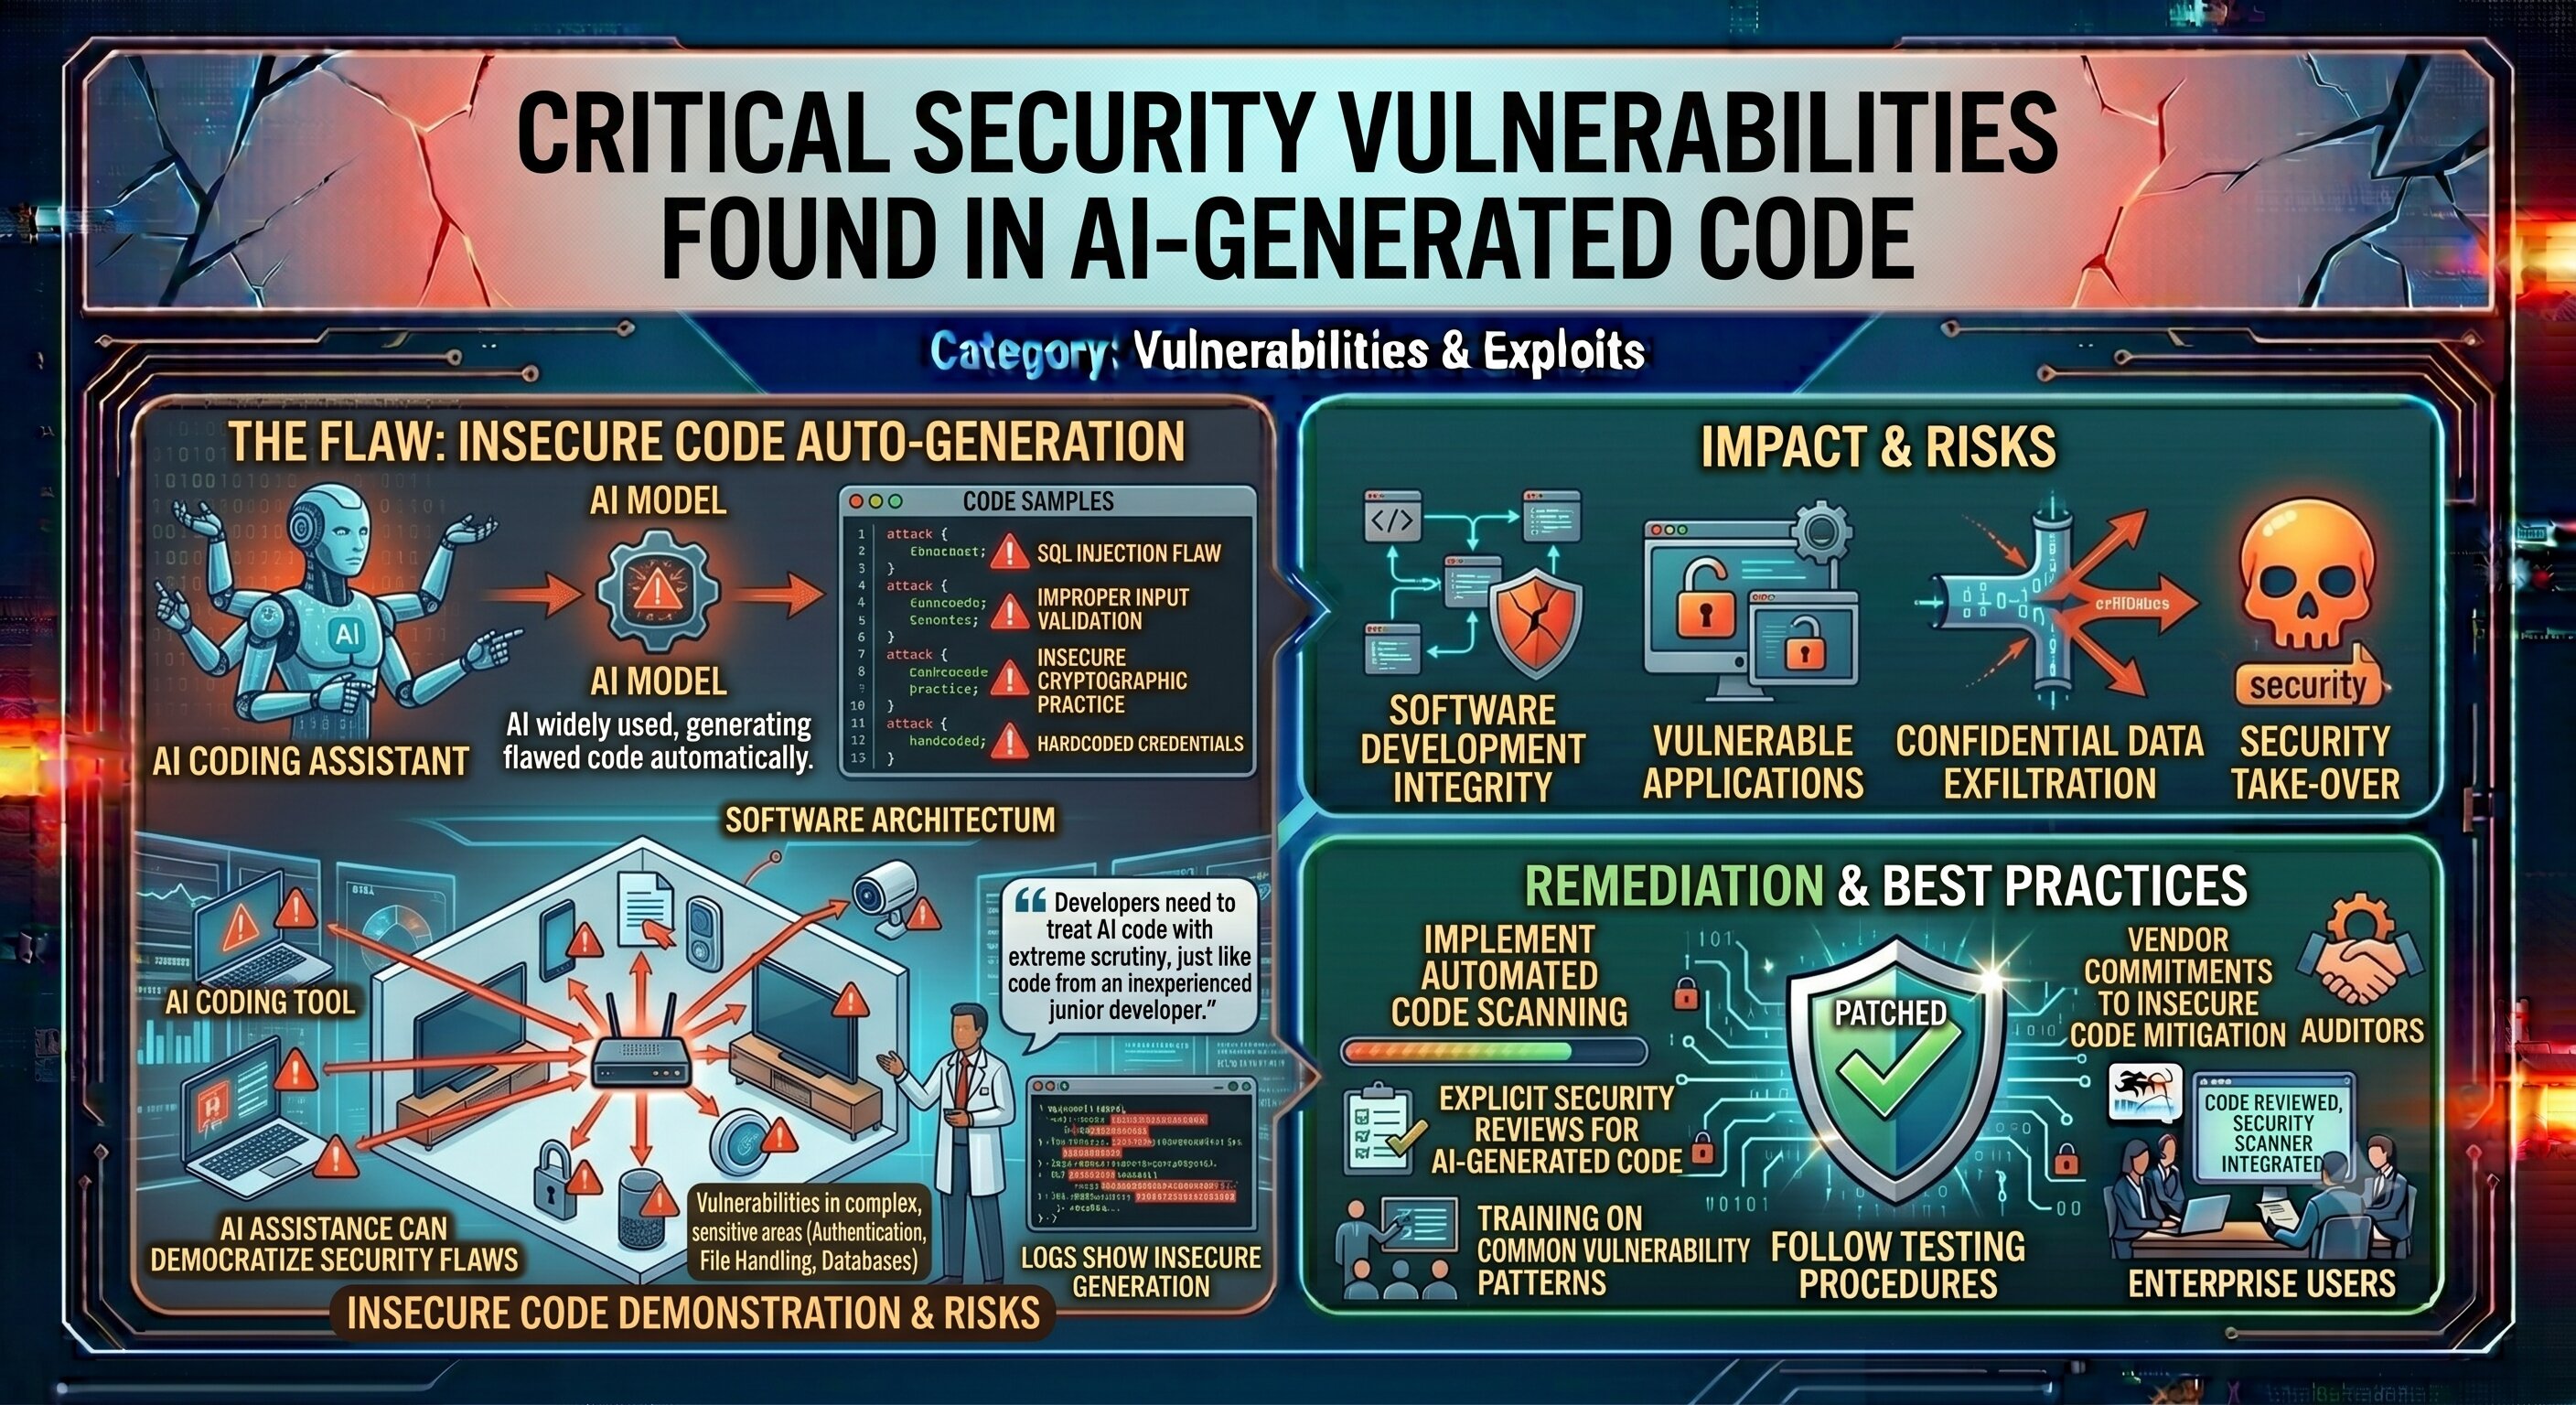
AI Coding
Assistants Found Generating Insecure Code Automatically
Category:
Vulnerabilities & Exploits
A
comprehensive study conducted by academic researchers has found that popular
AI-powered coding assistants — including tools widely used in professional
software development — frequently generate code containing serious security
vulnerabilities. The research analyzed thousands of code samples produced by
leading AI tools and found that a significant percentage contained flaws
including SQL injection vulnerabilities, improper input validation, insecure
cryptographic practices, and hardcoded credentials.
The study
found that the AI tools were most likely to introduce vulnerabilities when
generating code for security-sensitive operations, such as authentication
systems, file handling, and database queries — precisely the areas where
developers are most likely to rely on AI assistance due to their complexity.
"AI
coding tools have democratized software development, but they've also
democratized the introduction of security flaws," said lead researcher Dr.
Yuki Tanaka. "Developers need to treat AI-generated code with the same —
or greater — scrutiny that they would apply to code written by an inexperienced
junior developer."
Several AI
tool vendors have responded to the research, acknowledging the findings and
committing to improvements in how their models are trained and fine-tuned for
security-sensitive code generation. Some vendors are also implementing
automated security scanning for AI-generated code before it is shown to users.
Security
professionals are recommending that organizations update their code review
practices to explicitly include security review of AI-generated code, and that
developers receive training on common vulnerability patterns so they can
identify risky AI suggestions.





Comments