
U.S. Government Bans
Federal Use of Foreign-Developed Security Software
Category:
Policy, Regulations & Industry
The United
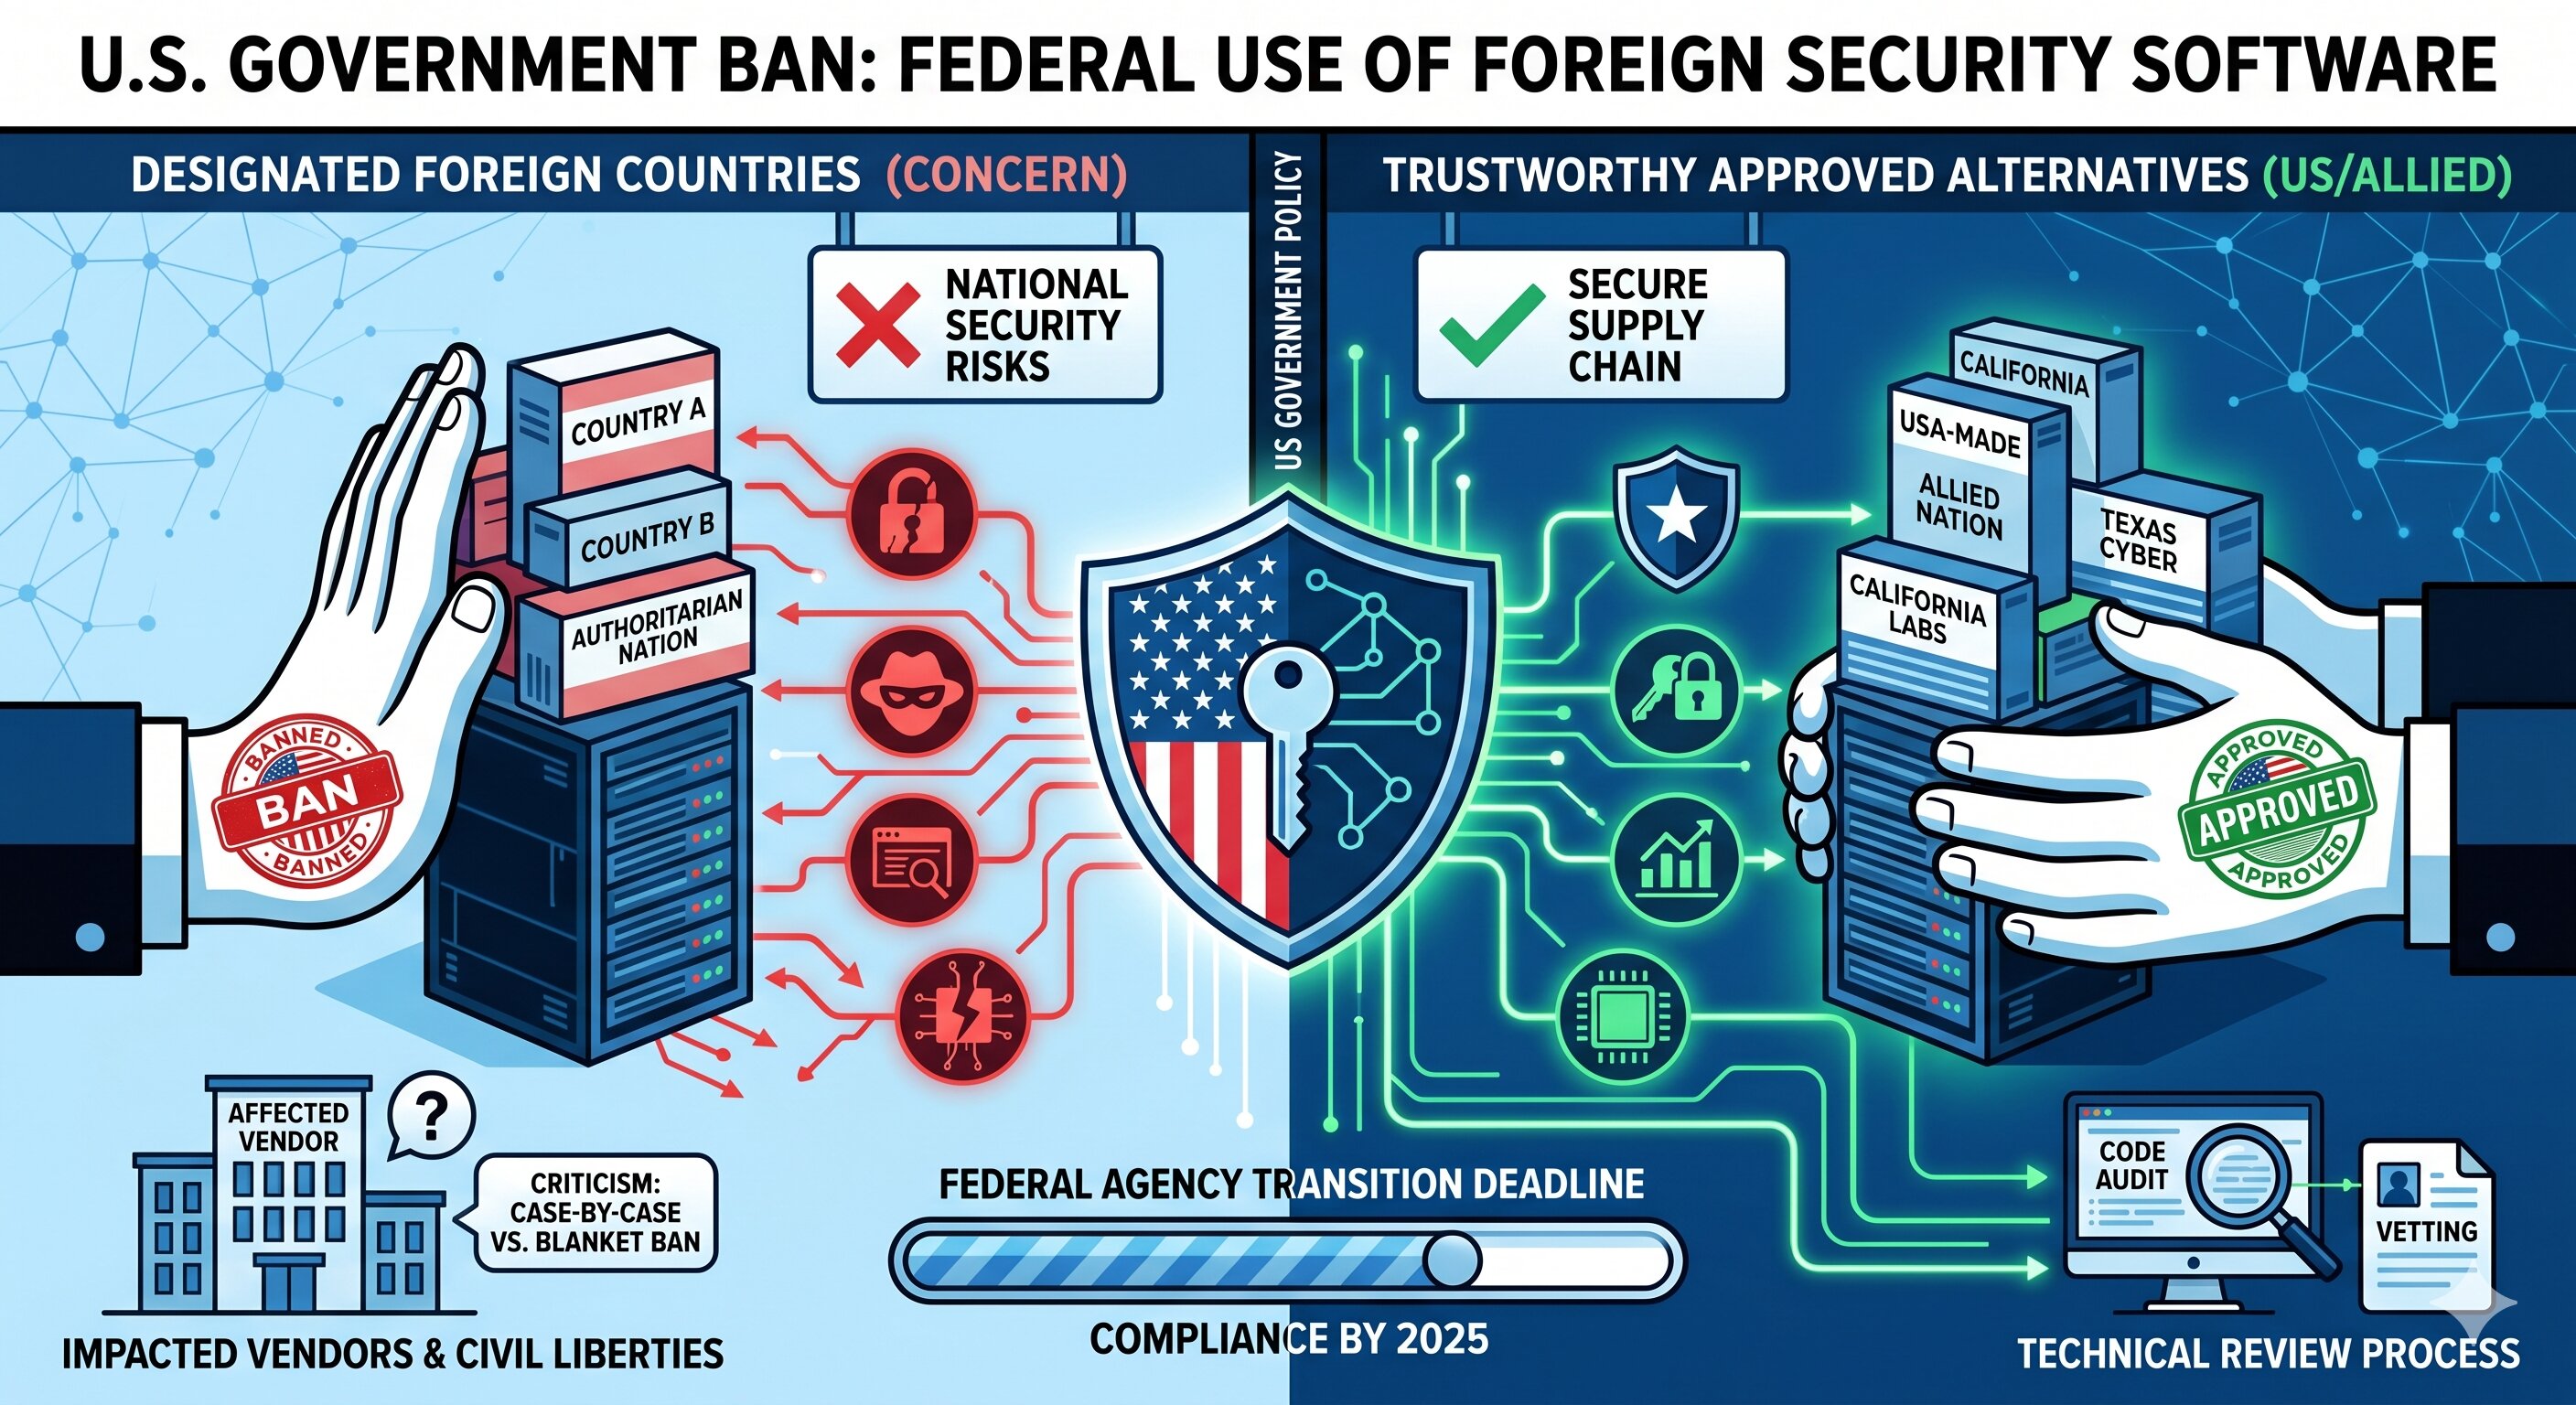
States government has issued a sweeping executive order banning federal
agencies from using cybersecurity software developed by companies from a list
of designated countries of concern, citing national security risks associated
with the potential for backdoors, unauthorized data access, and supply chain
compromise. The order represents one of the most significant steps taken by any
government to address foreign influence in its cybersecurity infrastructure.
The ban
covers a wide range of security products, including antivirus software, network
monitoring tools, identity and access management systems, and security
information and event management (SIEM) platforms. Federal agencies have been
given a defined timeframe to complete the transition to approved alternatives.
"The
software we use to protect our most sensitive systems must itself be
trustworthy," said the National Security Advisor in a statement
accompanying the order. "We cannot defend our networks with tools that may
themselves be vectors for foreign intelligence collection."
The order has
significant implications for the cybersecurity software market, as several
large vendors will be directly affected. It also raises questions about the
security of state and local governments and critical infrastructure operators
who may be using the same software but are not covered by the federal order.
Civil
liberties advocates have raised concerns about the precedent set by
blacklisting companies based on national origin, arguing that technical
assessment of specific products is a more appropriate approach than blanket
country-of-origin bans. The administration has indicated that technical review
processes will be established to assess specific products on a case-by-case
basis.





Comments