
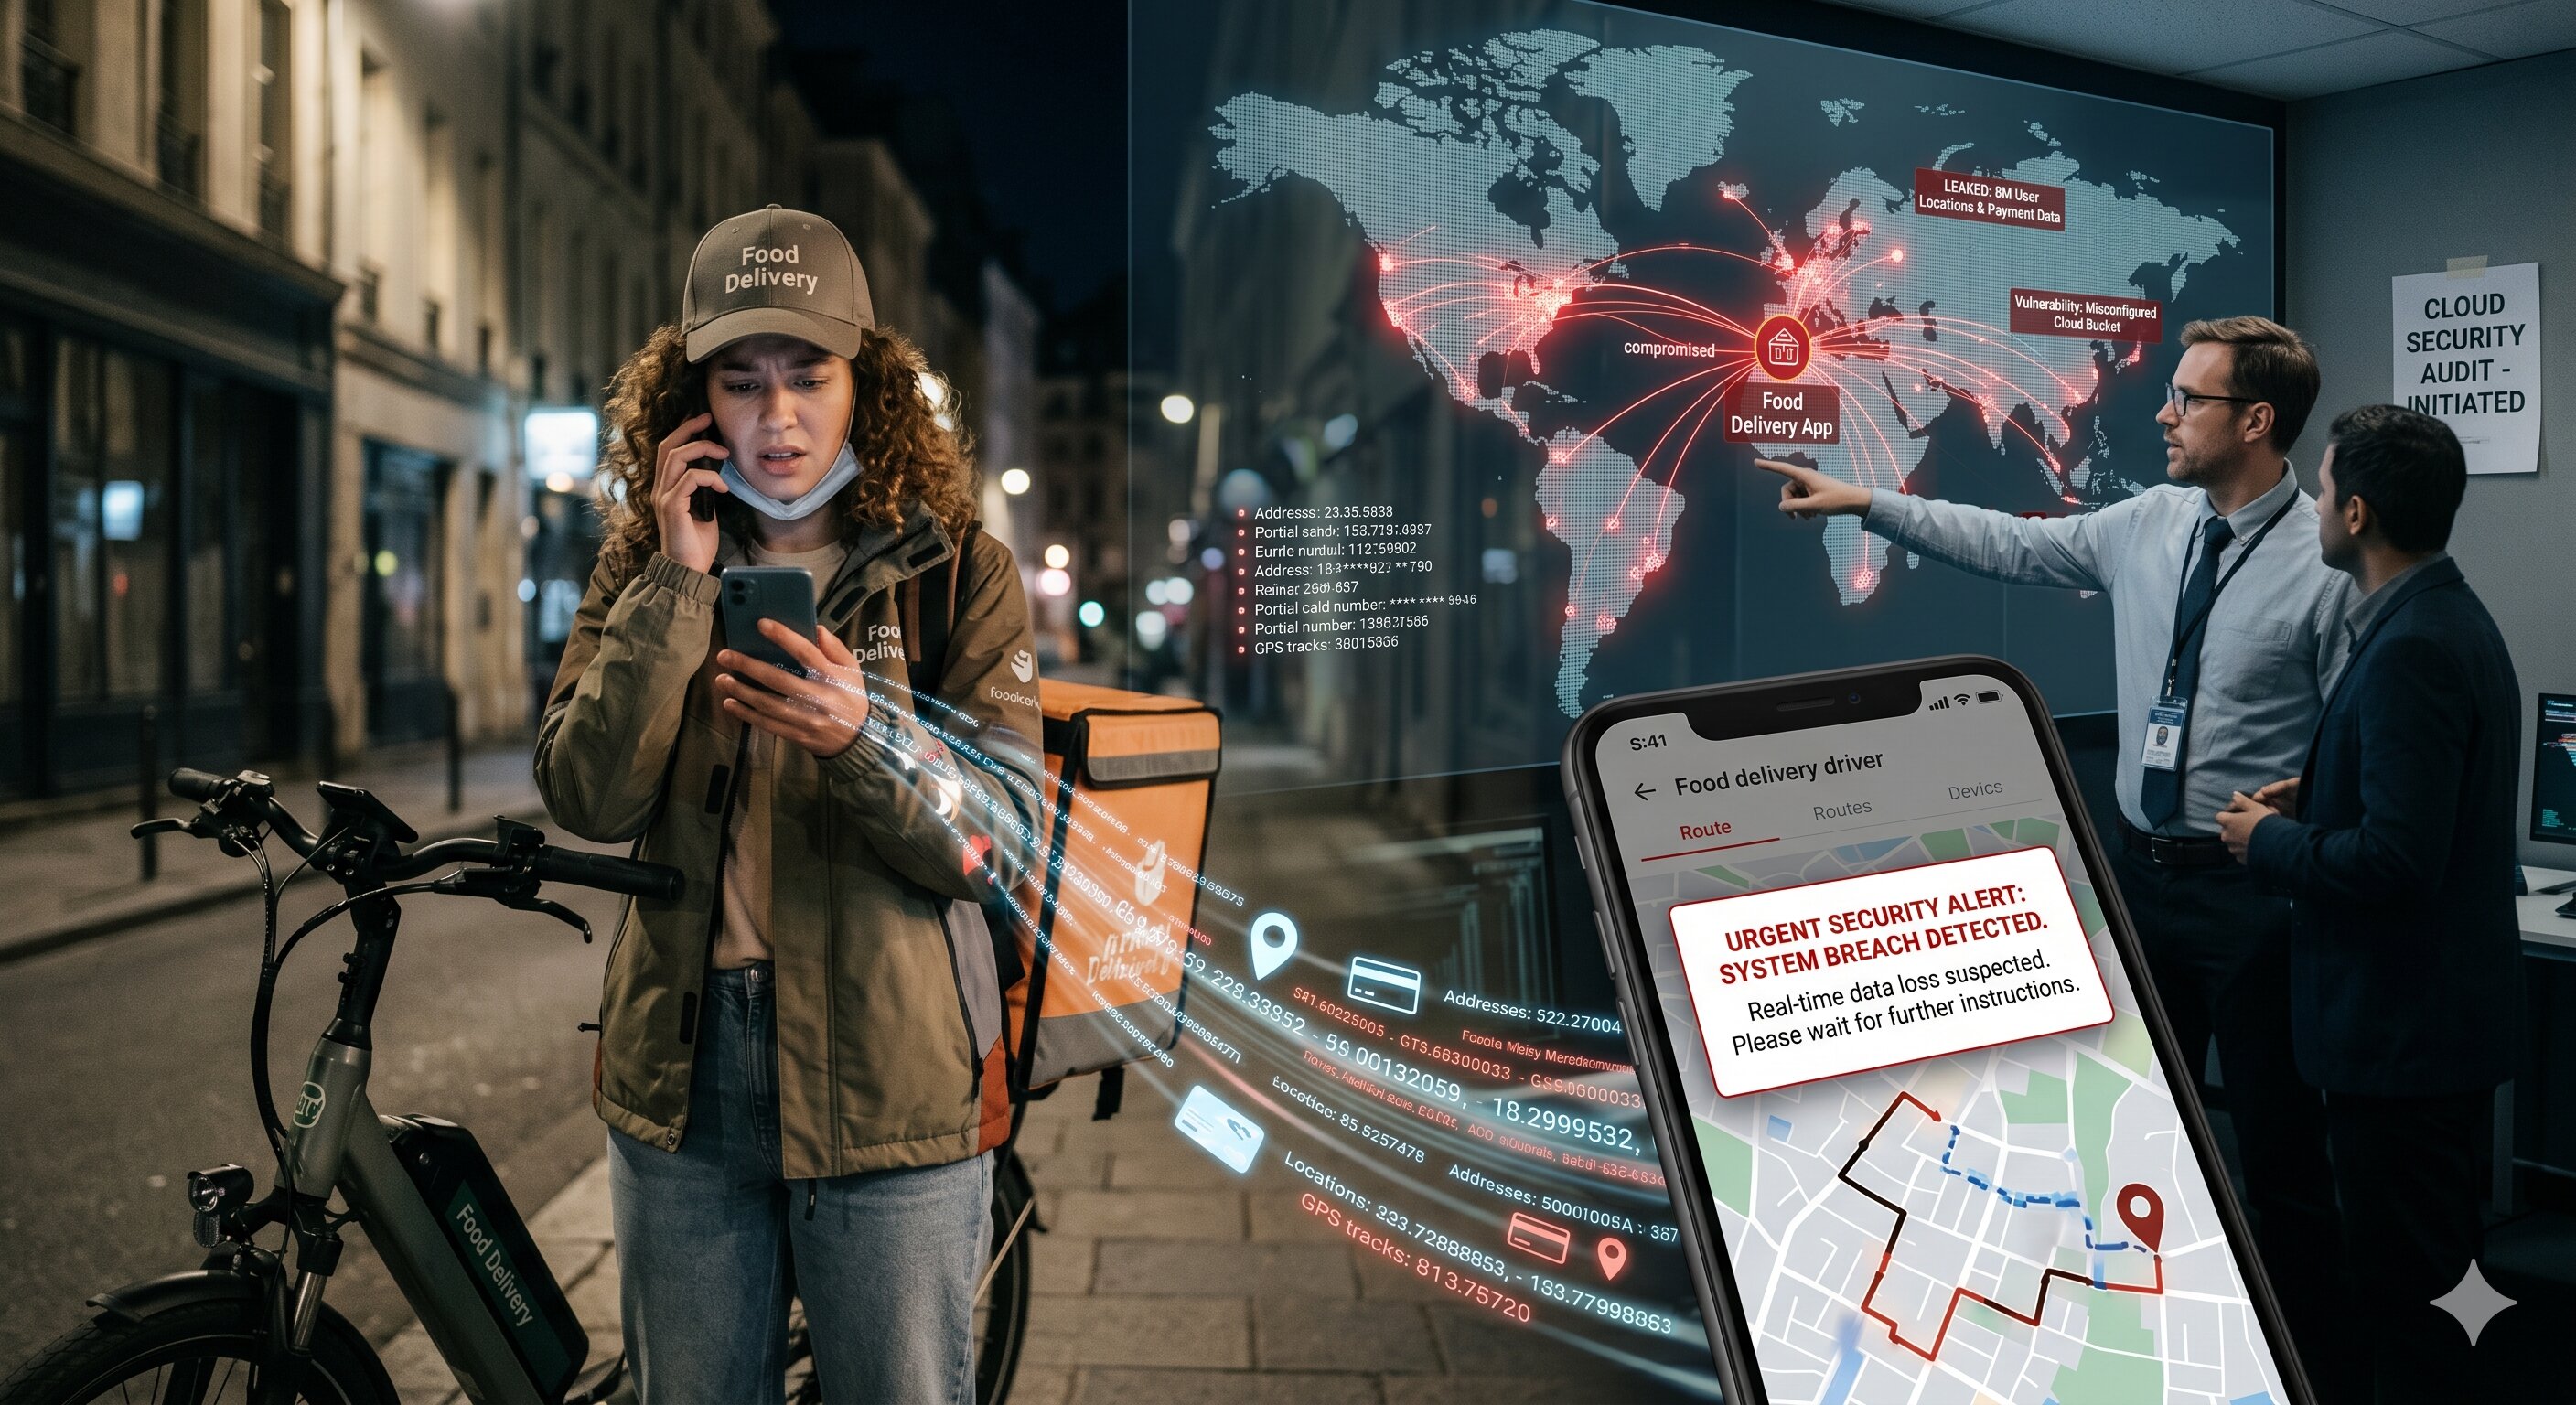
Popular Food Delivery
App Leaks Users' Location and Payment Data
Category:
Data Breaches
A widely used
food delivery application has suffered a significant data breach that exposed
the real-time location history, home addresses, and partial payment information
of an estimated 8 million users. The breach, caused by a misconfigured cloud
storage bucket, left sensitive user data publicly accessible on the internet
for over two weeks before being discovered and secured.
Security
researcher Marcus Webb stumbled upon the exposed data during a routine scan of
publicly accessible cloud storage. He found that the bucket contained detailed
delivery records, including pickup and drop-off addresses, GPS coordinates,
timestamps, and masked credit card details. In some cases, it was possible to
reconstruct users' daily routines based on their delivery history.
"This
kind of data is a gold mine for stalkers, burglars, and identity thieves,"
Webb warned in his disclosure report. "Knowing where someone lives, where
they work, and what their daily habits look like is incredibly sensitive
information."
The food
delivery company has since secured the storage bucket and launched an internal
investigation. It has notified affected users and is working with cybersecurity
experts to audit its cloud infrastructure for similar misconfigurations.
This incident
adds to a growing list of data breaches caused by improperly configured cloud
storage, a problem that continues to plague organizations of all sizes. Experts
recommend regular audits of cloud resources, the use of automated
misconfiguration detection tools, and stricter access control policies.





Comments