
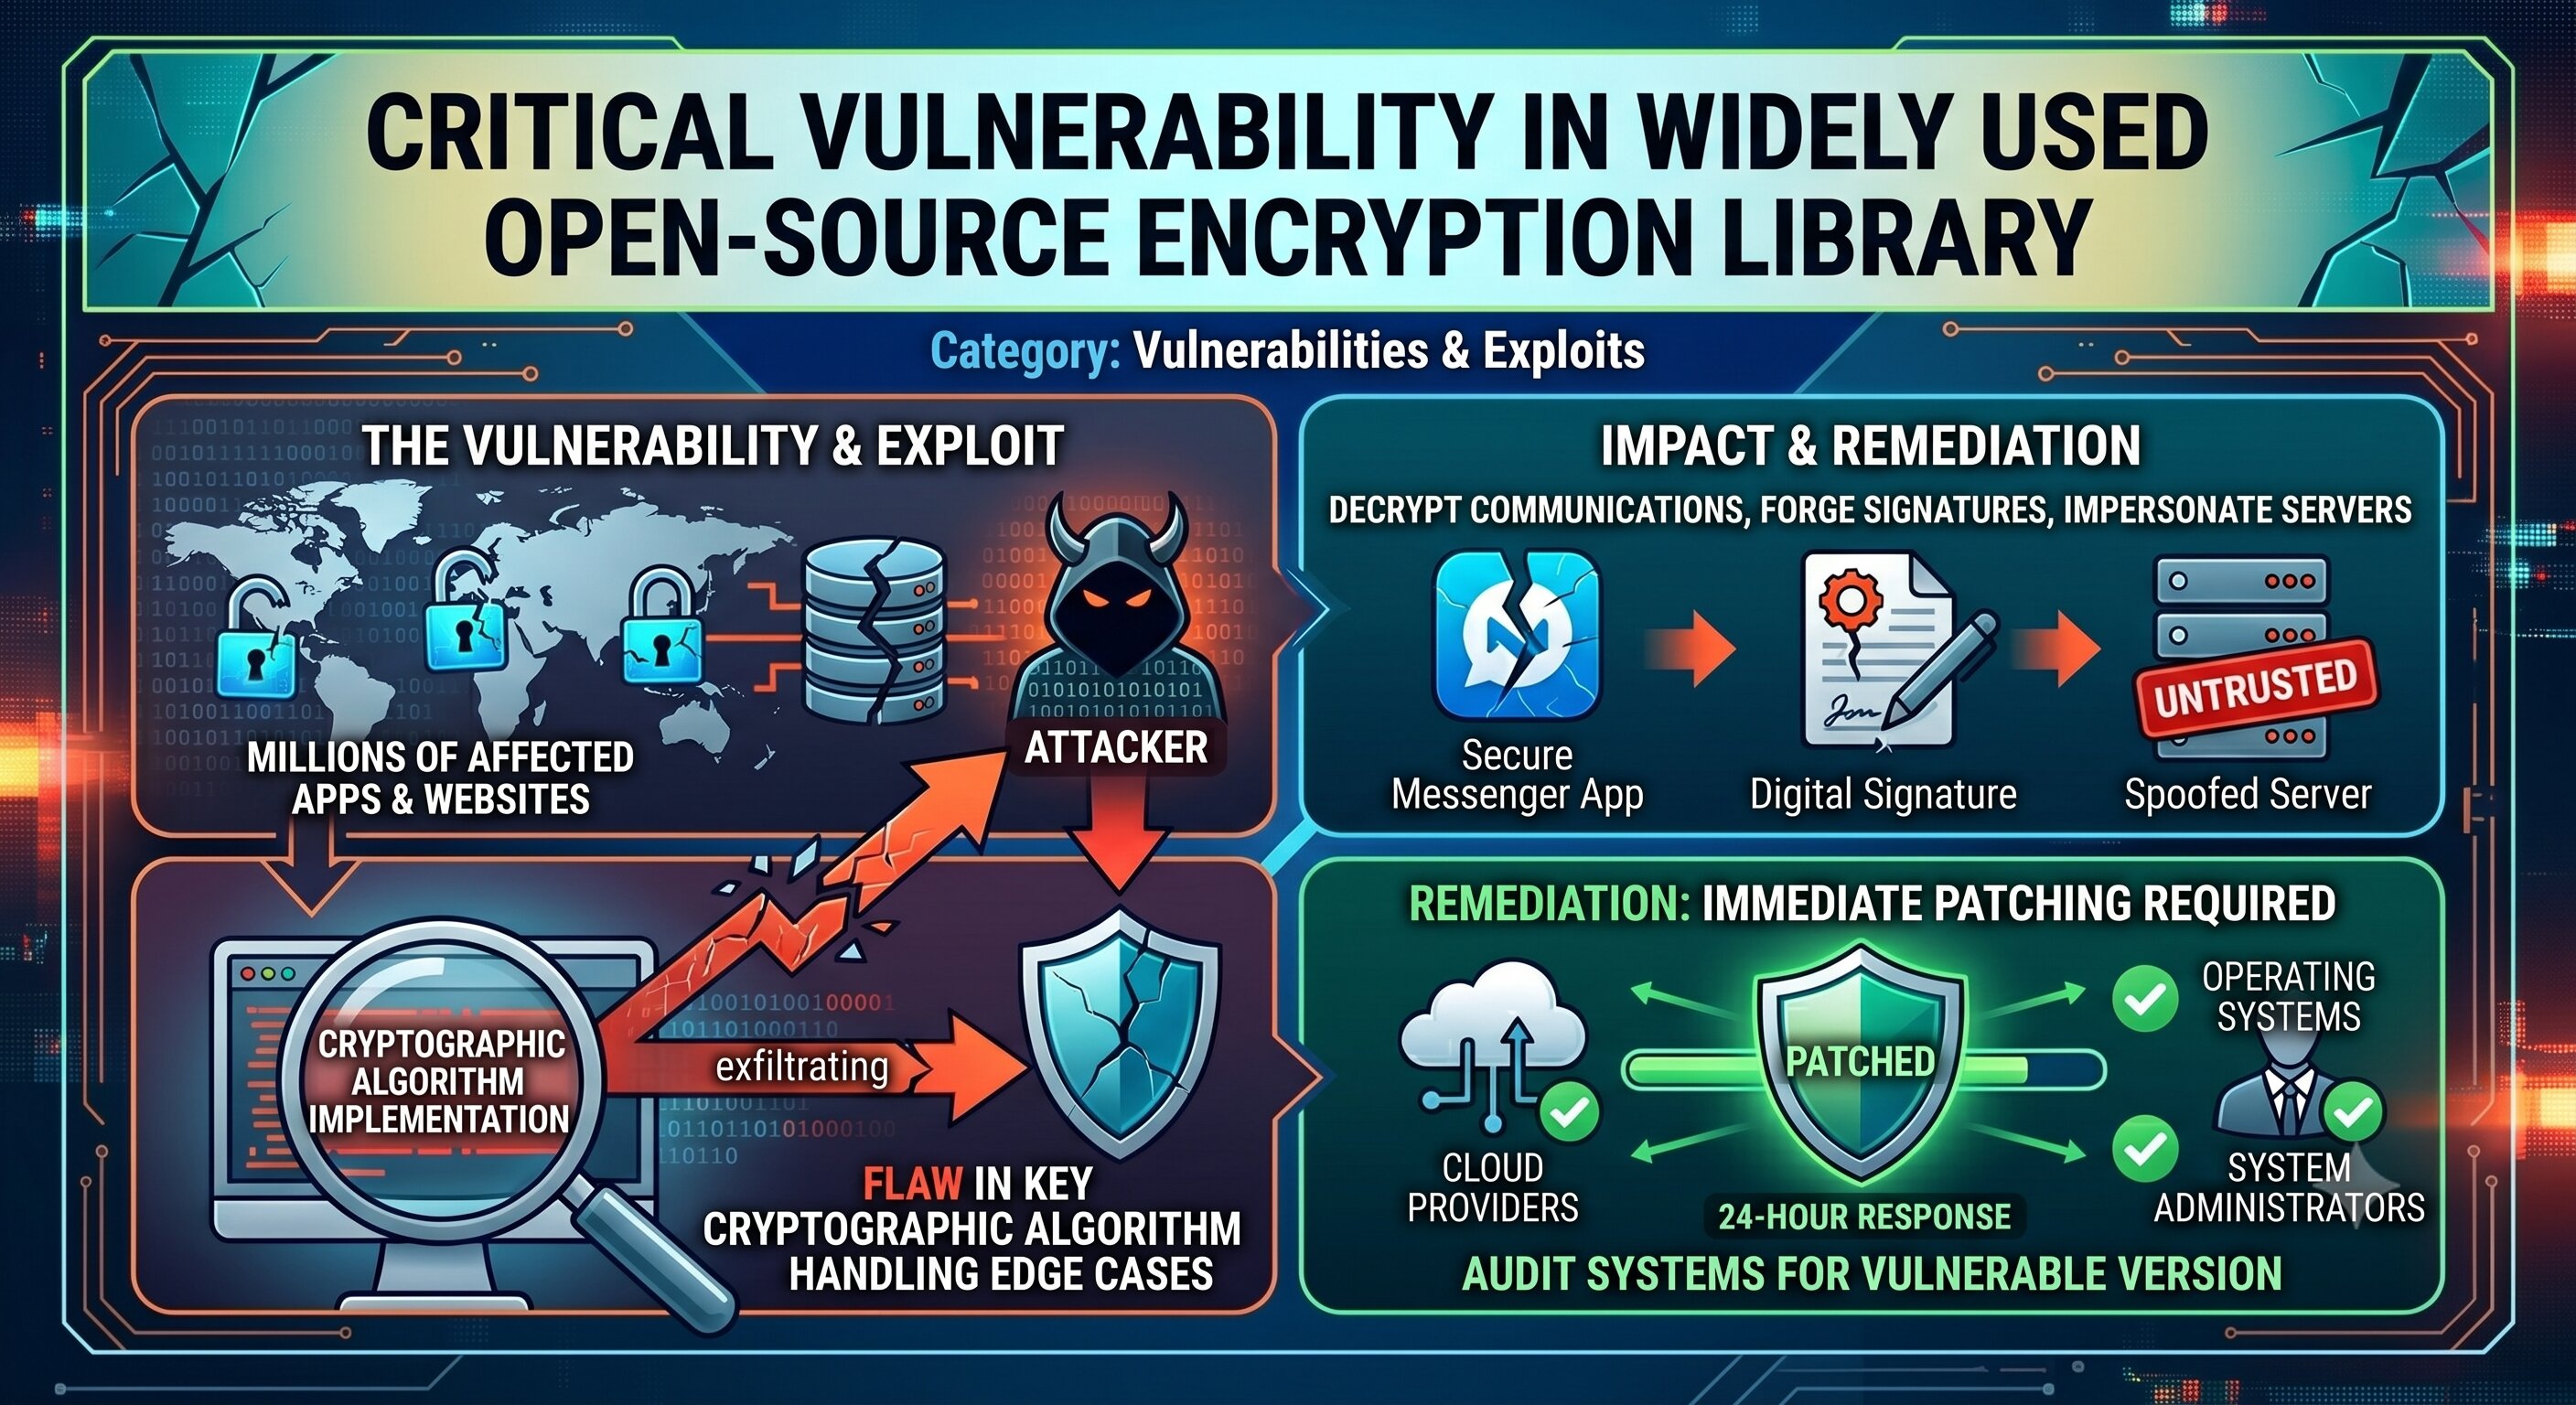
Critical Flaw Found
in Widely Used Open-Source Encryption Library
Category:
Vulnerabilities & Exploits
Security
researchers have uncovered a critical vulnerability in a widely used
open-source encryption library that underpins the security of millions of
applications and websites worldwide. The flaw, which has been assigned the
highest possible severity rating, could allow attackers to decrypt sensitive
communications, forge digital signatures, and impersonate trusted servers.
The
vulnerability exists in the library's implementation of a key cryptographic
algorithm and stems from an error in how the library handles certain edge cases
during decryption operations. An attacker who can position themselves in the
network path between a client and server — a man-in-the-middle attack — could
potentially exploit the flaw to intercept and decrypt what should be encrypted
communications.
"Given
how deeply embedded this library is in modern software infrastructure, the
potential impact of this vulnerability is enormous," said lead researcher
Dr. Amara Osei. "We're talking about everything from secure web browsing
to encrypted messaging apps to financial transaction systems."
The
open-source community has responded with impressive speed. A patch was released
within 24 hours of the vulnerability being disclosed to the library's
maintainers. However, the challenge now lies in getting millions of
applications and systems that depend on the library to apply the update.
Major cloud
providers, operating system vendors, and software companies have been briefed
and are in the process of releasing their own updates. System administrators
are urged to audit all systems for the vulnerable library version and
prioritize patching immediately.





Comments