
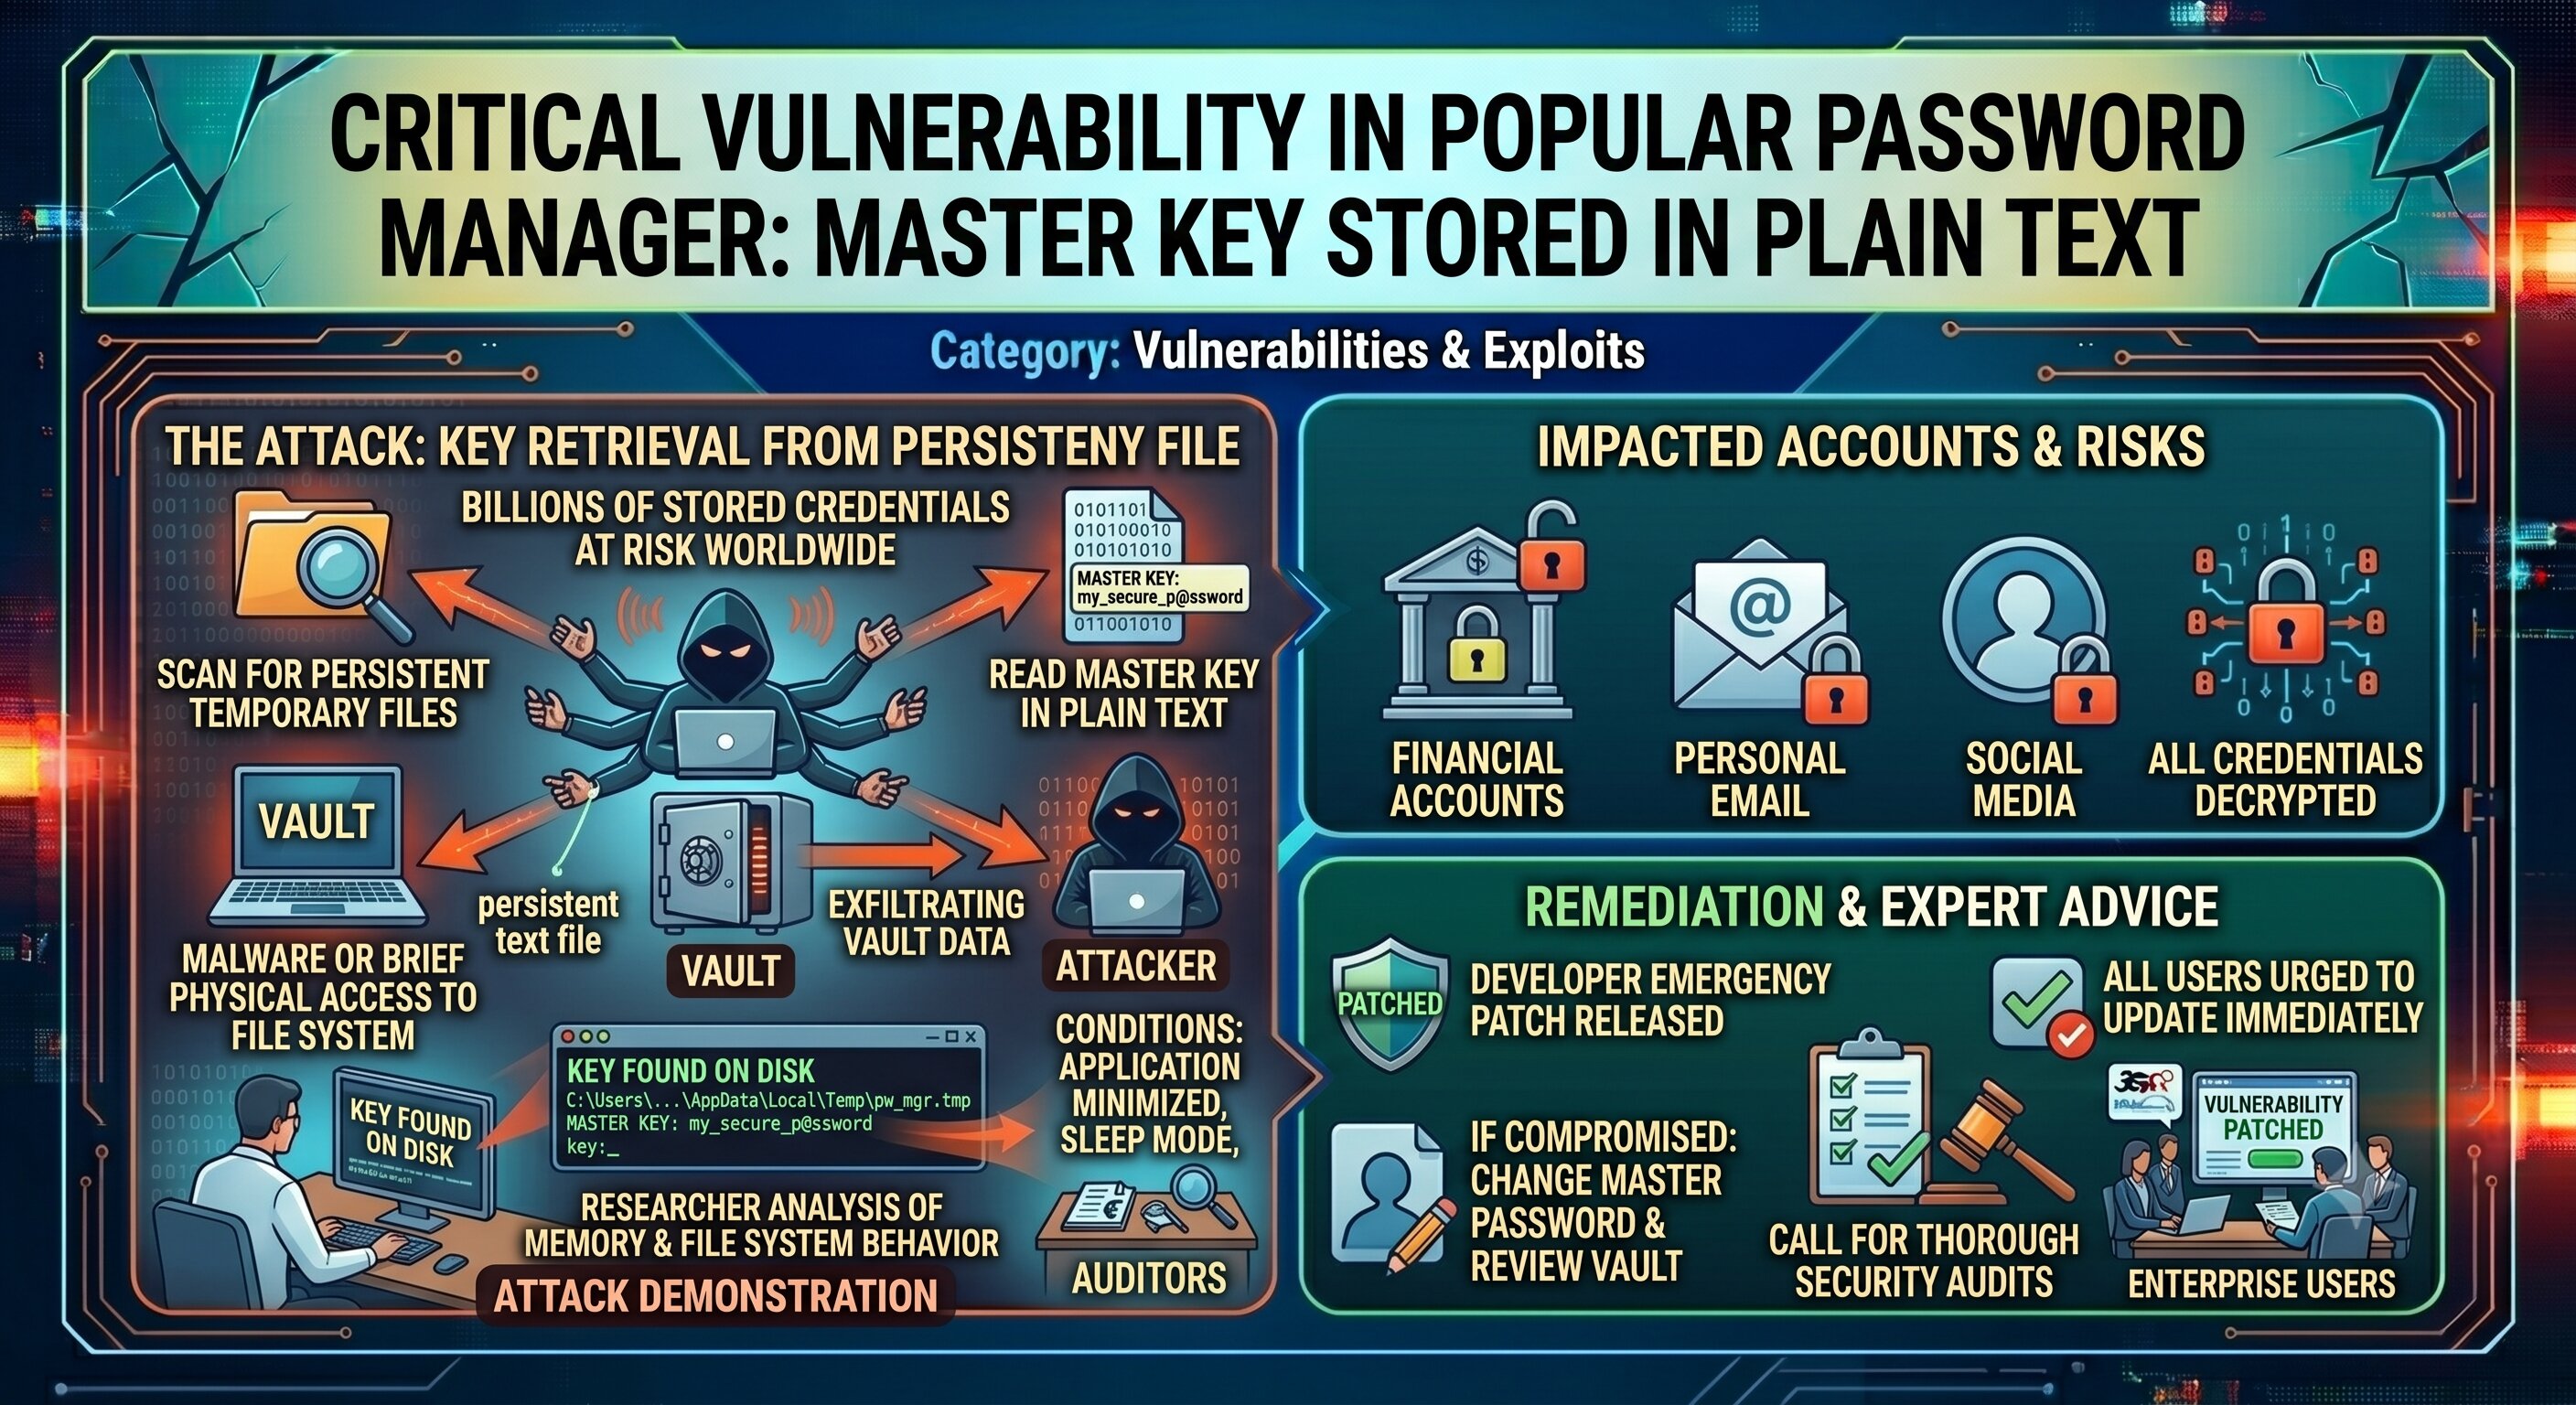
Popular Password
Manager Found Storing Keys in Plain Text
Category:
Vulnerabilities & Exploits
A security
audit of a popular password management application has revealed a serious
vulnerability in which the master encryption key used to protect users' stored
passwords was being temporarily written to disk in plain, unencrypted text
during certain operations. The discovery has prompted urgent concern among the
application's millions of users, many of whom rely on it to safeguard
credentials for sensitive financial and personal accounts.
The issue was
identified by a security researcher during a routine analysis of the
application's memory and file system behavior. Under specific conditions —
including when the application was minimized, placed in sleep mode, or during
certain autofill operations — the master key was written to a temporary file
that persisted on disk longer than intended and was not securely wiped.
"A
password manager that doesn't properly protect its master key is potentially
worse than not using one at all," the researcher stated. "An attacker
with even brief physical access to the machine, or the ability to access the
file system through malware, could retrieve the key and decrypt the entire
password vault."
The
application's developer has confirmed the vulnerability and released an
emergency patch addressing the issue. All users are urged to update
immediately. The developer has also recommended that users who believe their
systems may have been compromised change their master password and review all
stored credentials.
This incident
highlights the critical importance of thorough security auditing for tools that
are themselves designed as security solutions.





Comments