
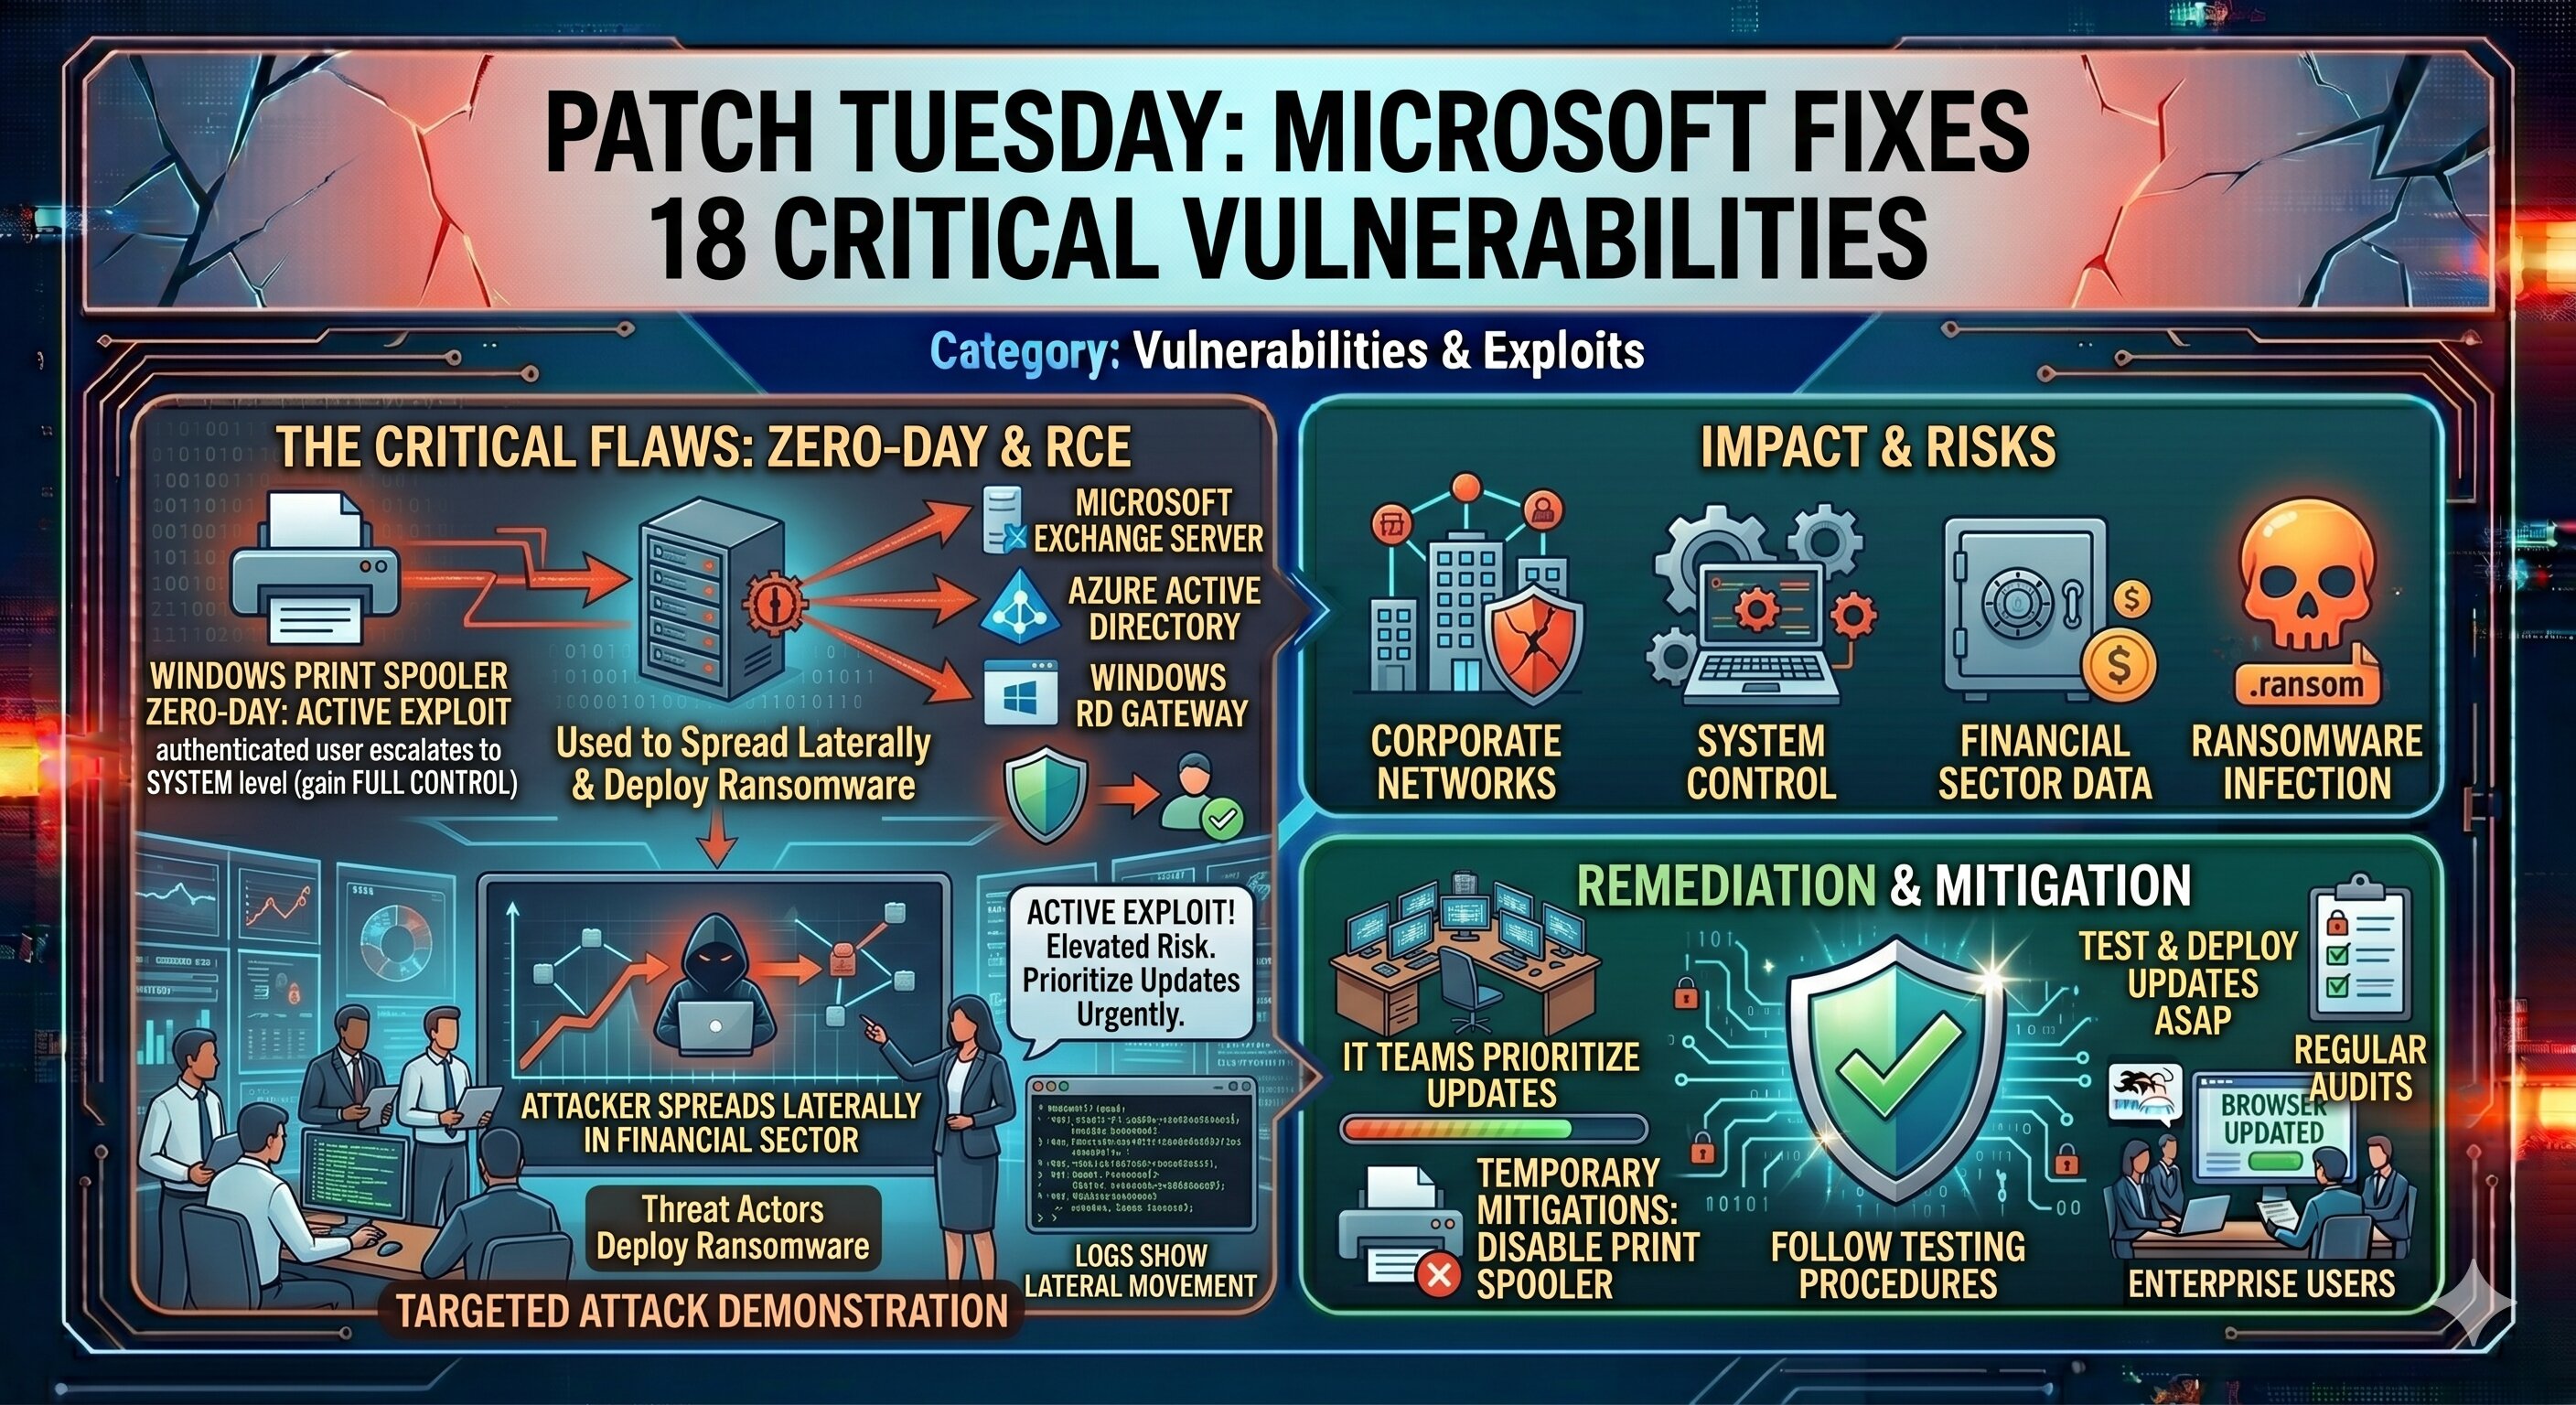
Patch Tuesday:
Microsoft Fixes 18 Critical Security Vulnerabilities
Category:
Vulnerabilities & Exploits
Microsoft has
released its monthly Patch Tuesday security update, addressing a total of 94
vulnerabilities across its product portfolio, including 18 rated as Critical.
Among the most serious flaws patched this month is a zero-day vulnerability in
the Windows Print Spooler service that has already been actively exploited in
targeted attacks against organizations in the financial services sector.
The zero-day
flaw allows an authenticated user to escalate their privileges to SYSTEM level,
effectively gaining full control over the affected machine. Combined with other
attack techniques, this vulnerability has been used by threat actors to spread
laterally across corporate networks and deploy ransomware.
Also fixed
this month are critical remote code execution vulnerabilities in Microsoft
Exchange Server, Azure Active Directory, and the Windows Remote Desktop
Gateway. The Exchange vulnerability is particularly notable given the history
of Exchange flaws being aggressively exploited by both cybercriminals and
nation-state actors.
"This is
a substantial Patch Tuesday, and IT teams should prioritize these updates with
particular urgency," said Aditi Kapoor, principal security engineer at a
major enterprise security firm. "The Print Spooler zero-day is being
actively exploited, which means every day without the patch is a day of
elevated risk."
System
administrators are urged to deploy the updates across their environments as
quickly as possible, following their standard testing procedures. Organizations
that cannot patch immediately should consider implementing temporary
mitigations, such as disabling the Print Spooler service on systems where it is
not required.





Comments