
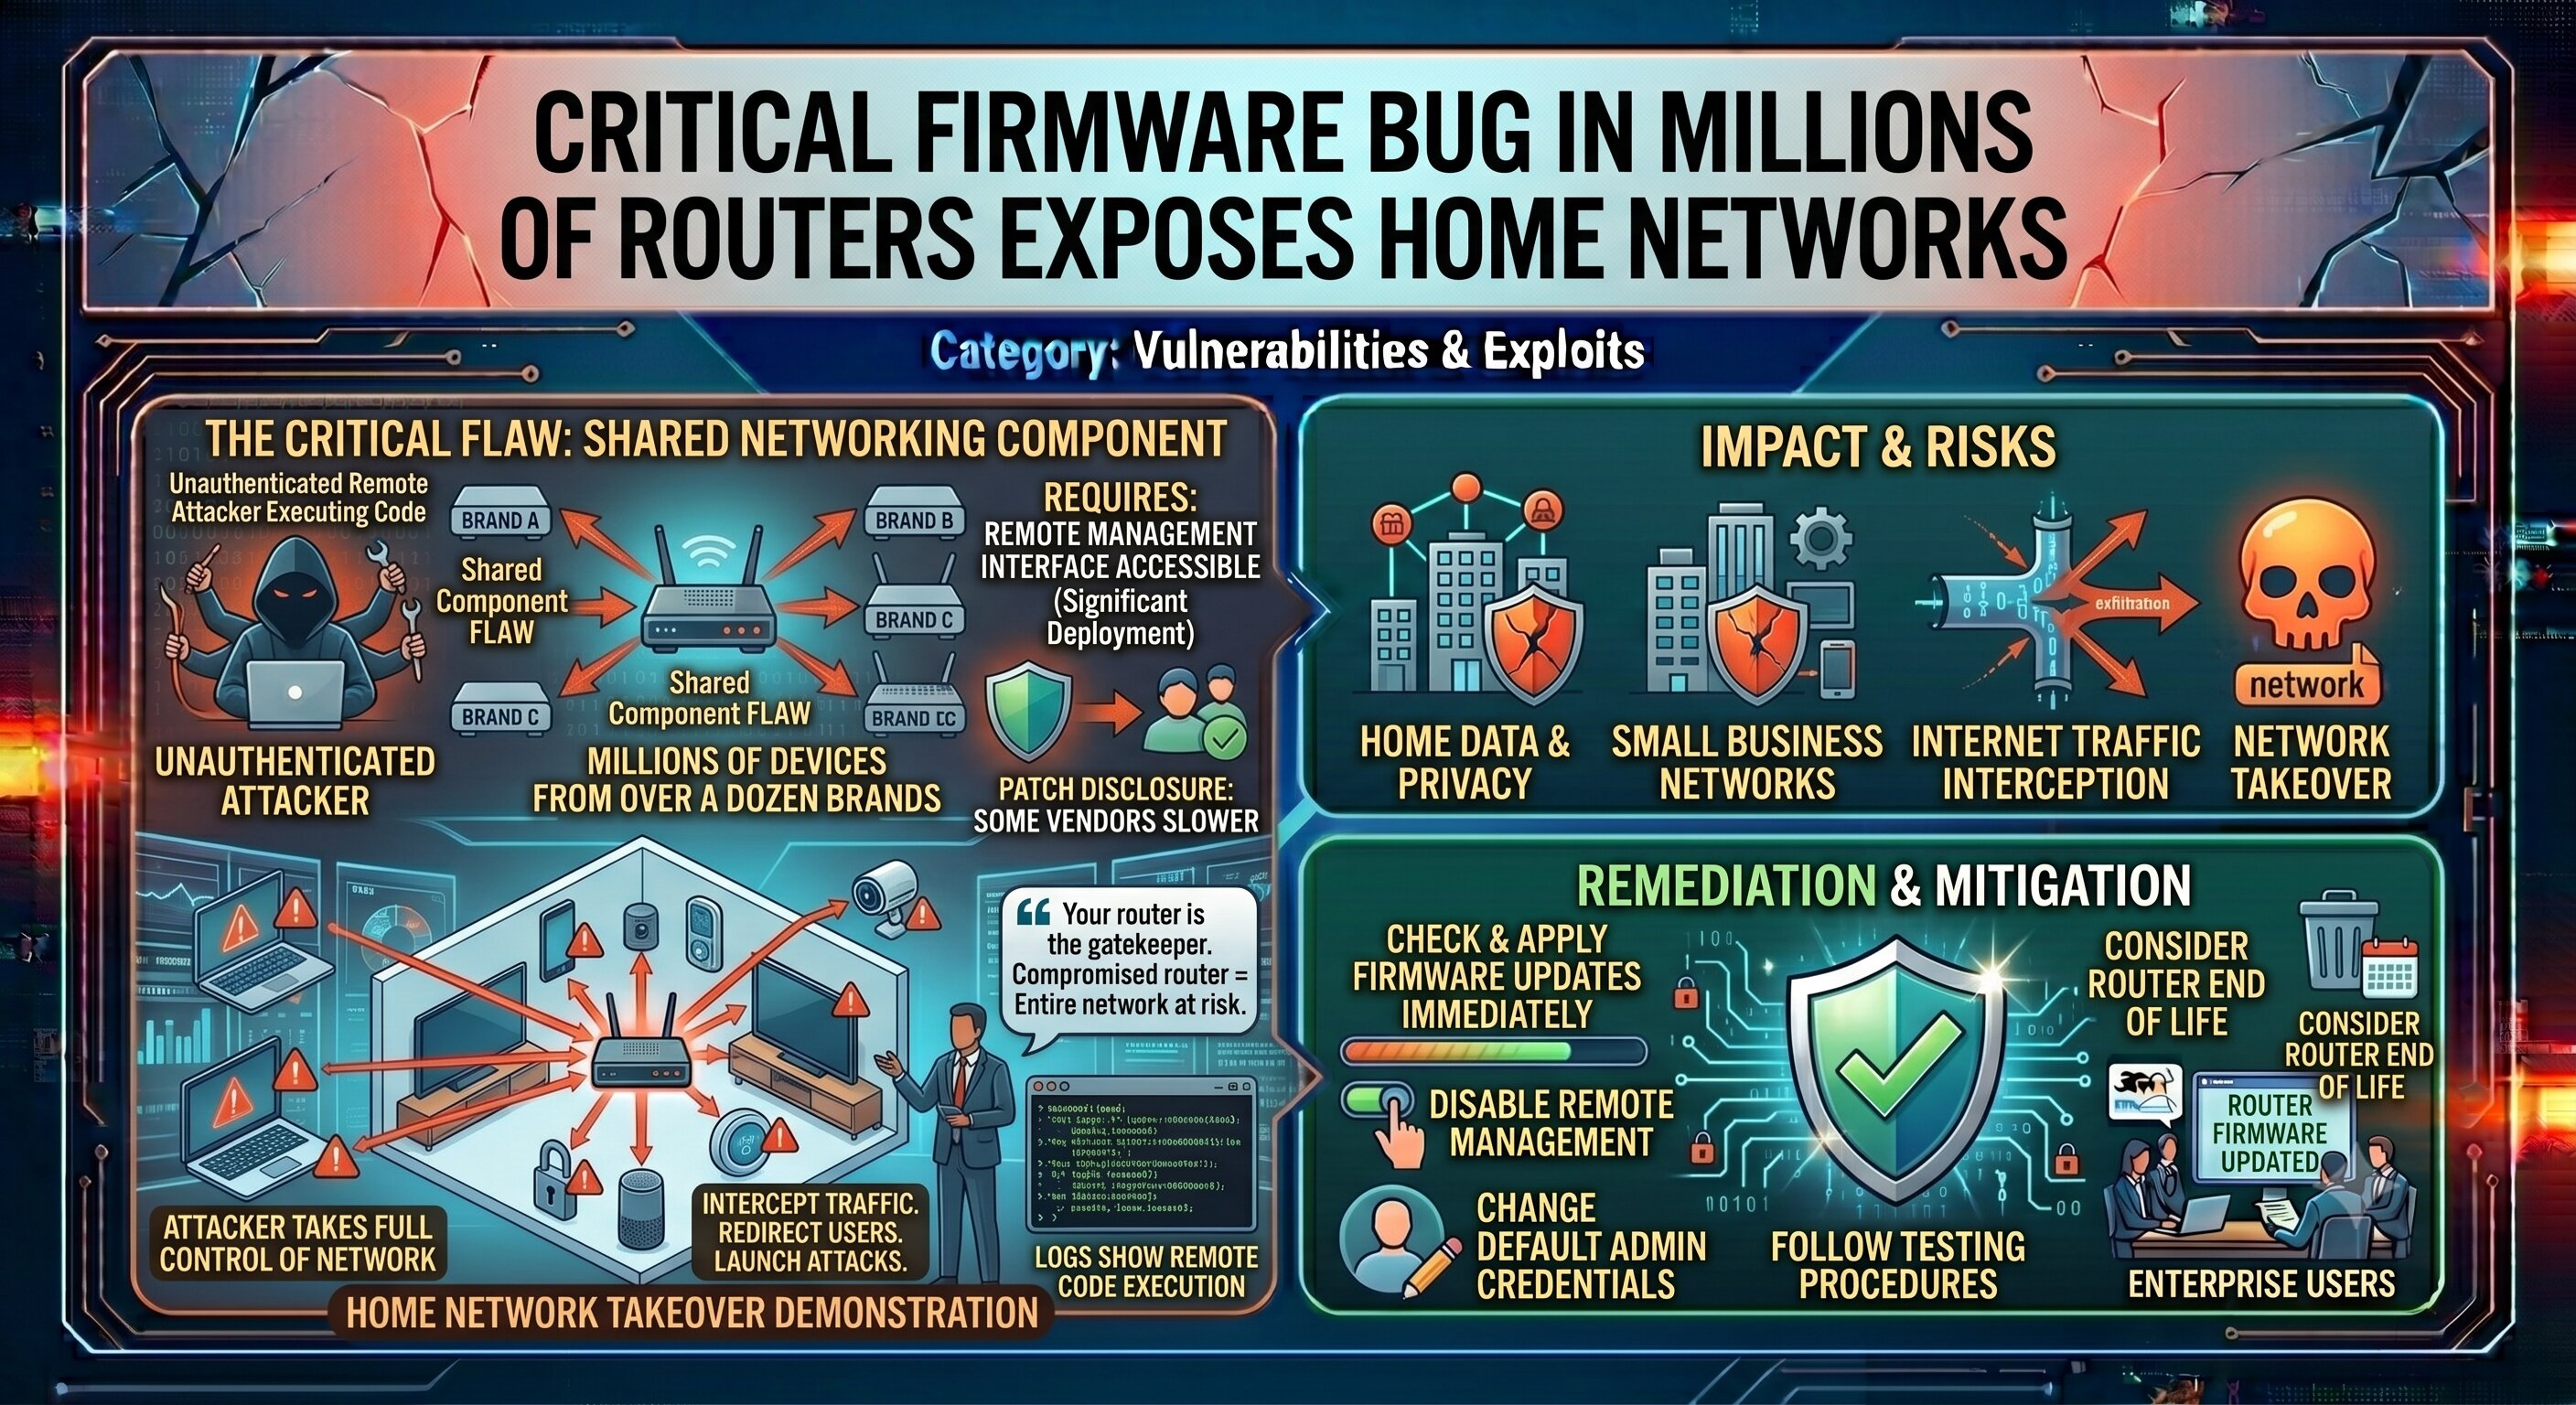
Firmware Bug in
Millions of Routers Leaves Home Networks Exposed
Category:
Vulnerabilities & Exploits
A serious
firmware vulnerability affecting millions of consumer routers from multiple
manufacturers has been publicly disclosed, potentially leaving vast numbers of
home and small business networks exposed to remote attacks. The flaw, which
exists in a shared networking component used by routers from over a dozen
brands, allows an unauthenticated remote attacker to execute arbitrary code on
the affected device and take full control of the network.
The
vulnerability was discovered during a security audit commissioned by a router
manufacturer, which then found that the affected component was licensed and
used by many other vendors. Coordinated disclosure was arranged with all
affected manufacturers, though not all vendors have released patches
simultaneously, leaving some devices still vulnerable.
Exploiting
the vulnerability requires only that the router's remote management interface
be accessible from the internet — a configuration that, according to
researchers, applies to a significant percentage of deployed devices. Once
compromised, a router can be used to intercept all network traffic, redirect
users to malicious websites, and serve as a launching point for attacks on
other networks.
"Your
router is the gatekeeper of your home network," said cybersecurity
educator Robert Chen. "If it's compromised, every device on your network —
your laptop, your phone, your smart TV — is potentially at risk."
Users with
affected routers should check their manufacturer's website for firmware updates
and apply them immediately. Additionally, users should disable remote
management if they do not need it, change default administrative credentials,
and consider whether their router model has reached end of life and may no
longer receive security updates.





Comments