Third-Party Risk Management Best Practices
Organizations today depend on an extensive ecosystem of vendors, contractors, and service providers to operate effectively, from cloud infrastructure providers and software vendors to staffing ...
Latest stories, in-depth analysis & breaking updates
Organizations today depend on an extensive ecosystem of vendors, contractors, and service providers to operate effectively, from cloud infrastructure providers and software vendors to staffing ...
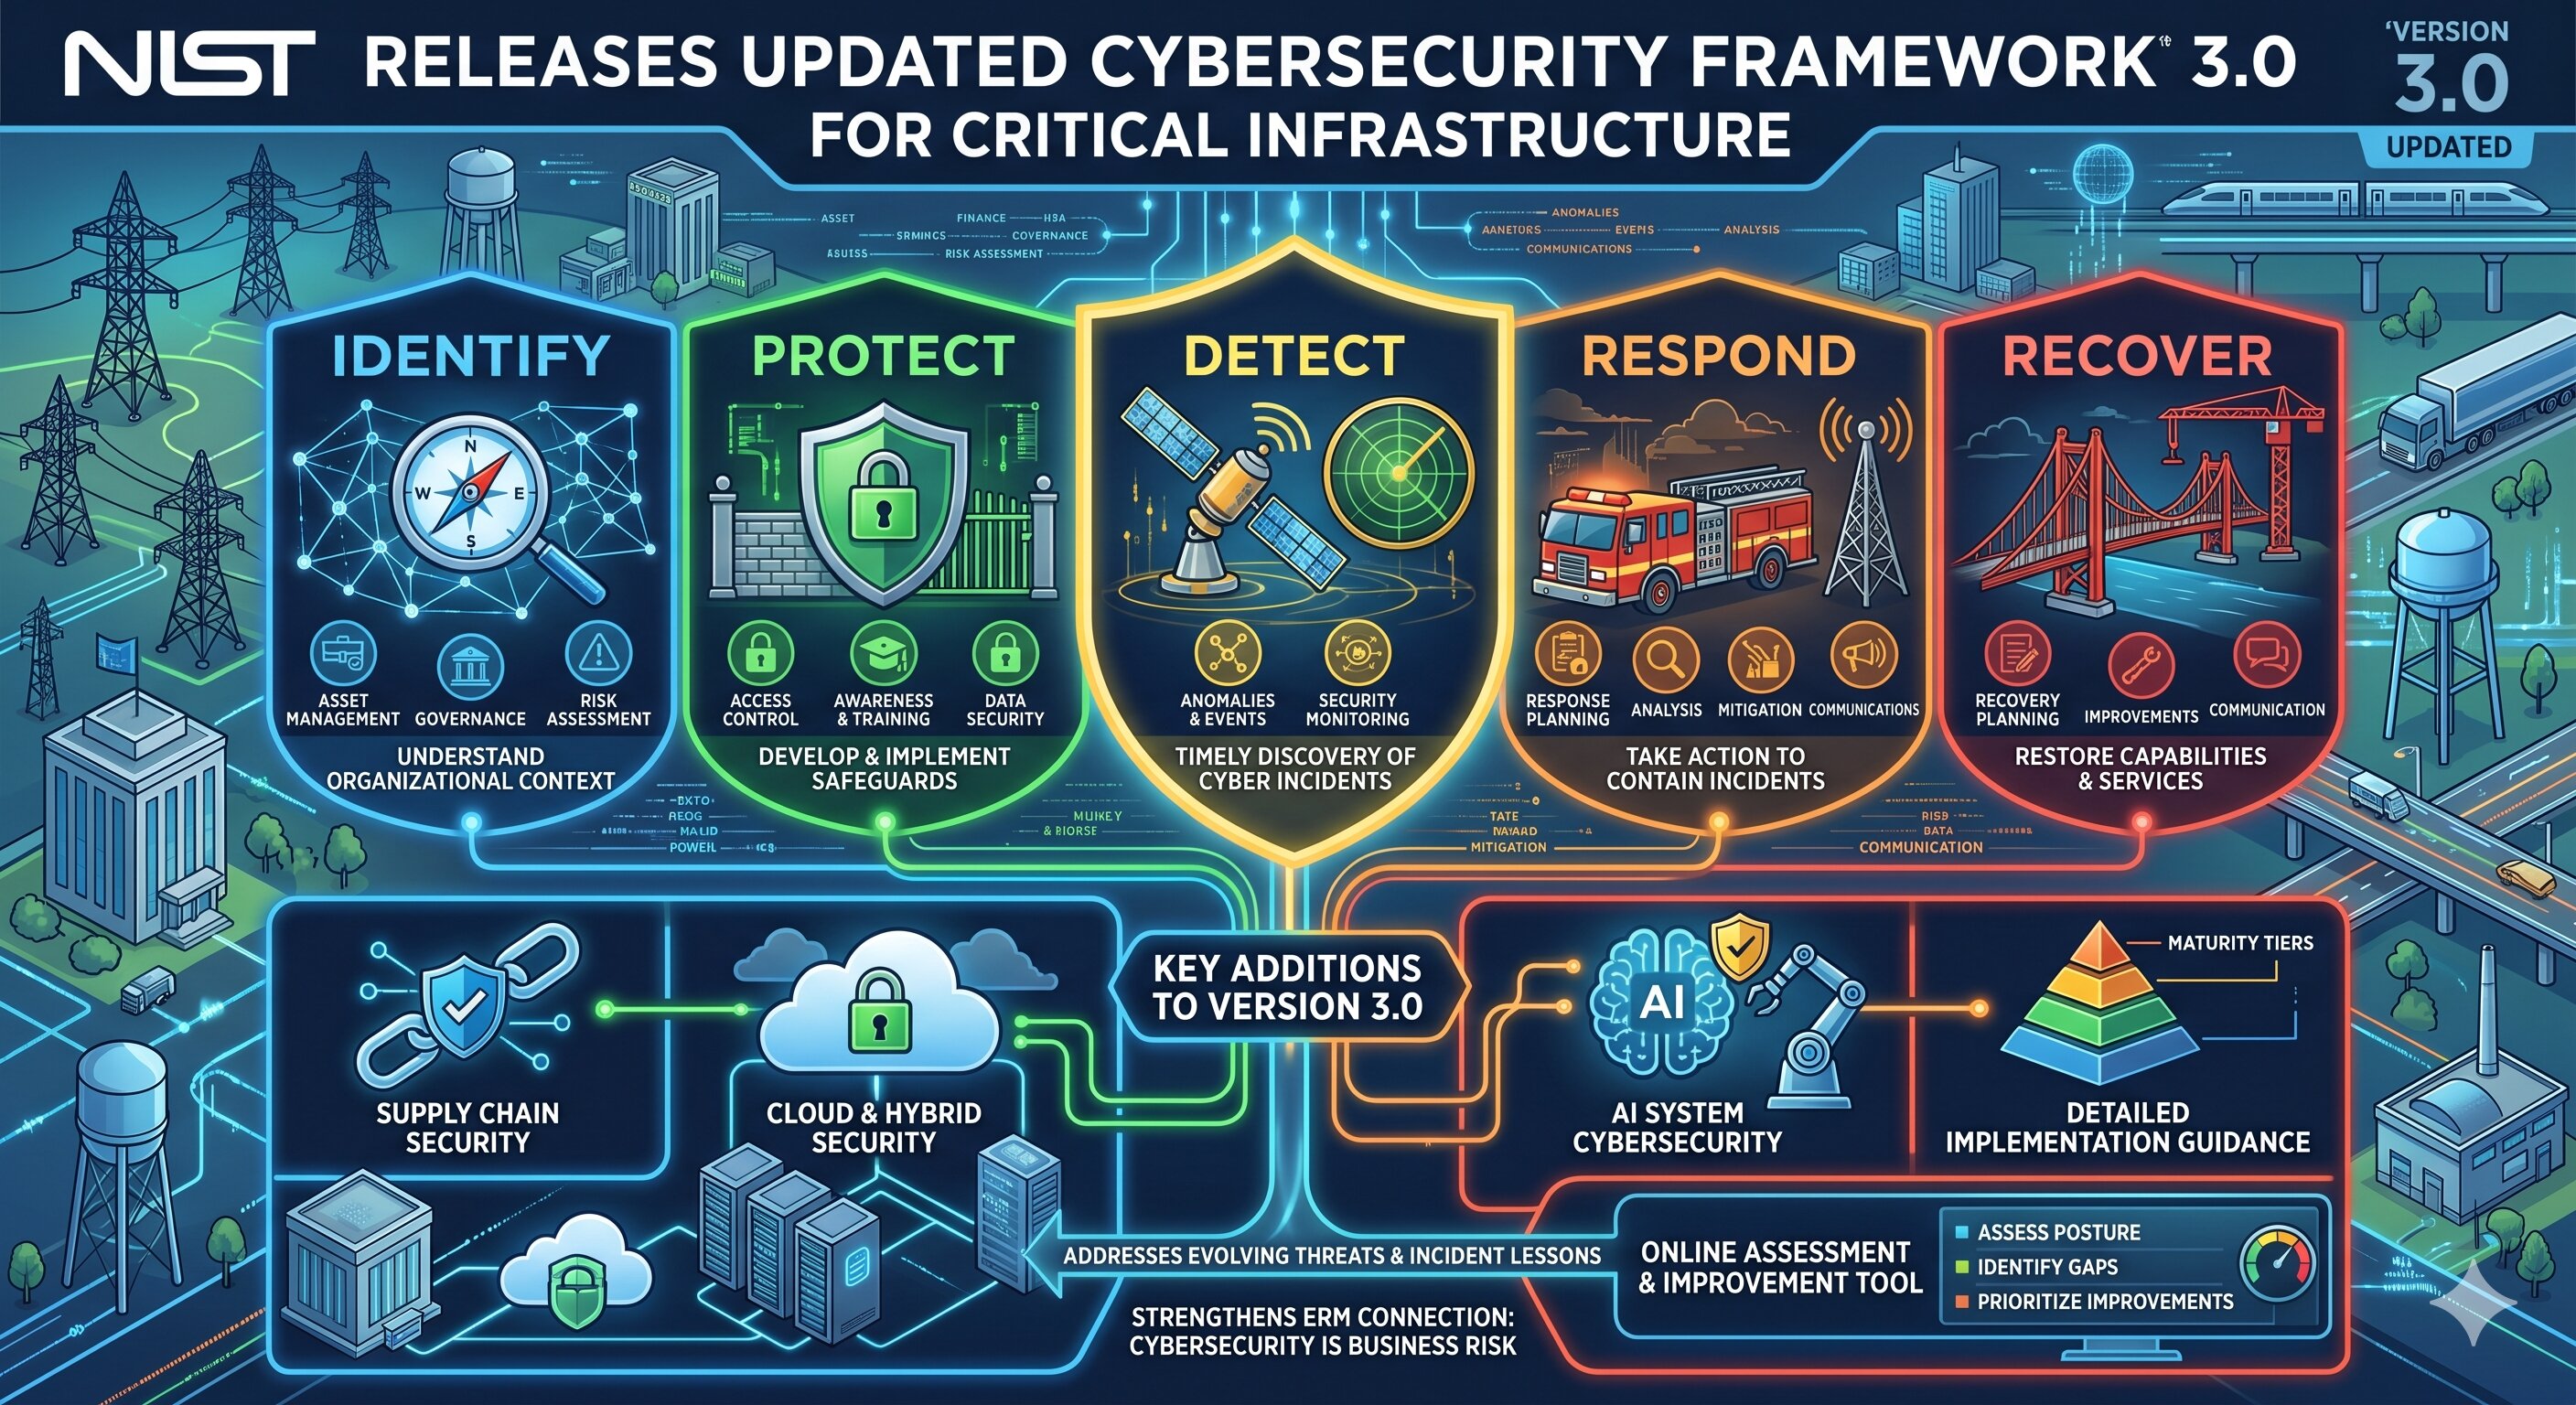
NIST Releases Updated Cybersecurity Framework 3.0 for Critical Infrastructure Category: Policy, Regulations & Industry The National Institute of Standards and Technology has published the...
The software supply chain has become one of the most attractive and devastating attack surfaces in modern cybersecurity. High-profile incidents involving widely-used software components and man...
The rapid development of AI regulation across multiple jurisdictions has created a compliance environment that cybersecurity and legal teams describe as uniquely challenging: requirements a...
The software supply chain crisis has elevated the Software Bill of Materials from an obscure concept in software engineering to a mainstream security and compliance requirement. Government mand...
Incident Response Planning: How to Survive a Cyberattack Before It Happens Introduction The security industry often repeats a sobering maxim: it is not a question of whether your organiz...