The Future of Passwordless Authentication
Passwords have represented the dominant authentication mechanism for digital systems for decades, but their fundamental weaknesses, including vulnerability to phishing, reuse across multiple ac...
Latest stories, in-depth analysis & breaking updates
Passwords have represented the dominant authentication mechanism for digital systems for decades, but their fundamental weaknesses, including vulnerability to phishing, reuse across multiple ac...
Mobile Security Under Siege: Banking Trojans and Stalkerware Target Smartphone Users Globally Mobile devices have become the primary computing platform for billions of users, and cybercrimin...
VRChat Data Breach Exposes 2.4 Million Users' Personal Data VRChat, Inc. has filed a formal data breach notification revealing that the personal information of more than 2.4 million users was...
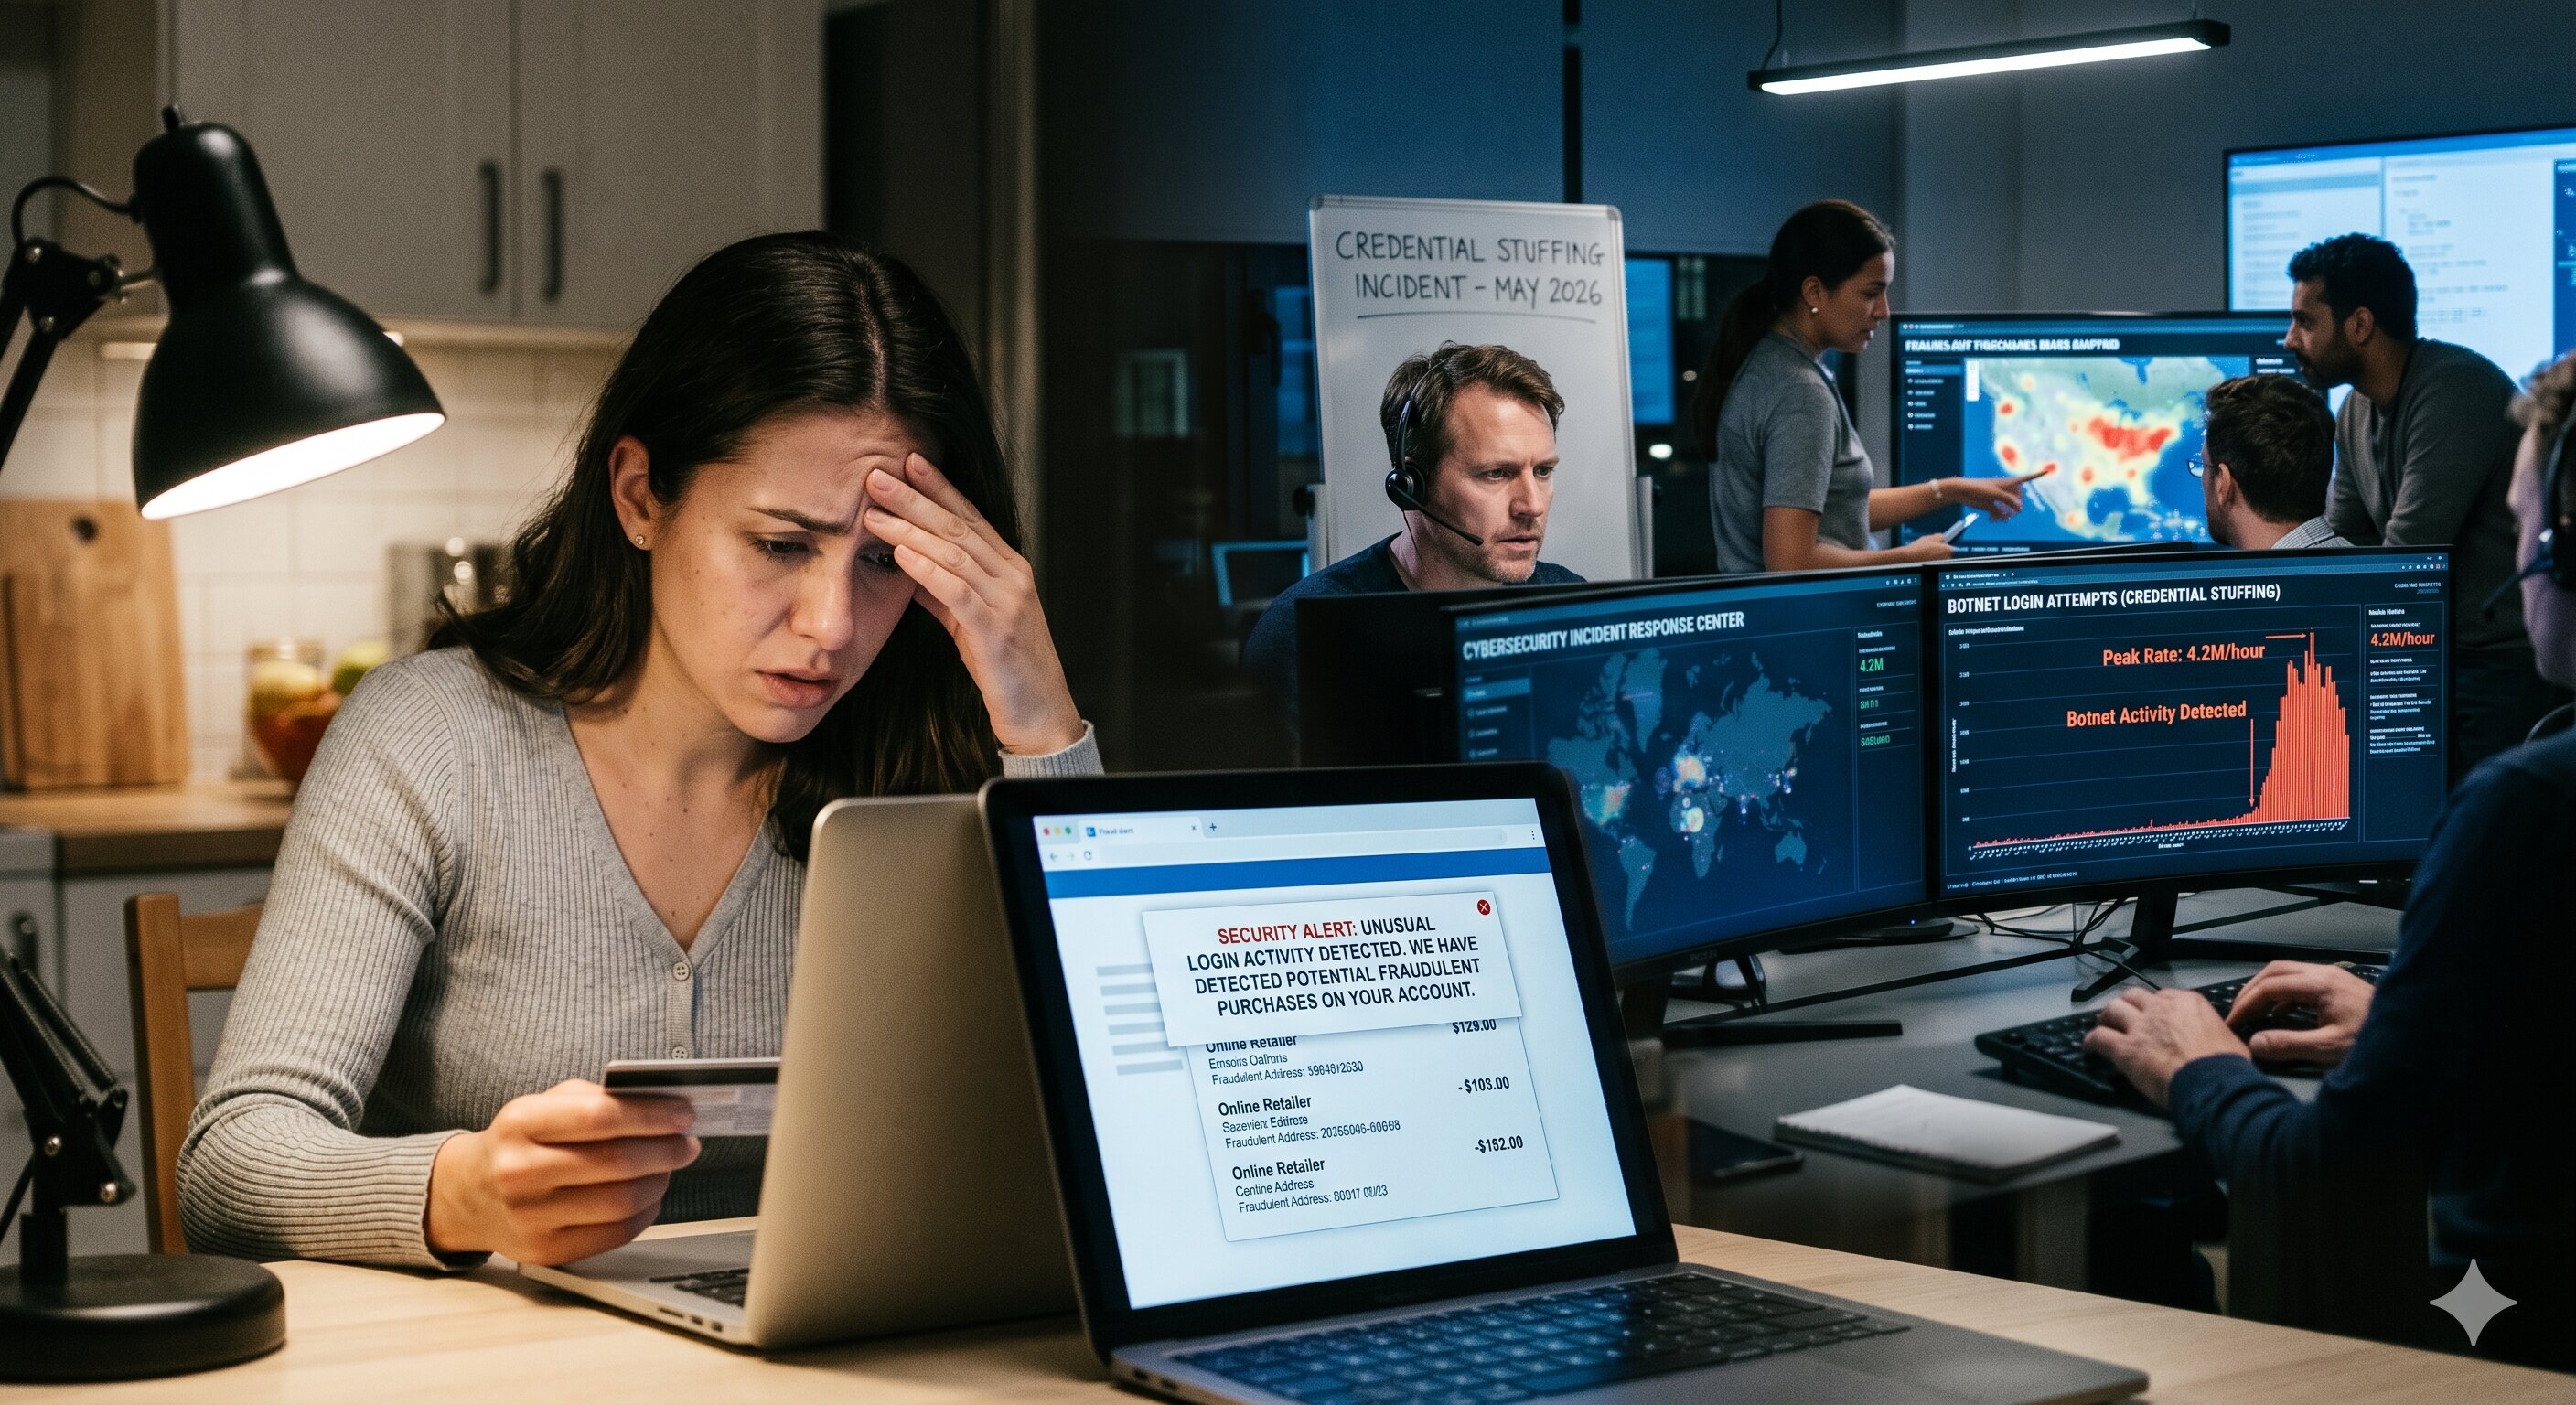
Credential Stuffing Attack Exposes 10 Million User Accounts Category: Threats & Attacks A large-scale credential stuffing attack has compromised approximately 10 million user accounts ac...
Privileged accounts, including system administrator credentials, database administrator access, and other elevated permission sets that grant broad control over critical systems and sensitive d...
Despite years of security industry advocacy for stronger authentication practices, password-based credentials remain the foundation of access control for the vast majority of online services, a...
In an era where the network perimeter has dissolved and users access corporate resources from everywhere using every type of device, identity has emerged as the new security perimeter. Identity...
Technical security controls have advanced dramatically over the past decade, making direct exploitation of software vulnerabilities increasingly difficult and expensive for attackers. In respon...
The traditional castle-and-moat approach to network security — where everything inside the perimeter is trusted and everything outside is suspect — is dead. In an era of cloud computing, remote...